The criteria in use today are the AICPA's 2017 Trust Services Criteria, with revised points of focus published in 2022. The 2022 revision updated the points of focus but did not change the criteria themselves [2].
The five categories
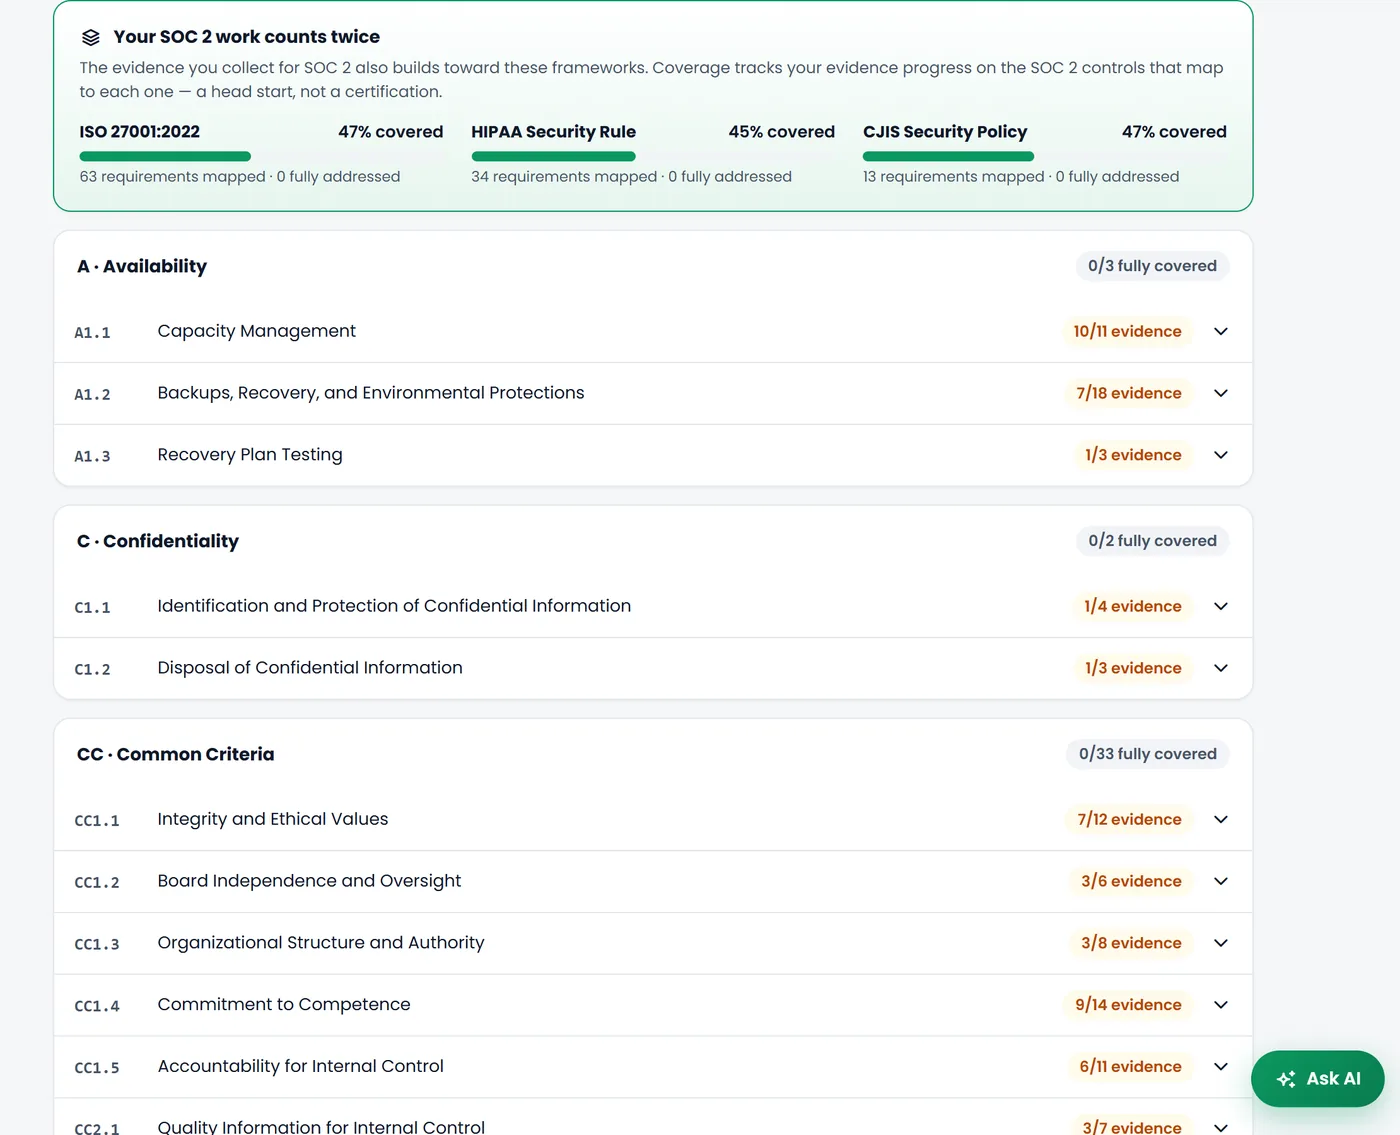
| Category | What it covers | Included when |
|---|---|---|
| Security | Protection of information and systems against unauthorized access and damage | Always: it is the common criteria |
| Availability | Systems are available for operation and use as committed | You make uptime commitments to customers |
| Processing integrity | Processing is complete, valid, accurate, timely and authorized | You process transactions or data for customers |
| Confidentiality | Information designated as confidential is protected | You handle customer confidential data |
| Privacy | Personal information is collected, used, retained and disposed of properly | You handle personal information for customers |
The common criteria (CC1 to CC9)
- CC1 Control environment
- CC2 Communication and information
- CC3 Risk assessment
- CC4 Monitoring activities
- CC5 Control activities
- CC6 Logical and physical access controls
- CC7 System operations
- CC8 Change management
- CC9 Risk mitigation, including vendor and business partner risk
CC1 to CC5 follow the structure of the COSO internal control framework; CC6 to CC9 add criteria specific to technology and security.
How to choose your scope
Start with Security. Add another category only when customers or contracts call for it, because each one adds controls to operate and evidence to collect. Your CPA firm will confirm the scope with you.
Frequently asked questions
How many Trust Services Criteria are there?
There are five categories: security, availability, processing integrity, confidentiality and privacy. Security, also called the common criteria, is included in every SOC 2 report.
Are all five categories required?
No. Only security is required. The others are included when they are relevant to the services you provide.
What changed in 2022?
The AICPA revised the points of focus that help apply the criteria, for example around changing technology and privacy. The 2017 criteria themselves did not change.
Related
SOC 2 Type 1 vs Type 2
Which report you need, and when. On SOC2Compliance.com.
How much SOC 2 costs
A full SOC 2 budget breakdown. On SOC2Compliance.com.
SOC 2 readiness checklist
The control-by-control checklist. On SOC2Compliance.com.