The HIPAA Security Rule requires a risk analysis (45 CFR 164.308(a)(1)(ii)(A)). The HHS Security Risk Assessment (SRA) Tool is the most widely used free question set for doing it. soc2audit.ai builds on that question set and turns it into a living part of your compliance program.
What you get
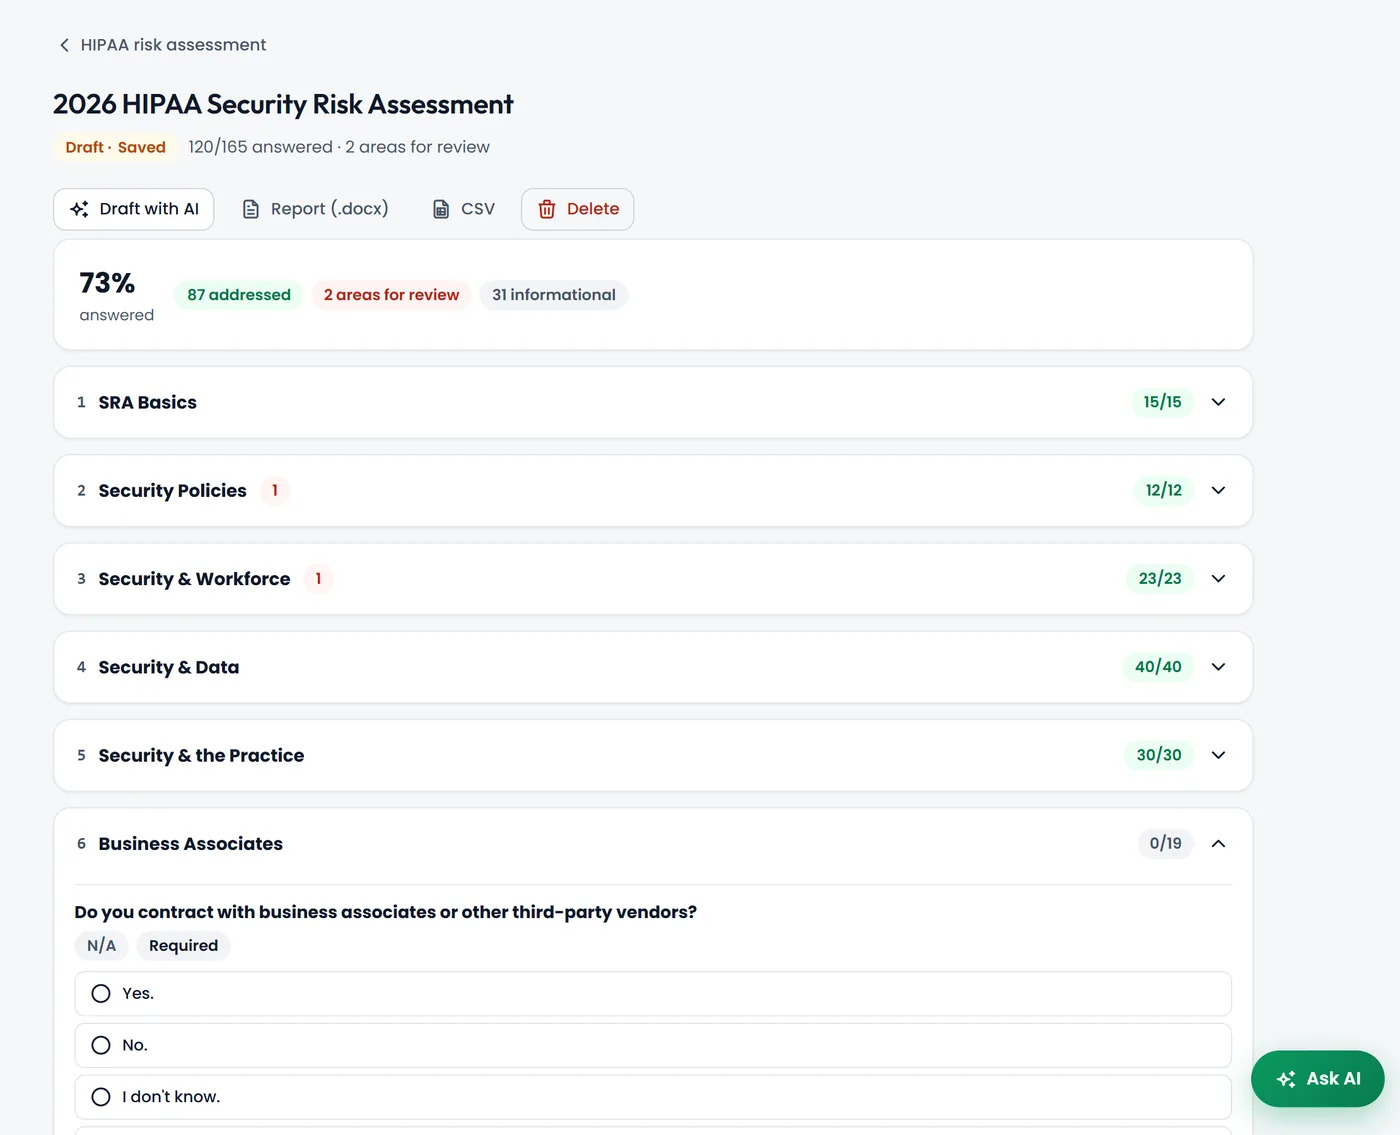
The full SRA question set
All 7 sections and 165 questions from version 3.6.1 of the HHS SRA Tool, each with its education text, HIPAA citation and Required or Addressable status.
AI-drafted answers
The AI drafts answers from your company profile and skips what it cannot know, so you review and correct rather than start from a blank page.
A real risk rating
Every area for review can be rated for likelihood and impact on the SRA risk matrix: Low, Moderate, High or Critical.
A signed report
Sign off and export a .docx report and a CSV, then attach it to your evidence. The assessment is tracked on an annual cadence.
BAA tracking
Mark vendors as business associates and track whether each BAA is signed, pending or not required, with gaps flagged.
Breach and incident log
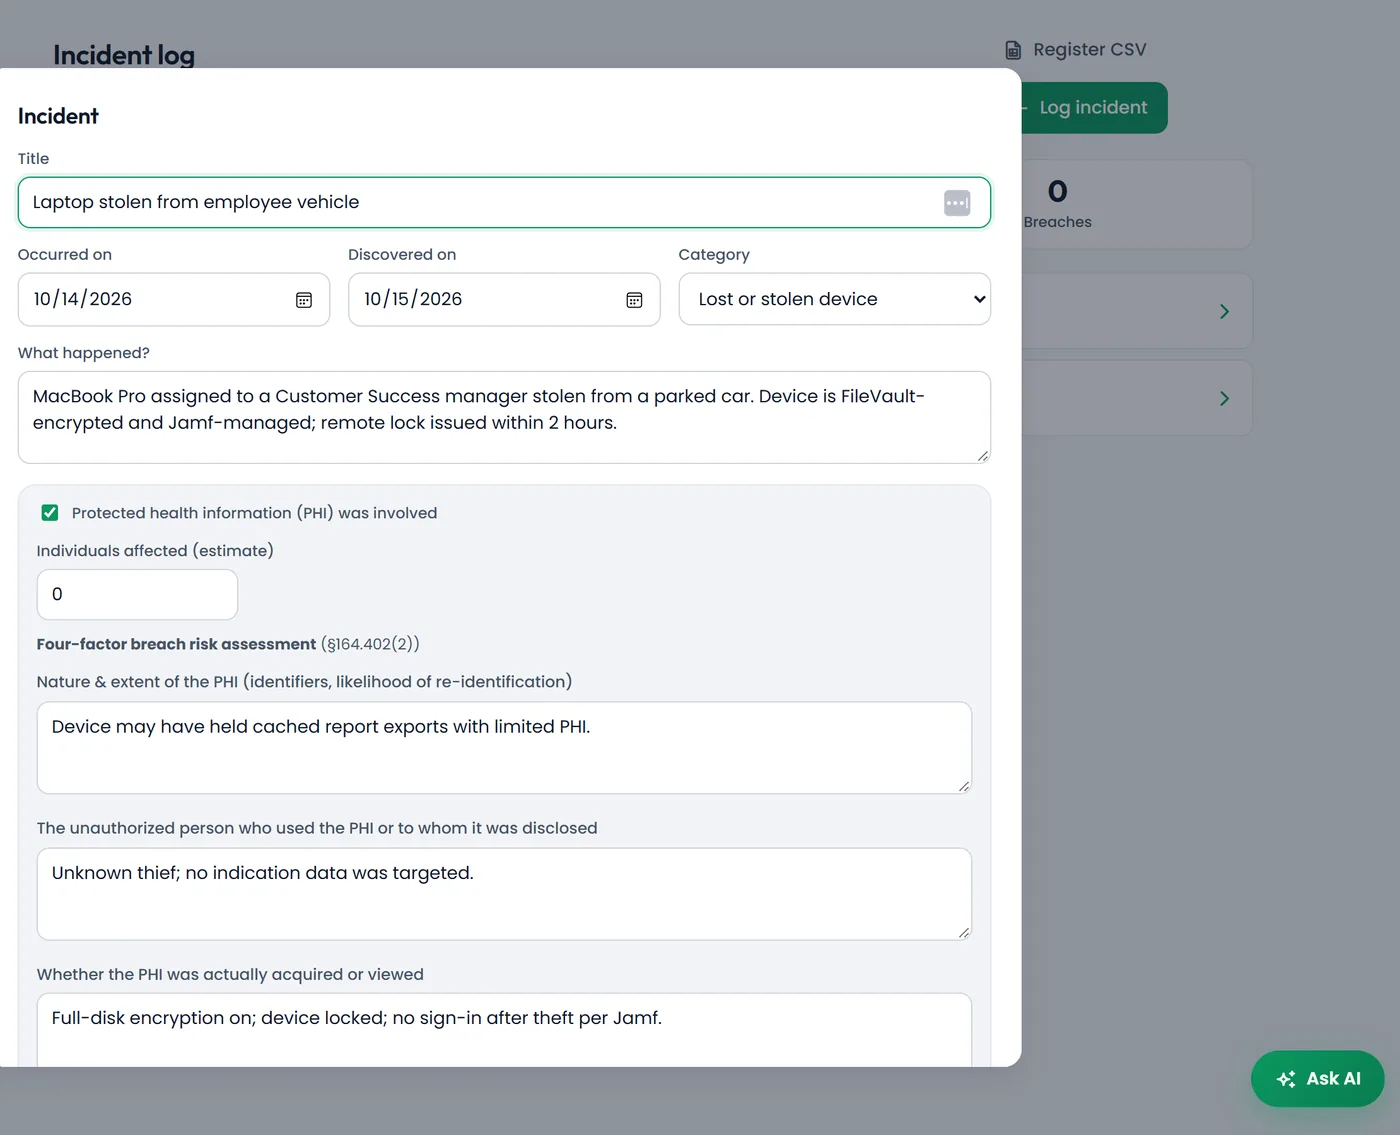
Log incidents with the HIPAA four-factor breach risk assessment and track individual, HHS and media notification dates.
HIPAA and SOC 2 in one program
Healthcare companies are often asked for both. In soc2audit.ai, the HIPAA risk assessment, BAA tracking, incident log and HIPAA policy templates (security, privacy and breach, and business associate management) sit next to your SOC 2 work, and SOC 2 controls are mapped to the HIPAA Security Rule so evidence carries over.
Frequently asked questions
Is a HIPAA risk assessment required?
Yes. The HIPAA Security Rule requires covered entities and business associates to conduct an accurate and thorough assessment of the potential risks and vulnerabilities to electronic protected health information (45 CFR 164.308(a)(1)(ii)(A)), and to review it periodically.
Is this the official HHS SRA Tool?
No. soc2audit.ai uses the question set published with the HHS Security Risk Assessment Tool, version 3.6.1, and adds AI drafting, a risk matrix, sign-off and reporting. soc2audit.ai is not affiliated with or endorsed by HHS.
How often should we repeat it?
HIPAA requires periodic review, and most organizations repeat the assessment at least annually and whenever their environment changes significantly. soc2audit.ai tracks an annual cadence and flags overdue assessments.
Does completing it make us HIPAA compliant?
No single assessment makes you compliant. It identifies risks you then need to address with safeguards, policies and ongoing monitoring, which the rest of the platform helps you track.
Related
Security questionnaires
Answer customer questionnaires from your own program data.
User access reviews
HR-matched access reviews with sign-off and a working paper.
Vendor risk management
Risk-tier vendors and let AI analyze their SOC 2 reports.