The step-by-step platform that walks you through every phase of your SOC 2 program from gap assessment to signed report with an AICPA-licensed audit partner engaged inside the platform.
A product of Cybersecurity Services, LLC
60–90 minutes
AI-Guided Gap Assessment
Answer ~100 AI-guided questions about your systems, people, and processes. The copilot produces a plain-English gap report mapped to the AICPA Trust Services Criteria, so you know exactly where you stand before you spend a dollar on remediation.
Weeks, not months
AI-Guided Remediation Far More Than Policies
Remediation isn’t just writing policies. soc2audit.ai closes real operational controls for you.
Policies: the AI drafts every policy for your business, inserts effective dates, and routes them to you for one-click approval. Your policy register builds itself.
Risk register: pre-populated with risks derived from your gap assessment, mapped to the controls they affect. No blank spreadsheet.
User access reviews: upload or pull each system’s user list and compare it with your HR roster. Former employees, unknown accounts and shared accounts are flagged; you keep, modify or revoke each one and sign off. What used to take a day of spreadsheet work is now a review session.
Vendor risk reviews: add your vendors and each one is tiered by the data it holds and how critical it is, with BAAs tracked. Upload a vendor’s SOC 2 report and the AI reviews it for the risks you actually need to know about. Hours of vendor chasing collapsed into an afternoon.
Connected checks: read-only connections to AWS, GitHub, Microsoft 365, and Okta keep evidence current while you focus on the work only you can do.
What used to be months of consultant hours is now a series of review sessions.
When you need them
Optional Services from Cyber Security Services
Penetration testing, vulnerability management, and virtual CISO, delivered by our parent company, Cyber Security Services. Surfaced inside the platform when you need them. Never bundled. Never required. Priced per engagement so you only pay for what you use.
Type I or Type II ready
AI-Guided Evidence Collection
Every fix you made in Gap Assessment and Remediation is attached as evidence, with no re-uploading and no re-explaining. For SOC 2 Type I (point-in-time) or Type II (observation period), the AI tells you exactly what remaining evidence to add, in what format, mapped to each control.
Auditor sets timeline
Managed Audit with an AICPA Partner
An AICPA-licensed CPA firm from our pre-vetted partner network runs your audit inside the platform. Real-time visibility into what the auditor has accepted, what’s still outstanding, and what needs your attention. No email chains. No “did you get my last file?” No side-channel document exchange.
Vendor risk, done in an afternoon.
Add your vendors and see who holds your sensitive data, who is business-critical and who is missing a BAA. Upload a vendor's SOC 2 report and the AI writes a security review that flags what needs follow-up, ready for your auditor.
Not just audit prep. A basic GRC program that runs all year, with an AI copilot that knows where you stand.

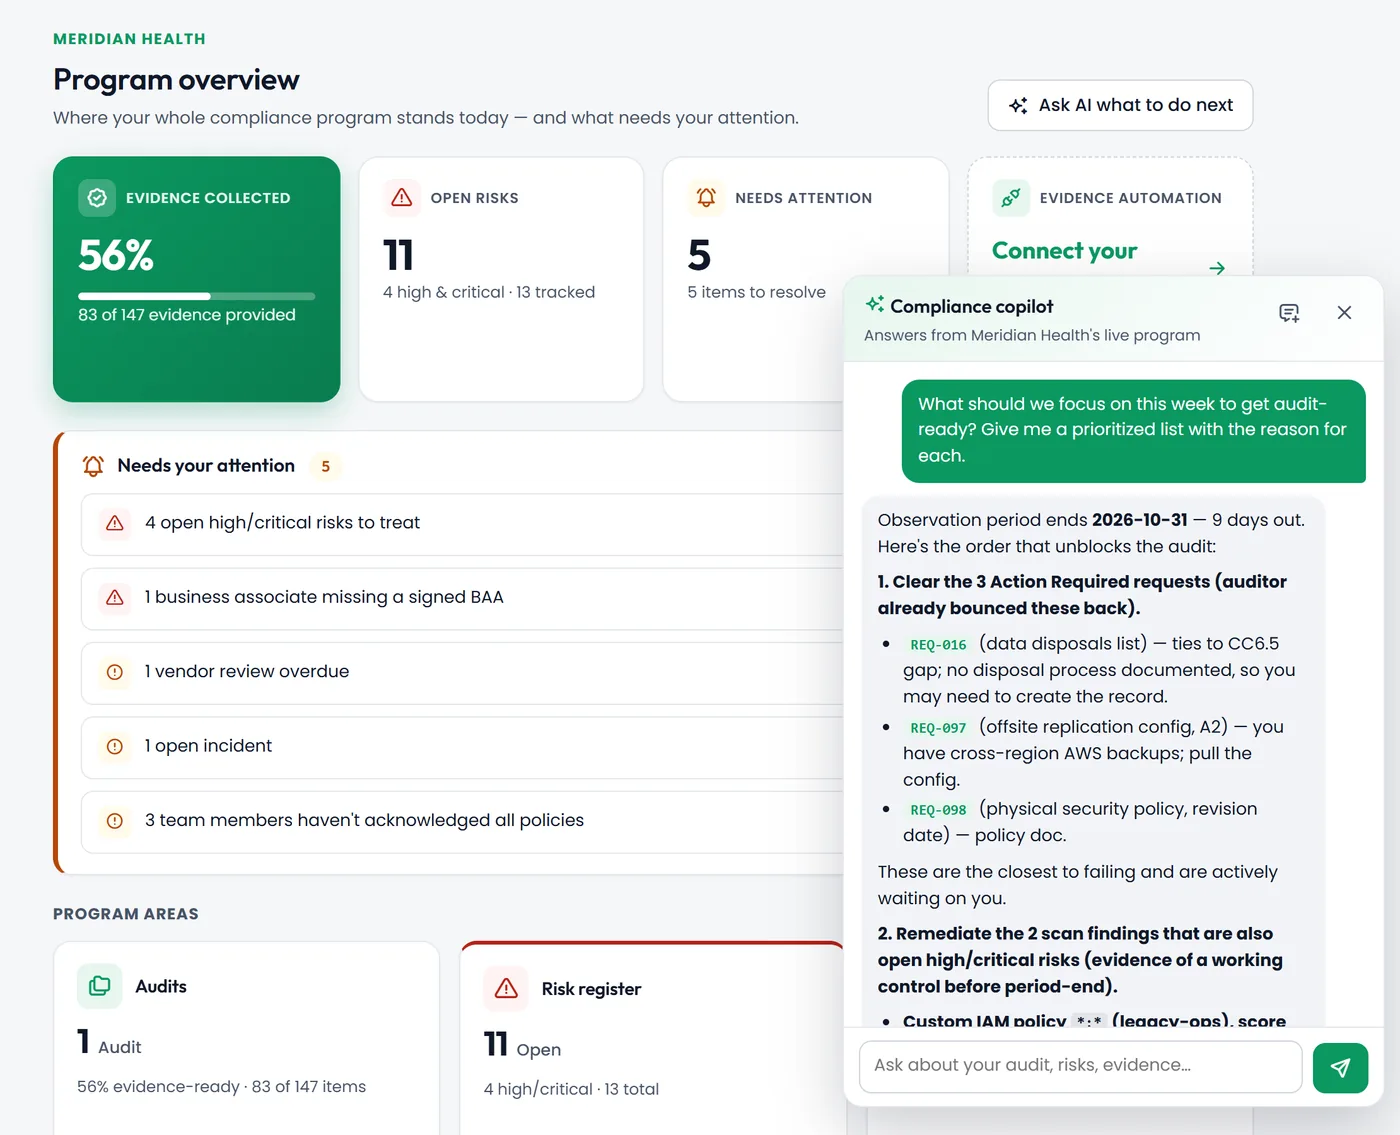
AI copilot
A copilot on every page that answers from your live data: what is blocking the audit, what the auditor sent back, which risks matter most.
Prioritized plans, status updates for leadership, answers that stream in
See it in the product tour →
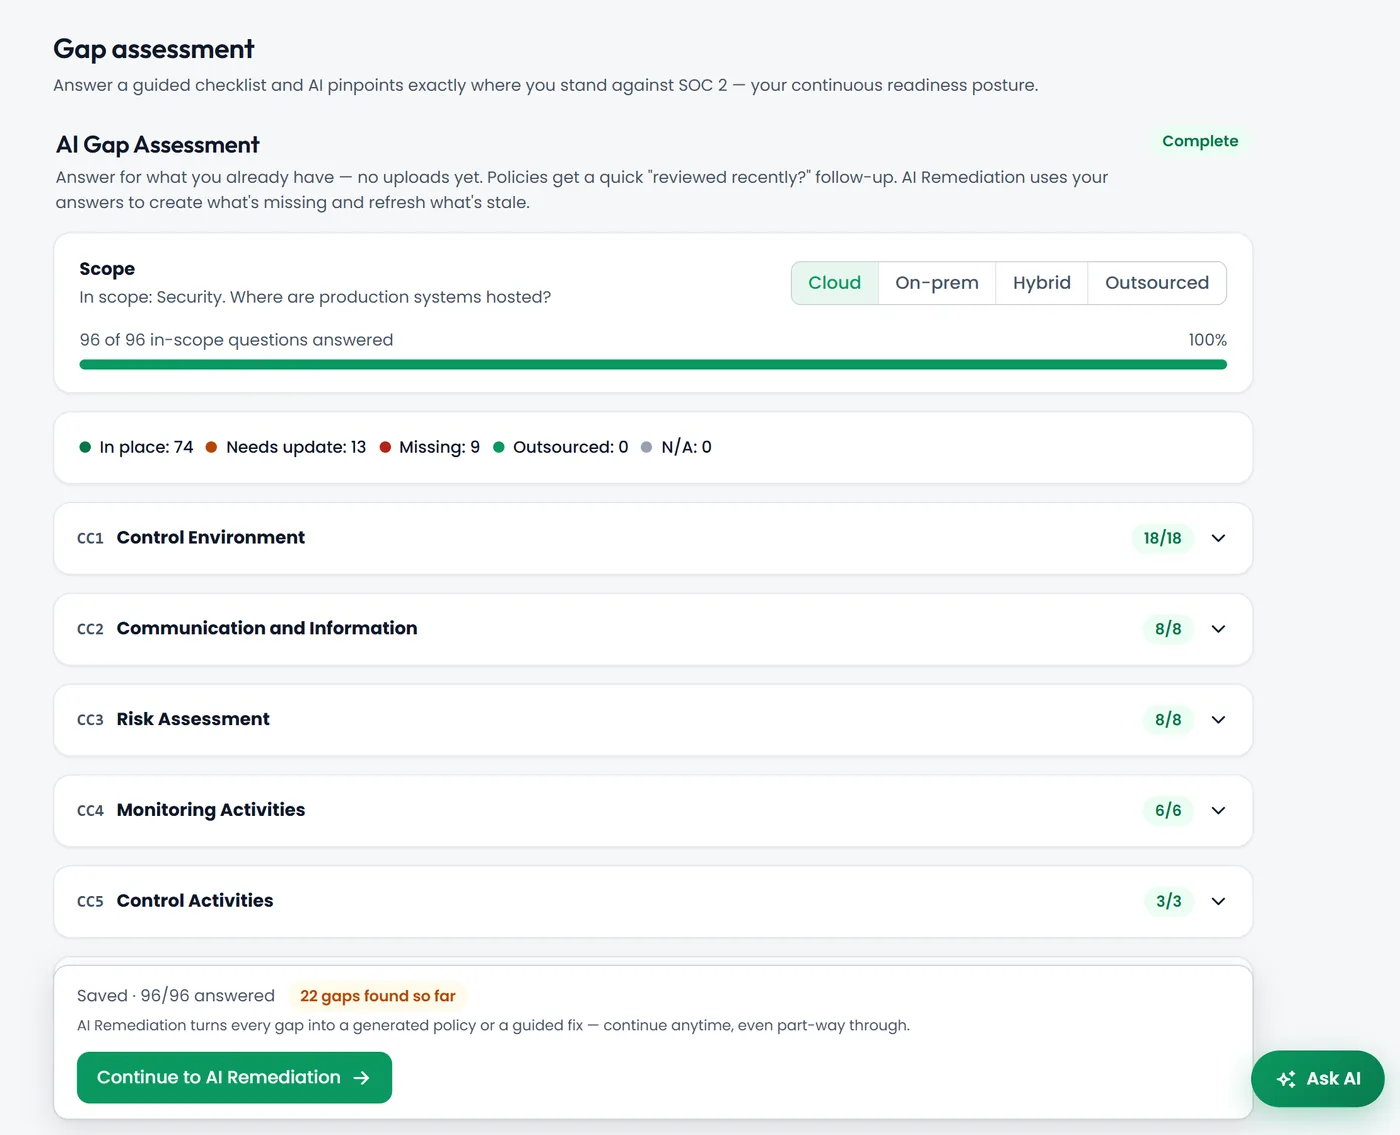
Readiness
An AI-guided gap assessment, policies and plans written for your stack, and a controls map that shows your ISO 27001, HIPAA and CJIS coverage too.
Gap assessment, Remediation, Controls map
See it in the product tour →
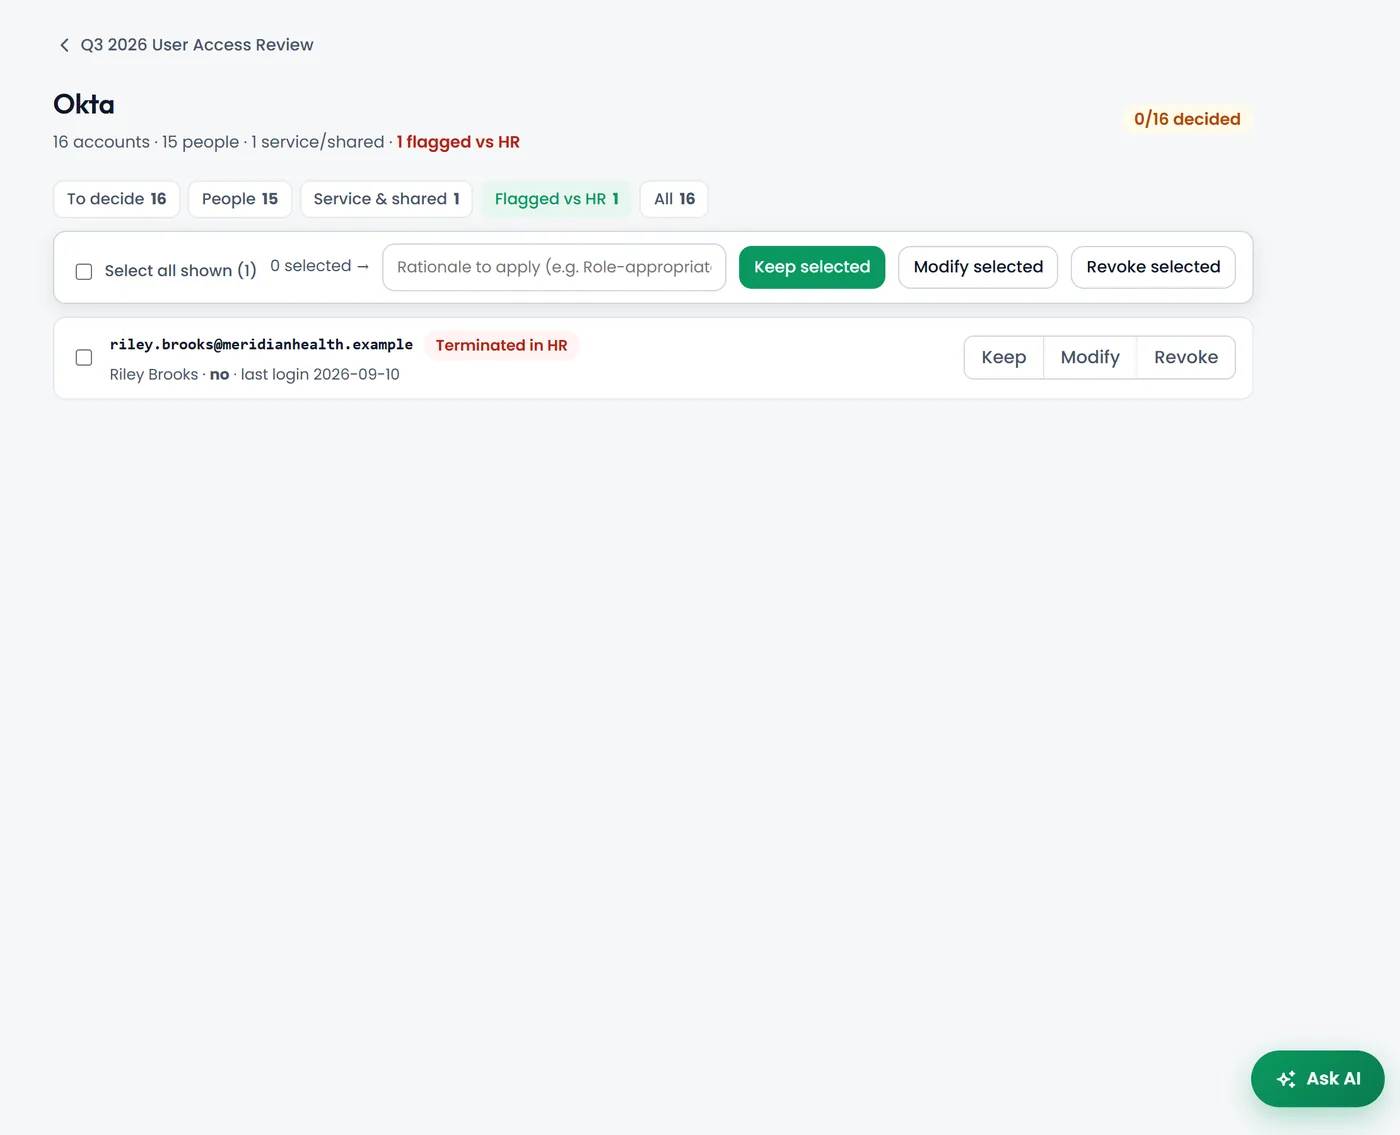
Governance
The GRC work auditors ask about, built in: risks, risk assessments, access reviews, vendor risk, scans, incidents, continuity and customer questionnaires.
Risk register, Risk assessments, HIPAA risk assessment, User access review, Security reviews, Vulnerability scans, Questionnaires, Business continuity, Incident log, Vendor Risk, Integrations
See it in the product tour →
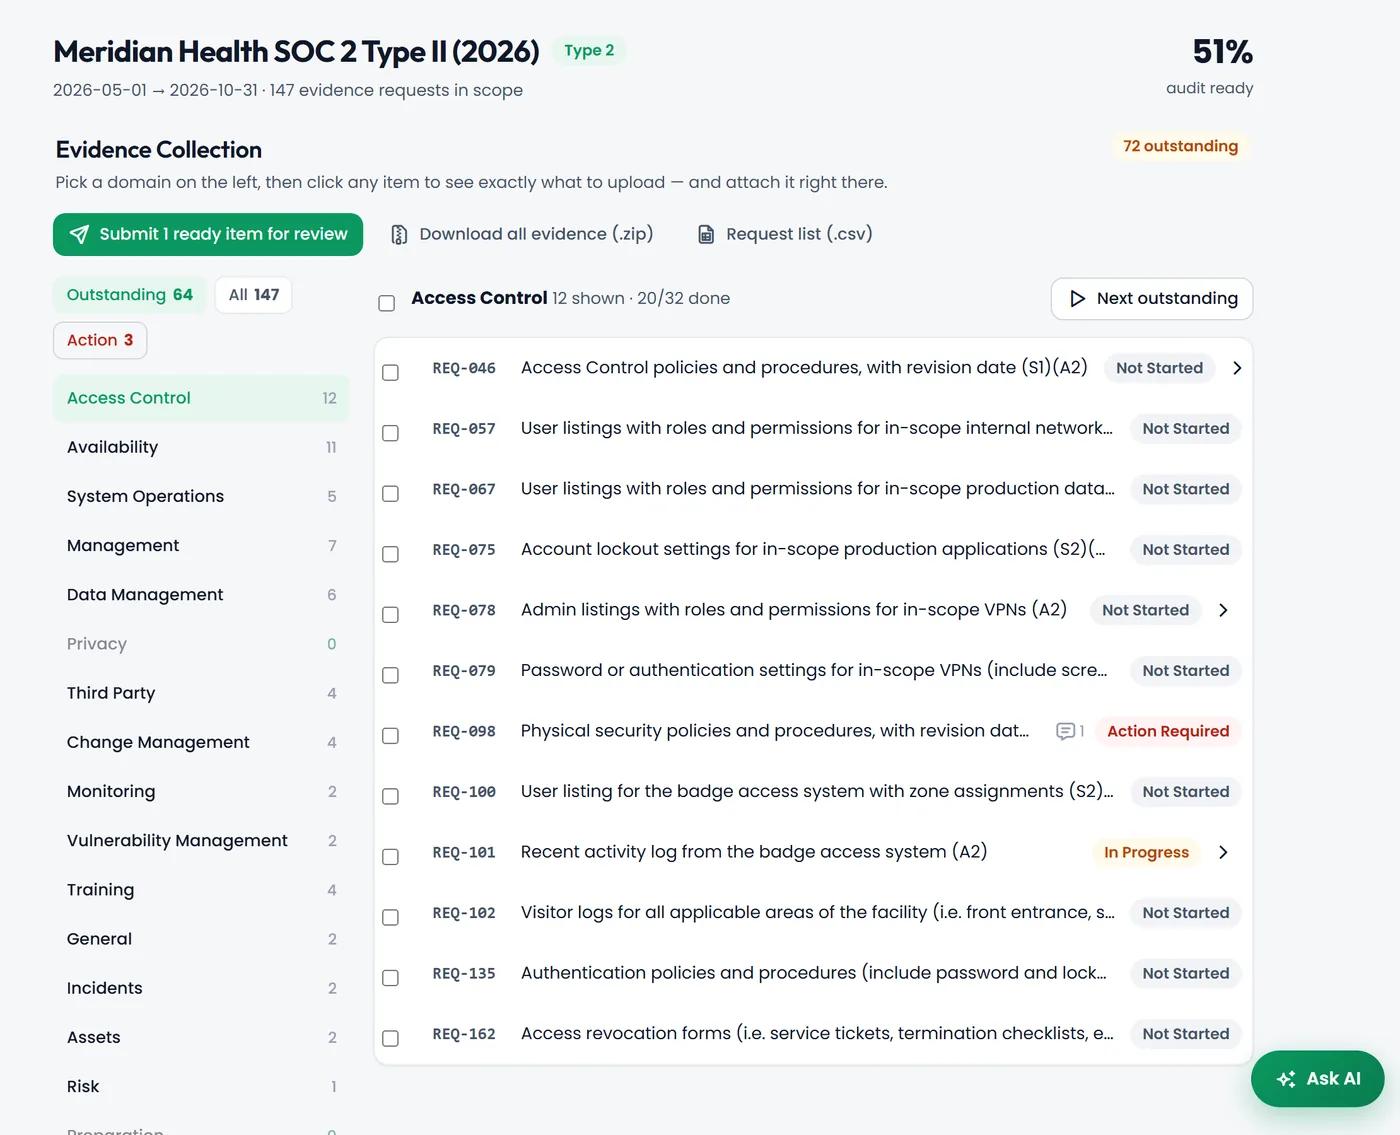
Audit
Every evidence request organized with owners and status, and an AICPA-licensed CPA firm reviewing, commenting and accepting inside the platform.
Evidence, Review thread, Managed audit, Auditor's view
See it in the product tour →
You do not need a compliance manager to use the platform. If you can answer questions about how your business works, the AI can tell you what to do next.
Not generic templates you have to fill in. The AI reads your environment and generates policies that reflect how you actually operate.
Our AICPA-licensed partner firms work inside soc2audit.ai. No shared drives, no email chains, no scrambling for evidence at the last minute.
Need a penetration test or a virtual CISO? Cyber Security Services provides those under a separate engagement. Never bundled, never required.
One annual subscription with every module included. No per-user pricing, no per-framework upsells.
Reach the sub-$15K startup segment that traditional GRC platforms price out, expanding your addressable market without cannibalizing enterprise work.
soc2audit.ai is a product of Cybersecurity Services, LLC (Cyber Security Services), a CISSP-led firm that has delivered SOC 2, HIPAA, CMMC, and penetration testing engagements to clients ranging from healthcare startups to Fortune 500 enterprises. Our team has led security programs at some of the largest firms in the United States.
We built soc2audit.ai because we watched too many of our own clients pay for GRC platforms that left them to figure out what to do next. We knew what a good SOC 2 program actually required, because we have guided clients through it for years. So we built the tool we wished existed.