Product

An AI copilot for your entire SOC 2 program.

From your first gap assessment to your signed audit report, soc2audit.ai walks you through five phases. Every step has an AI assistant. The audit is delivered by a real AICPA-licensed CPA firm.

Inside the platform

Every module, straight from the menu.

Tour the real product: the AI copilot, readiness, year-round governance and the audit itself. Modules marked AI have AI drafting the work for you to review.

Overview
Readiness
Governance
Audit
Company
app.soc2audit.ai
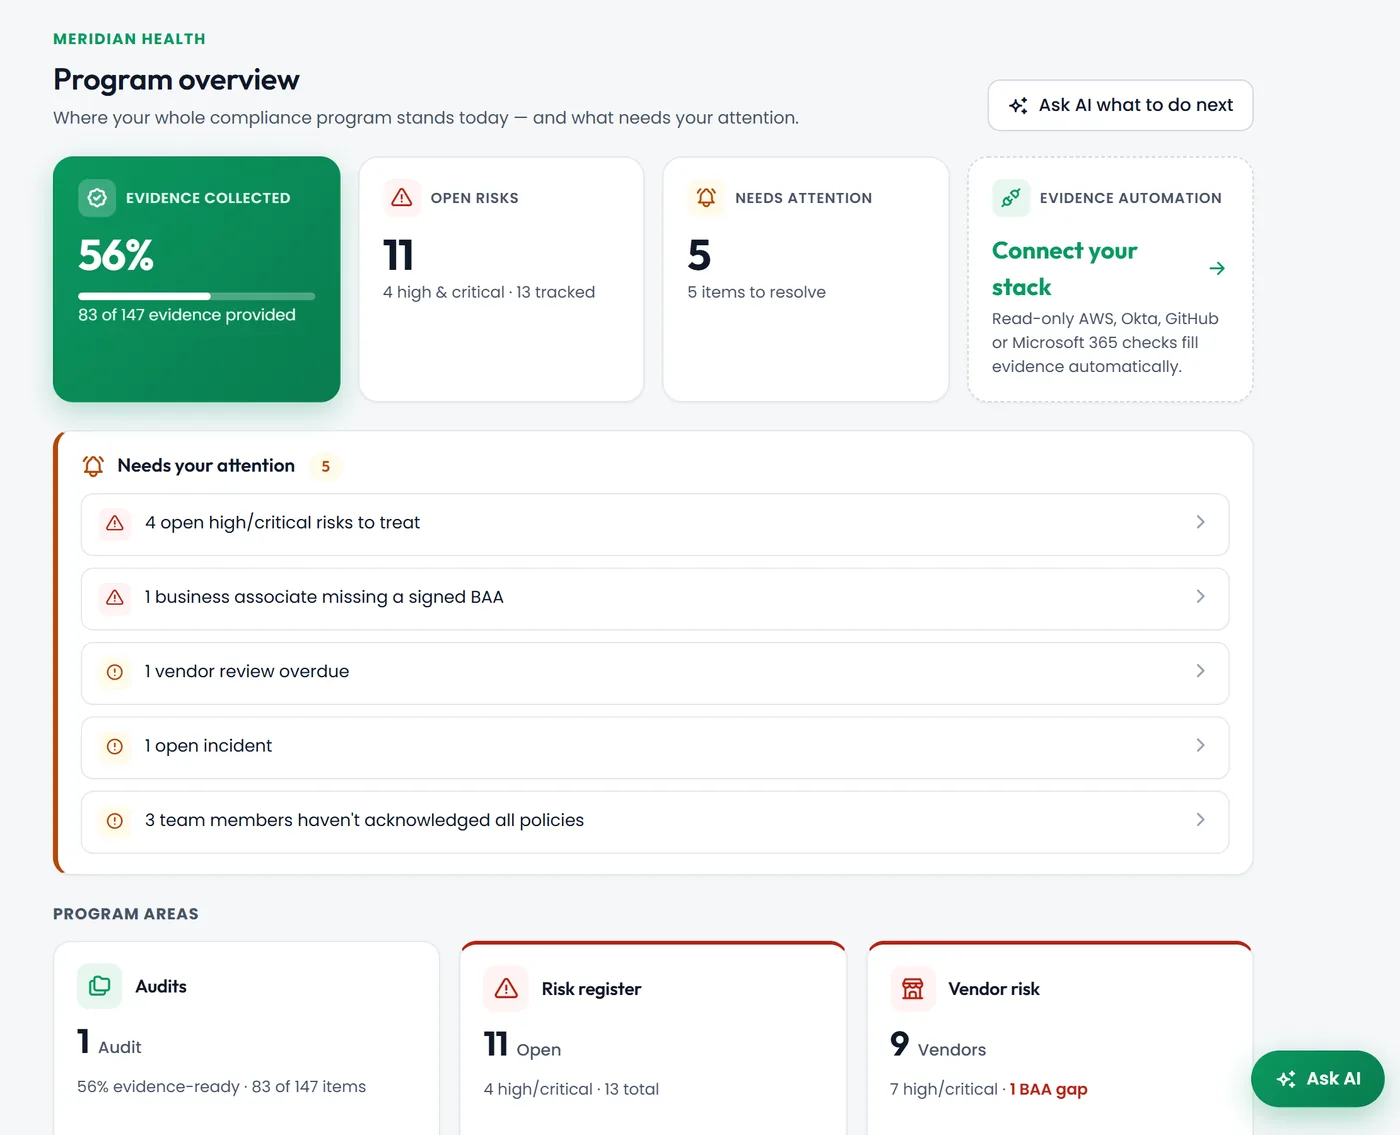
Program overview with evidence progress, open risks and a needs-attention list

Overview

Your whole compliance program on one page.

Evidence progress, open risks and everything that needs attention, pulled together from every part of the program.
  • Headline numbers: evidence collected, open risks, items to resolve
  • A "Needs your attention" list from every module: missing BAAs, open incidents, overdue reviews
  • One click into any program area
app.soc2audit.ai
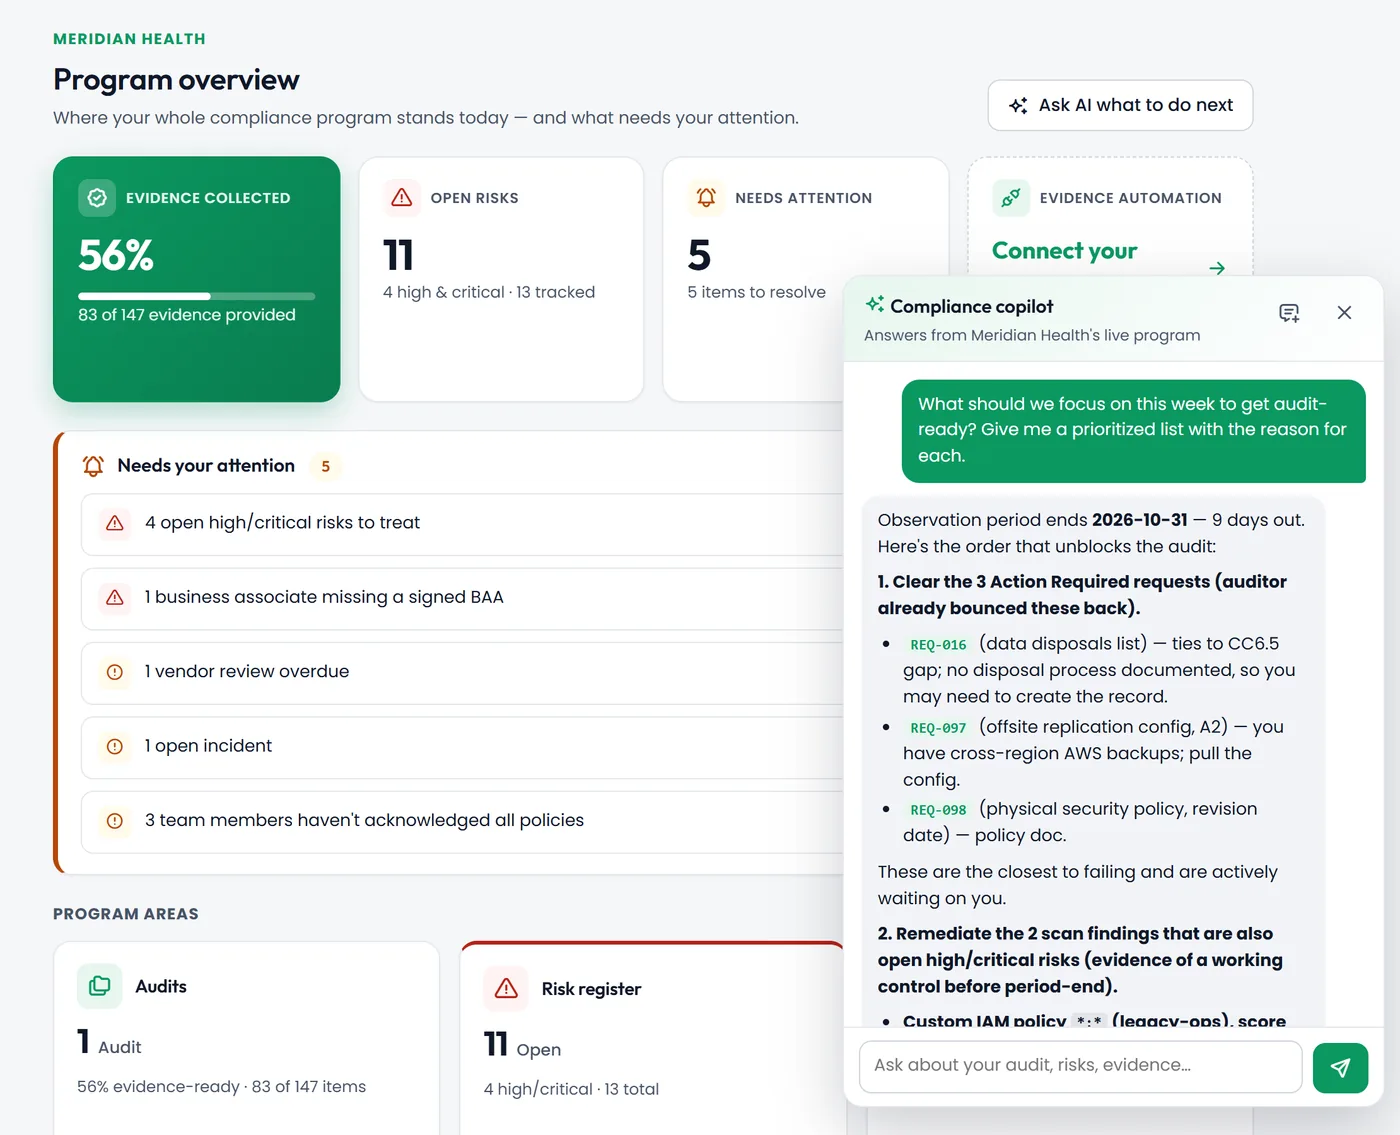
AI compliance copilot streaming a prioritized plan from live program data

Overview › Ask AI · AI-assisted

Ask anything about your program.

The compliance copilot answers from your live data: what is blocking the audit, what your auditor sent back, which risks matter most. It is on every page.
  • Prioritized plans that name the exact evidence requests, controls and deadlines
  • Writes a status update for your CEO or board in seconds
  • Answers stream in as you watch
app.soc2audit.ai
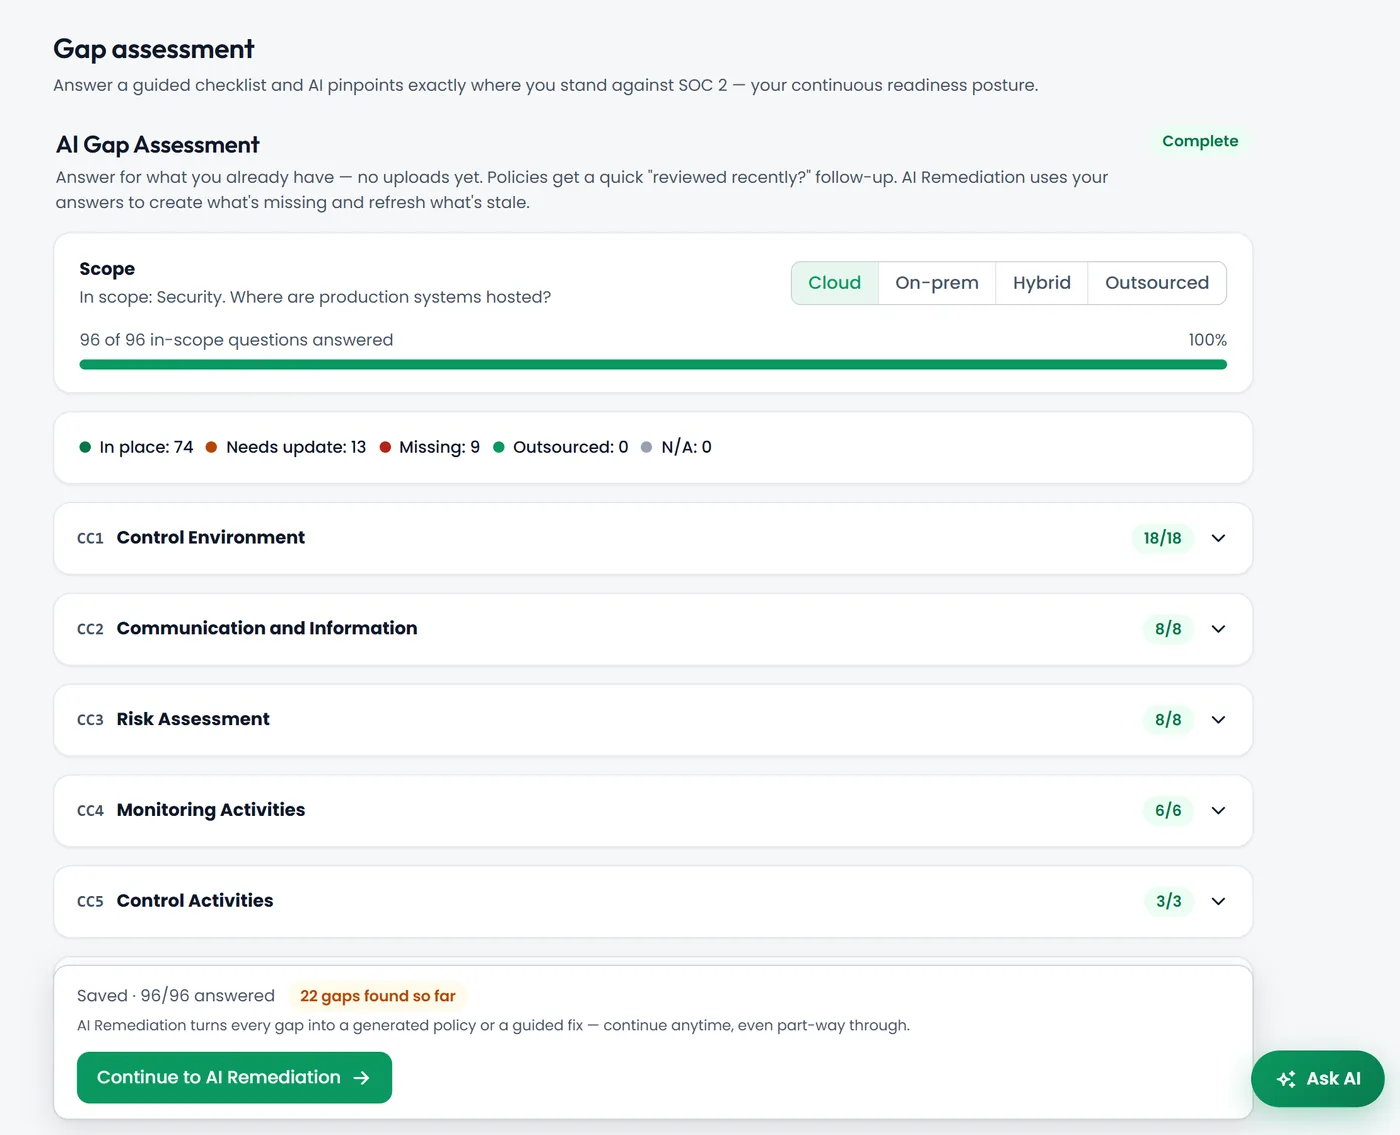
AI-guided SOC 2 gap assessment with gaps ranked by severity

Readiness › Gap assessment · AI-assisted

Know exactly where you stand.

About 100 plain-English questions mapped to the AICPA Trust Services Criteria. AI drafts answers from your company profile.
  • Covers all five Trust Services Categories
  • AI gap report, board-ready as PDF or Word
  • Every gap ranked by severity
app.soc2audit.ai
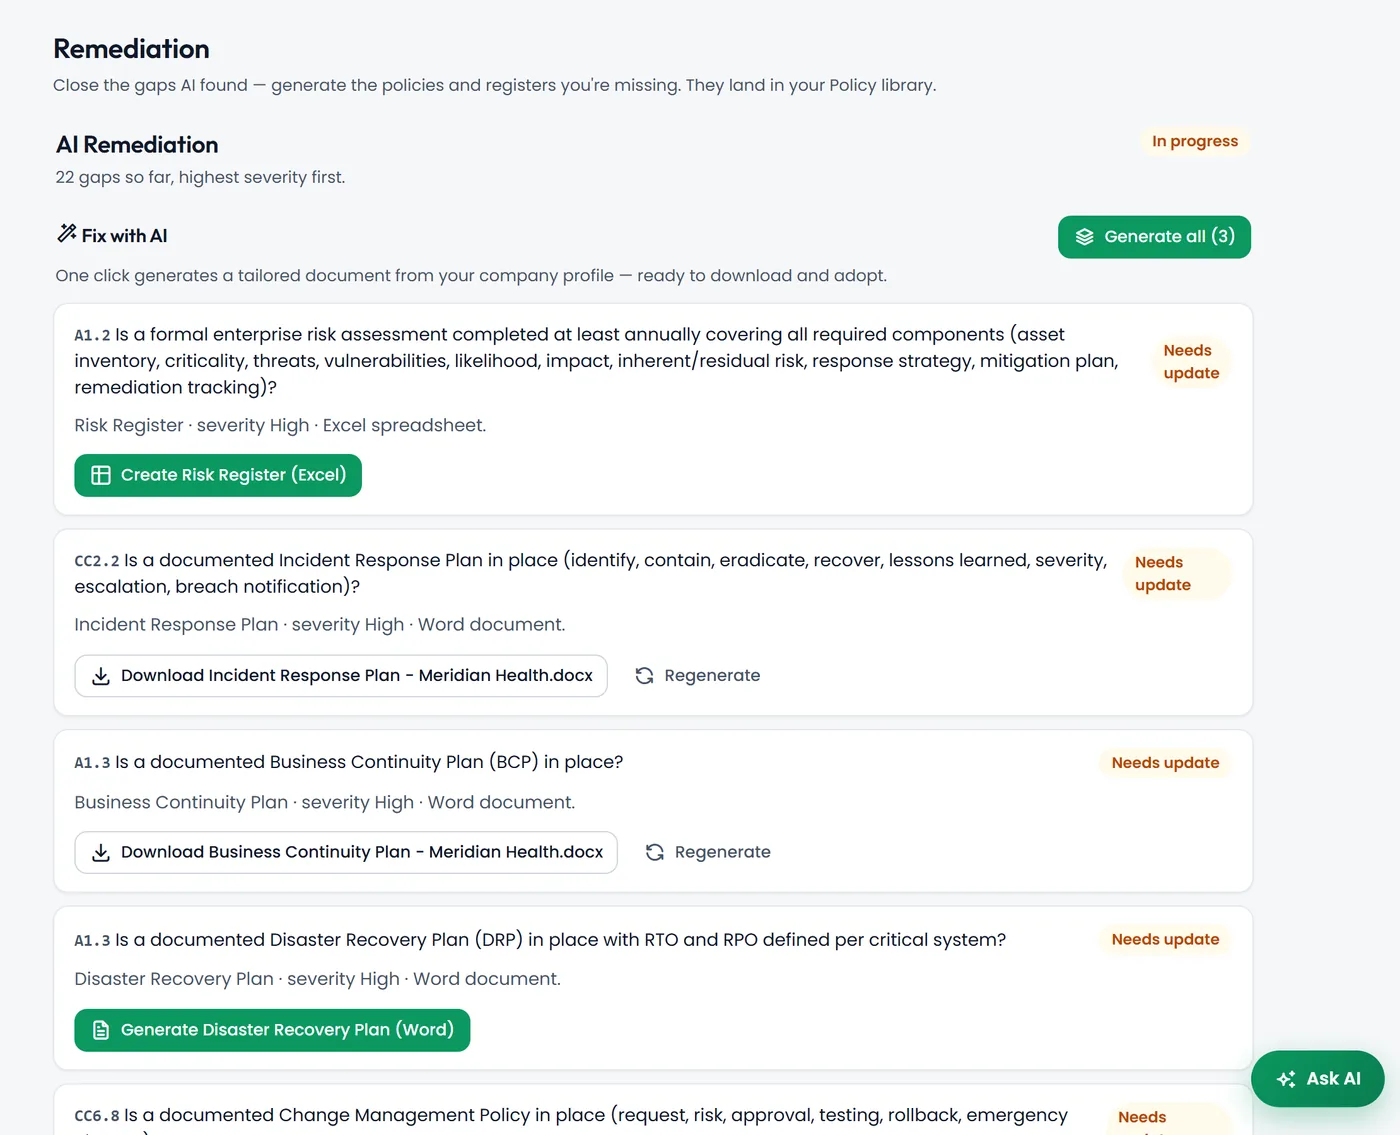
Remediation workspace where AI drafts policies and plans for each gap

Readiness › Remediation · AI-assisted

AI writes what is missing.

Turn each gap into a policy, plan or register written for your company and your stack, not a generic template.
  • Incident response, business continuity, disaster recovery and more
  • Internal Controls Matrix and Risk Register in Excel
  • "Generate all" closes every gap in one pass
app.soc2audit.ai
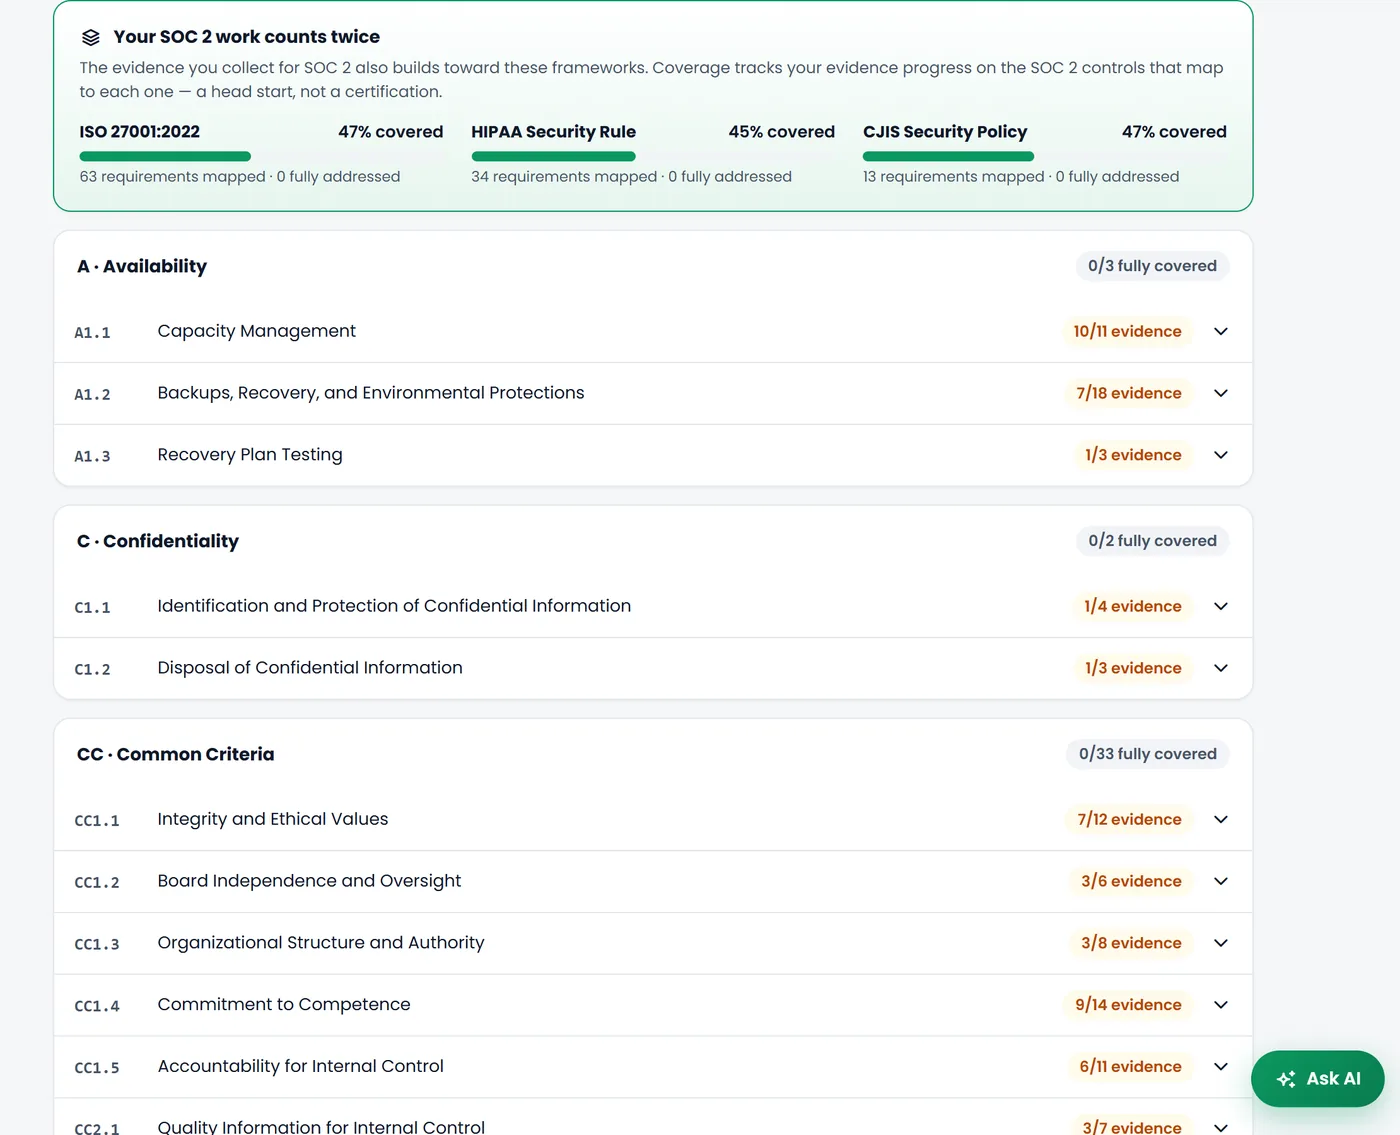
Controls map showing SOC 2 evidence coverage toward ISO 27001, HIPAA and CJIS

Readiness › Controls map

See every control, and what else it counts toward.

Every in-scope criterion with its evidence and policies, plus live coverage toward other frameworks from the same work.
  • ISO 27001, HIPAA Security Rule and CJIS coverage, measured as you go
  • Evidence status per control
  • Related policies one click away
app.soc2audit.ai
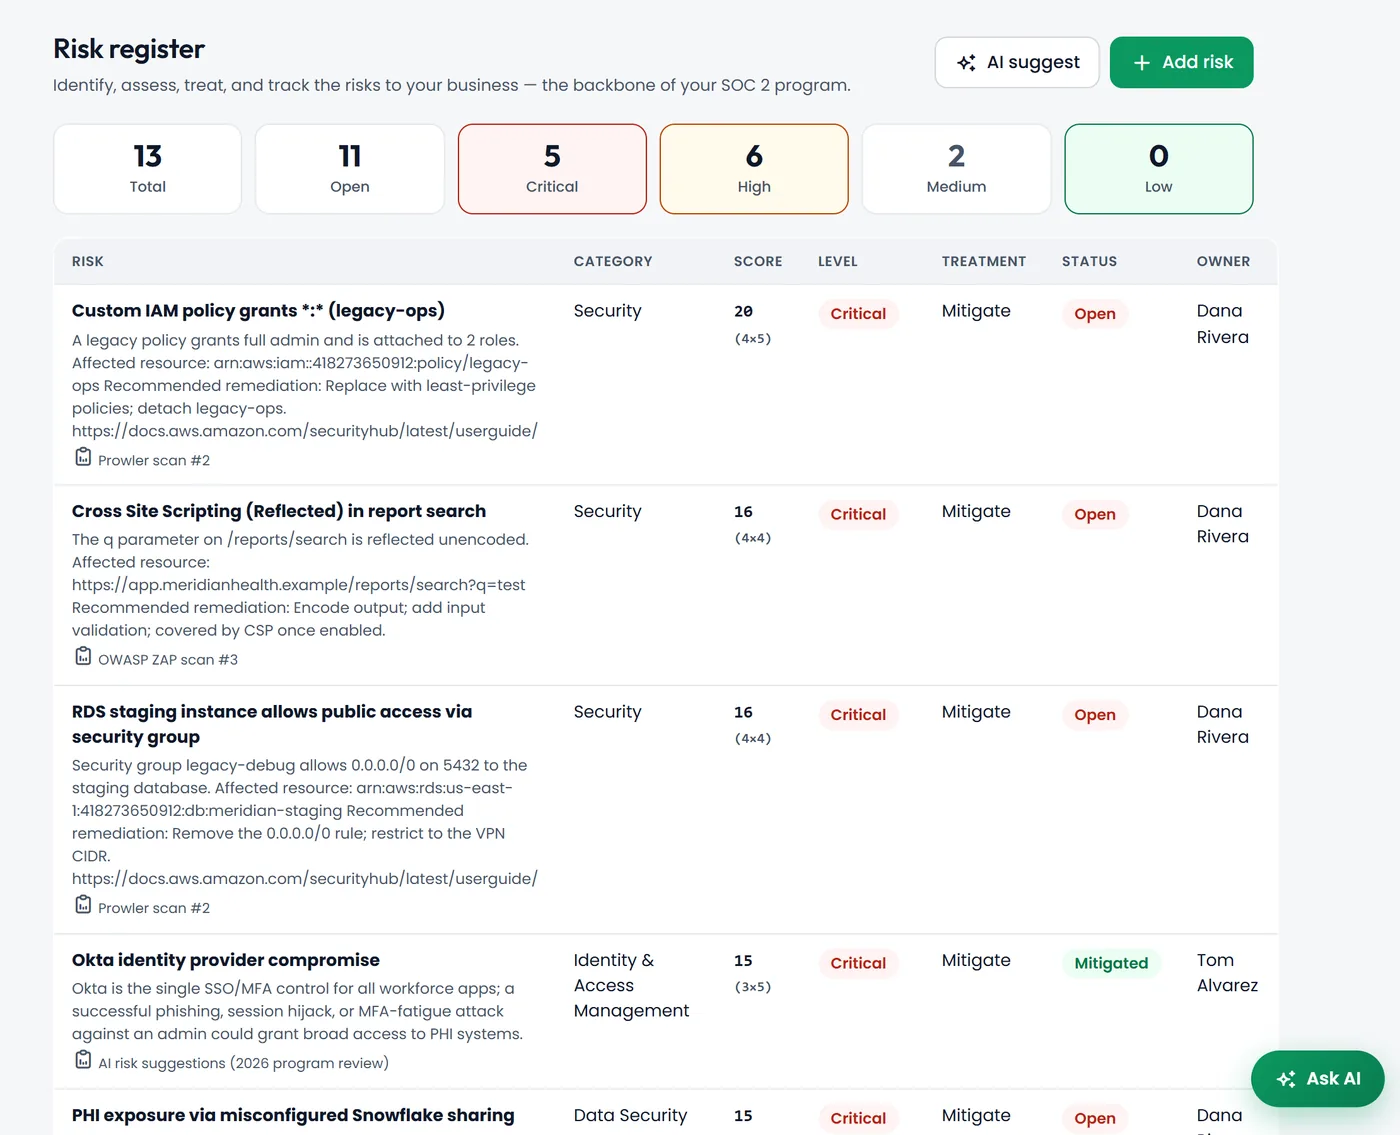
Risk register with scored risks, owners and treatment plans

Governance › Risk register · AI-assisted

Know your biggest risks and who owns them.

Score, treat and track every risk. AI suggests risks specific to your business, and scan findings feed straight in.
  • Likelihood and impact scoring with owners and treatment plans
  • AI risk suggestions from your company profile
  • Risks from assessments and scans land here automatically
app.soc2audit.ai
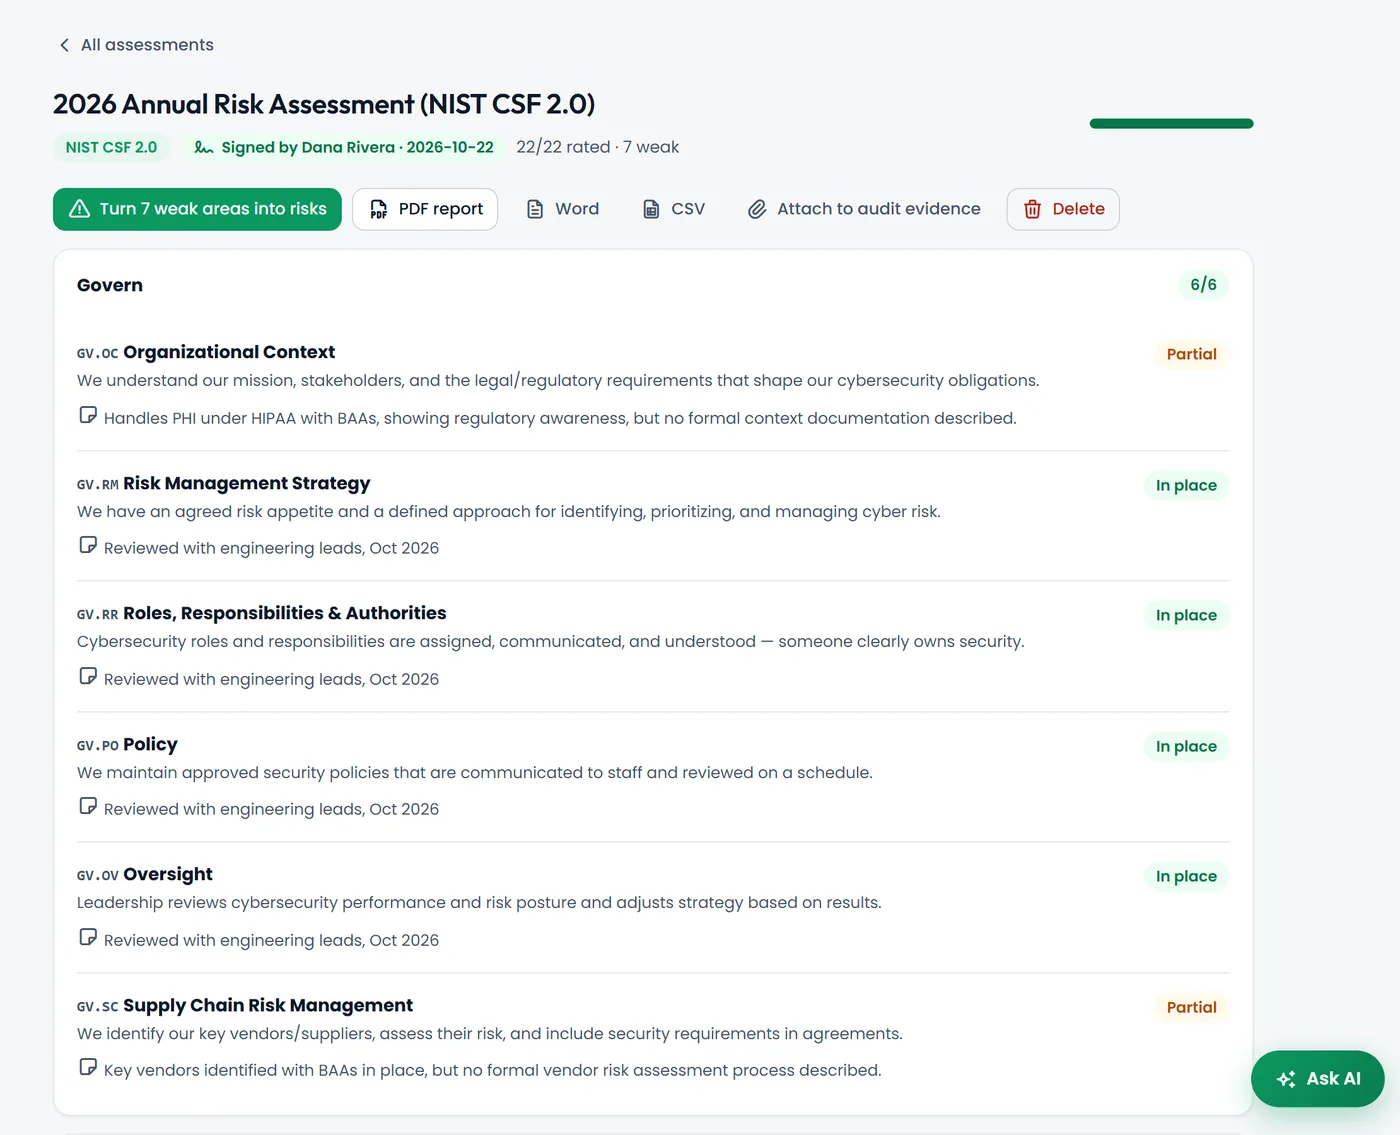
Annual risk assessment against NIST CSF 2.0 with AI-drafted ratings

Governance › Risk assessments · AI-assisted

Your annual risk assessment, done properly.

Assess against NIST CSF 2.0, CIS Controls v8.1 or the CJIS Security Policy. AI drafts the ratings and turns weak areas into risks.
  • Three frameworks built in
  • Sign-off with your name and date
  • Branded PDF ready for the auditor
app.soc2audit.ai
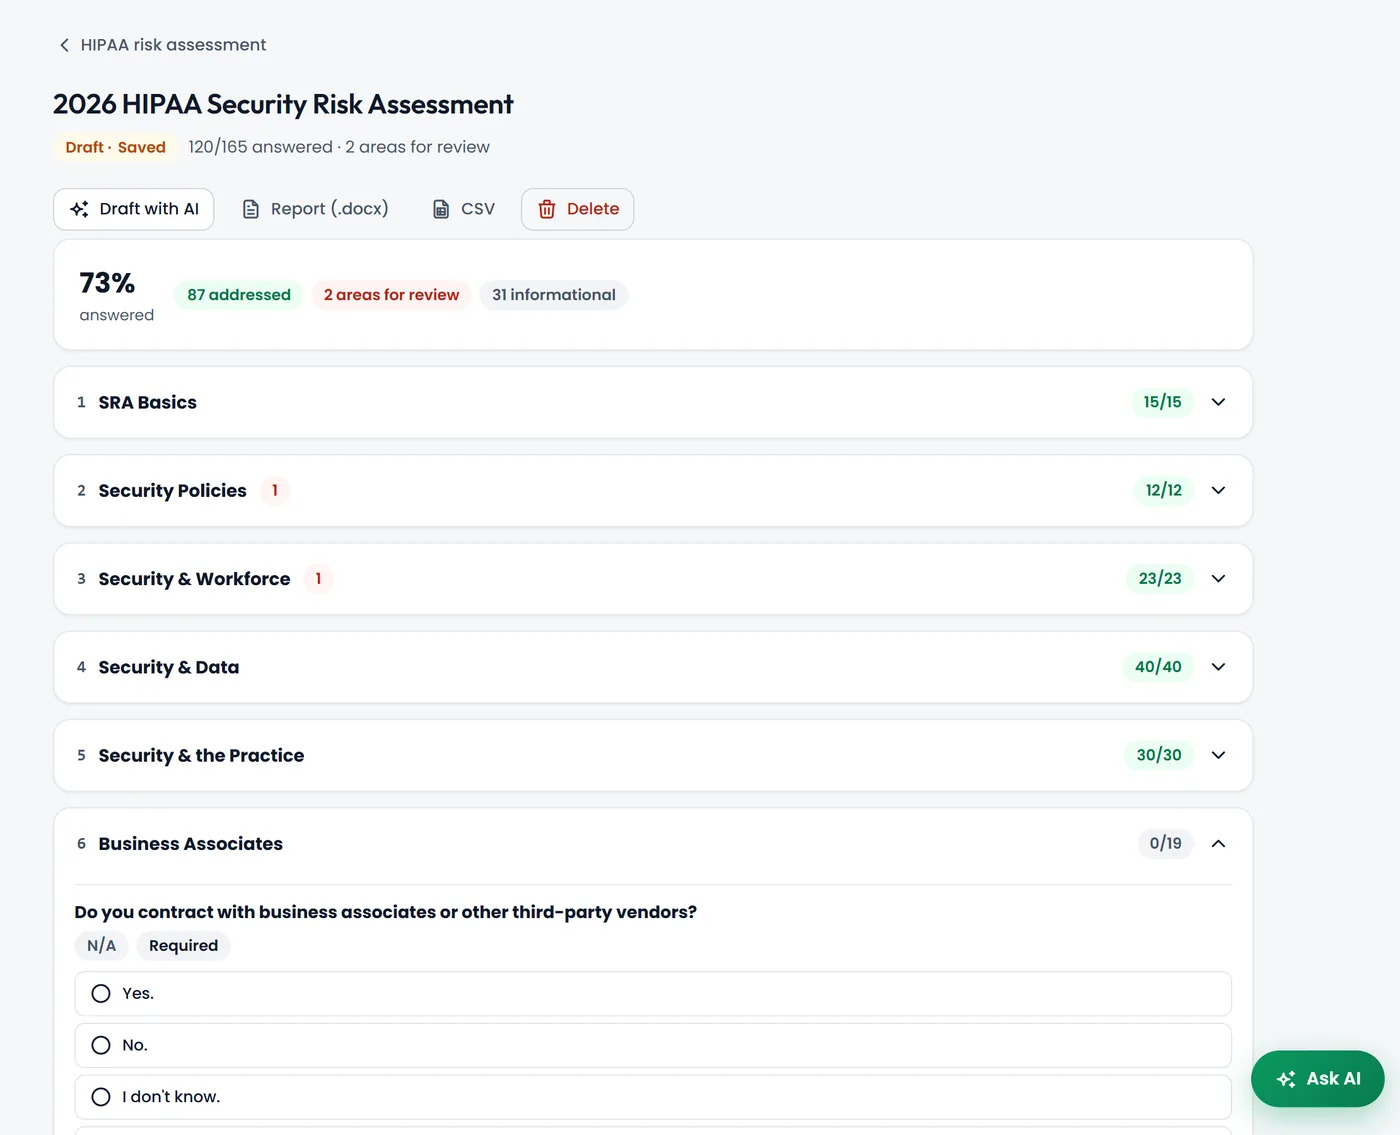
HIPAA Security Risk Assessment with AI-drafted answers and citations

Governance › HIPAA risk assessment · AI-assisted

The HIPAA Security Risk Assessment, guided.

Built on the ONC/HHS SRA Tool method: seven sections and 165 questions mapped to the HIPAA Security Rule. AI drafts answers and shows its reasoning.
  • Every answer tied to a HIPAA citation
  • AI drafts with the reason shown, you confirm
  • Sign-off and report for your records
app.soc2audit.ai
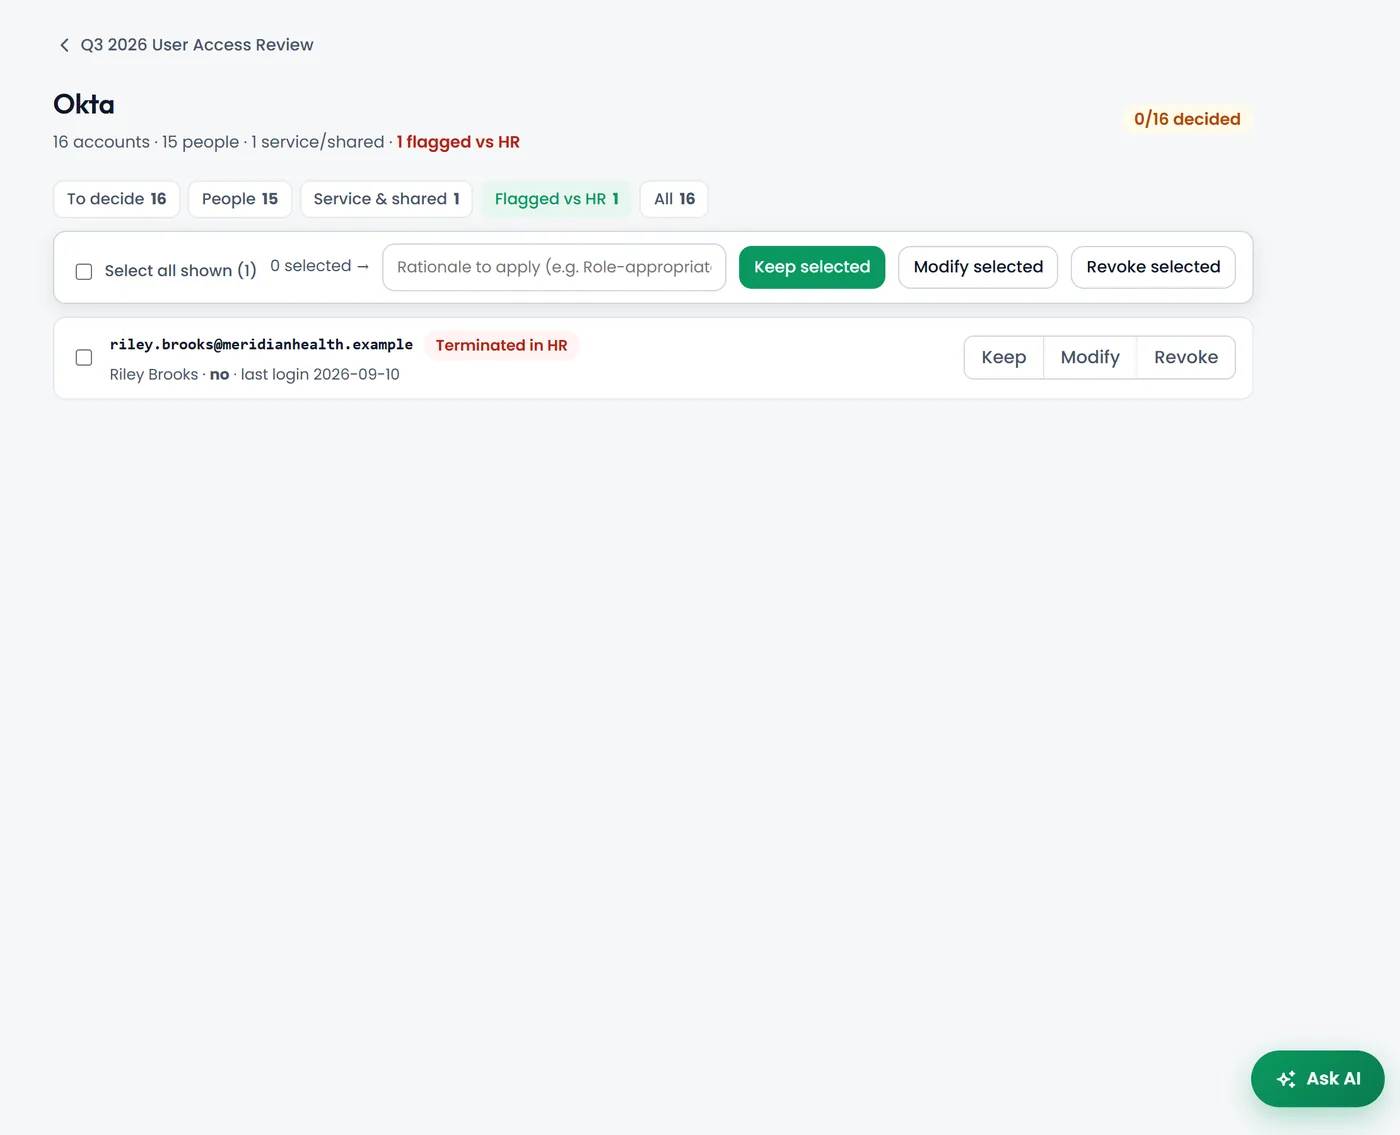
User access review flagging a terminated employee who still has Okta access

Governance › User access review

Catch the accounts that should not exist.

Compare your HR roster with each system's user list. Former employees and unknown accounts are flagged for you.
  • Flags terminated staff who still have access
  • Keep, modify or revoke, then sign off
  • Pulls user lists straight from connected systems
app.soc2audit.ai
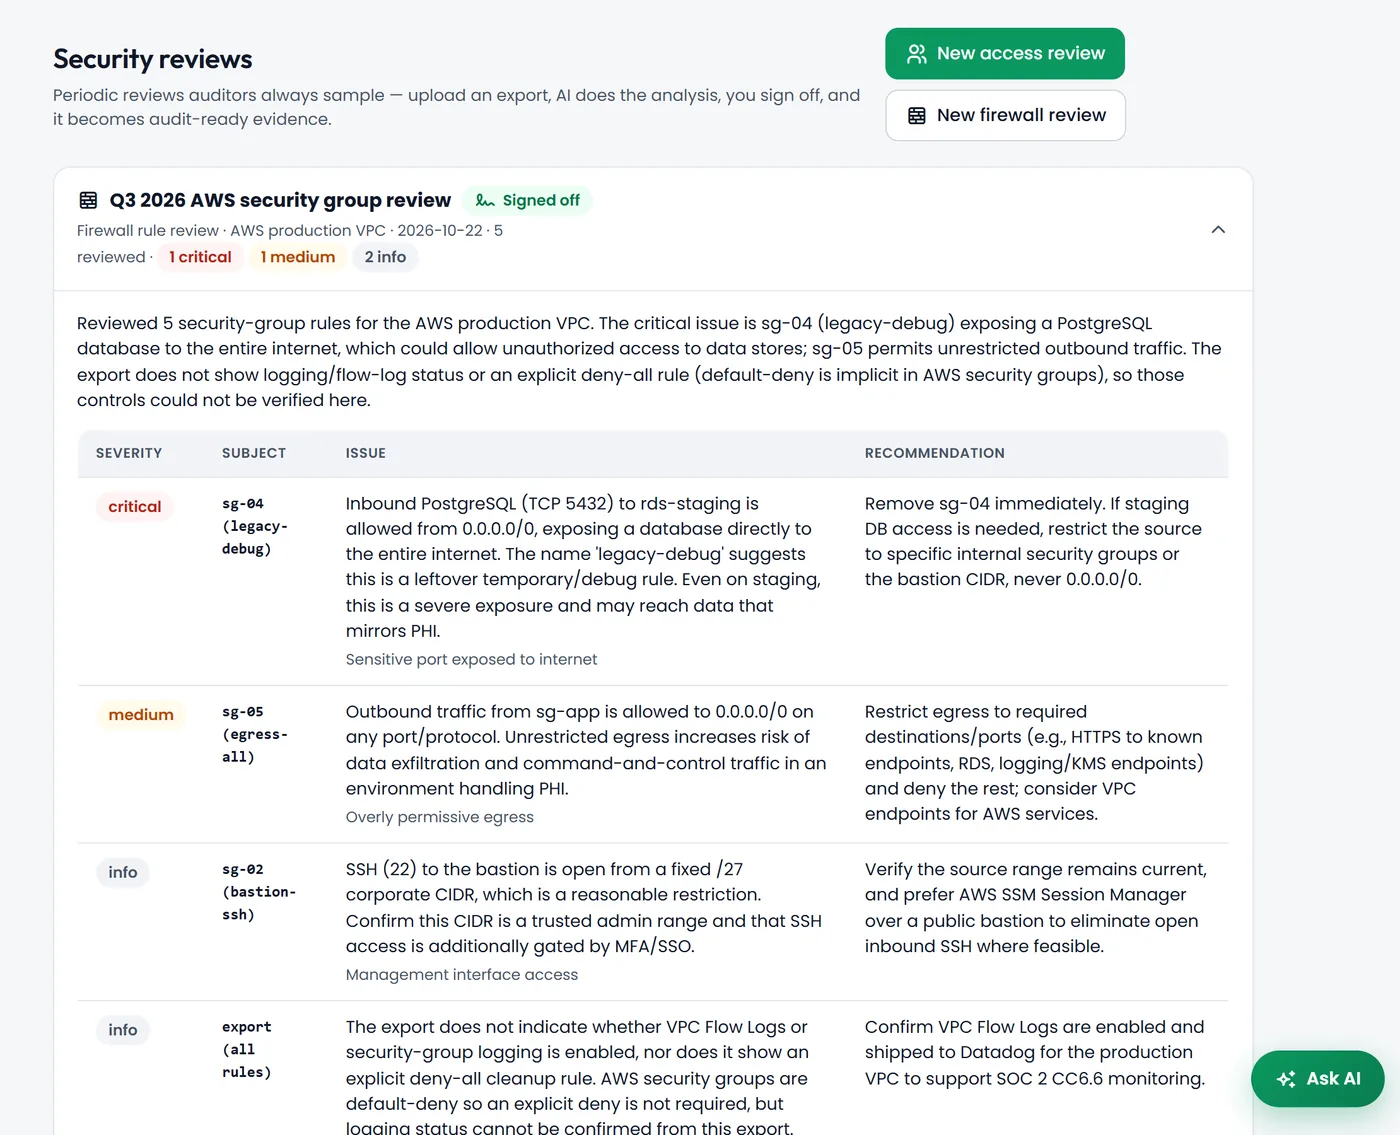
Firewall rule review with AI findings ranked by severity

Governance › Security reviews · AI-assisted

The reviews auditors always ask for.

Upload a firewall export and AI finds the risky rules. Sign it off and it becomes audit evidence.
  • Findings ranked by severity with fixes
  • Named sign-off for the auditor
  • Attaches to the right evidence request in one click
app.soc2audit.ai
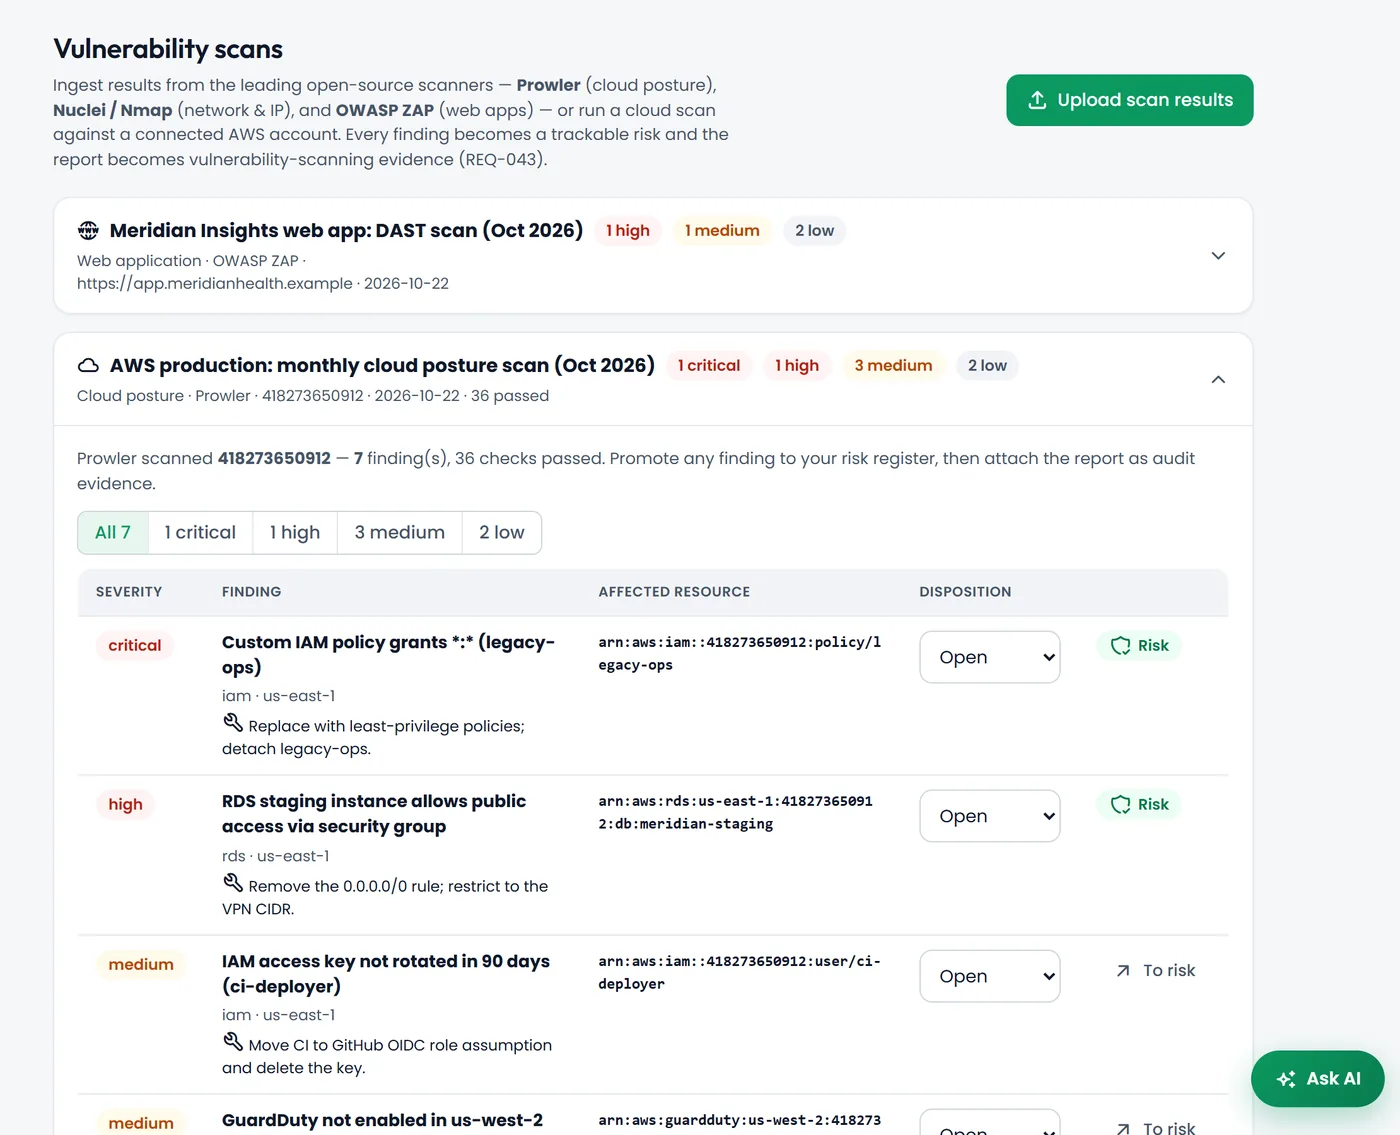
Vulnerability scan results from Prowler and OWASP ZAP with findings by severity

Governance › Vulnerability scans

Scan results that turn into evidence.

Import results from Prowler, Nuclei or OWASP ZAP. Promote findings to the risk register and attach the report to your audit.
  • Cloud, network and web app results in one place
  • Findings by severity, with a fix for each
  • The report counts as vulnerability scanning evidence
app.soc2audit.ai
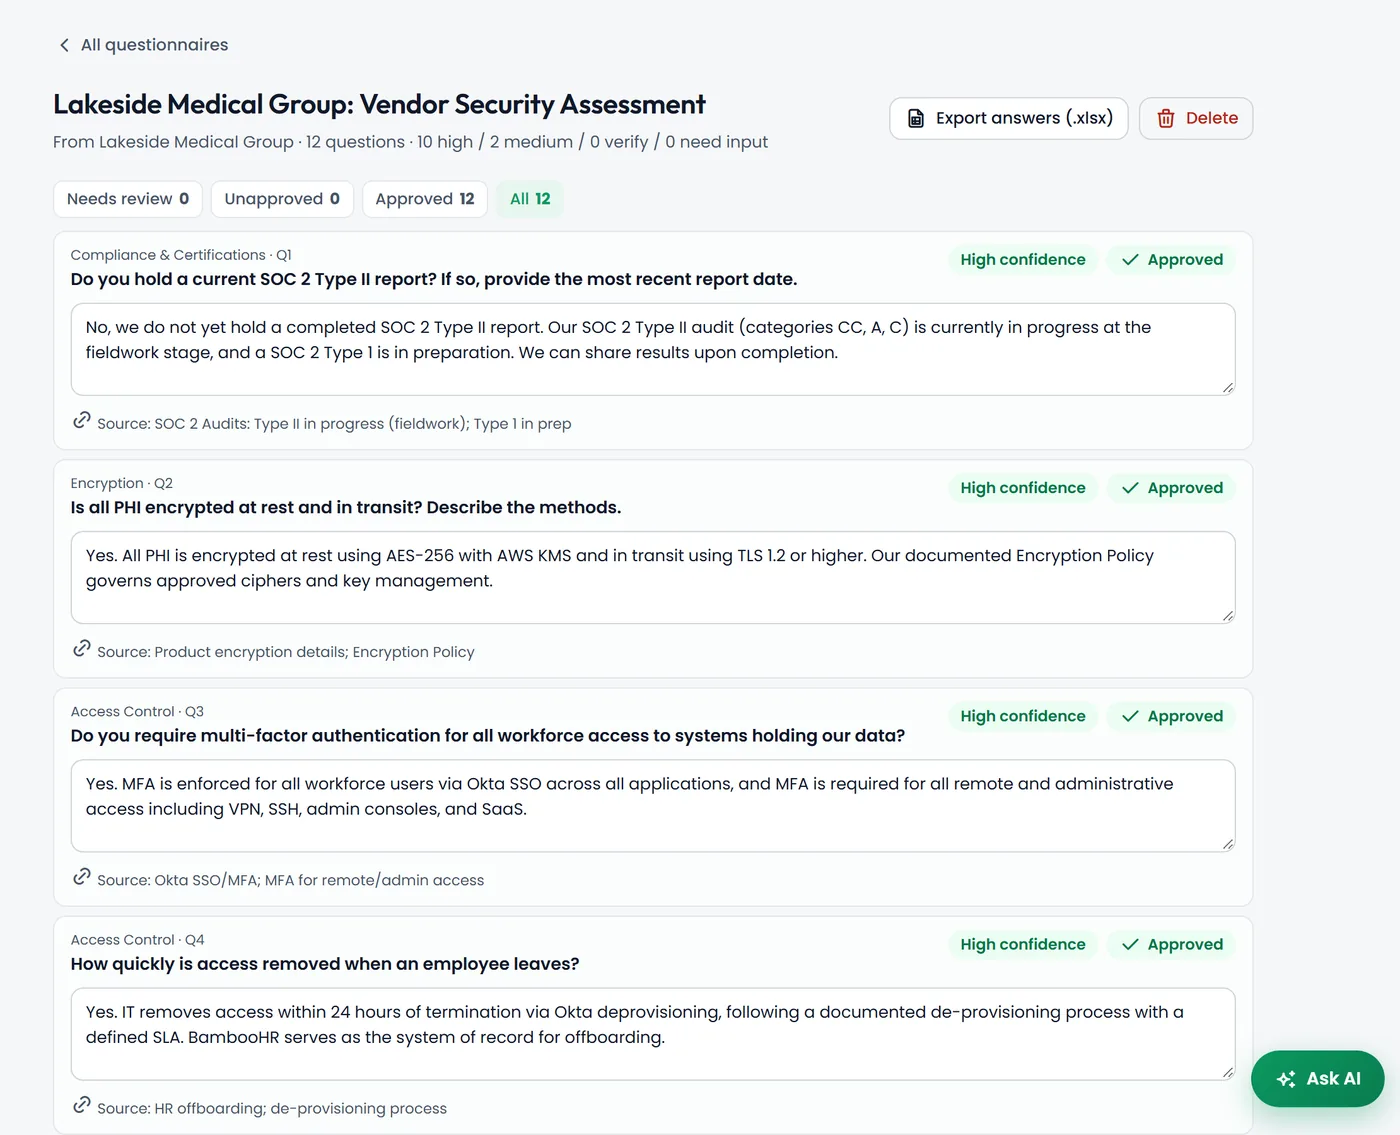
Customer security questionnaire answered by AI with confidence levels

Governance › Questionnaires · AI-assisted

Answer customer security questionnaires in minutes.

Paste or upload a questionnaire. AI answers it from your own program, with a confidence level on every answer.
  • Answers grounded in your policies and controls
  • Review and approve before anything goes out
  • Export back to Excel
app.soc2audit.ai
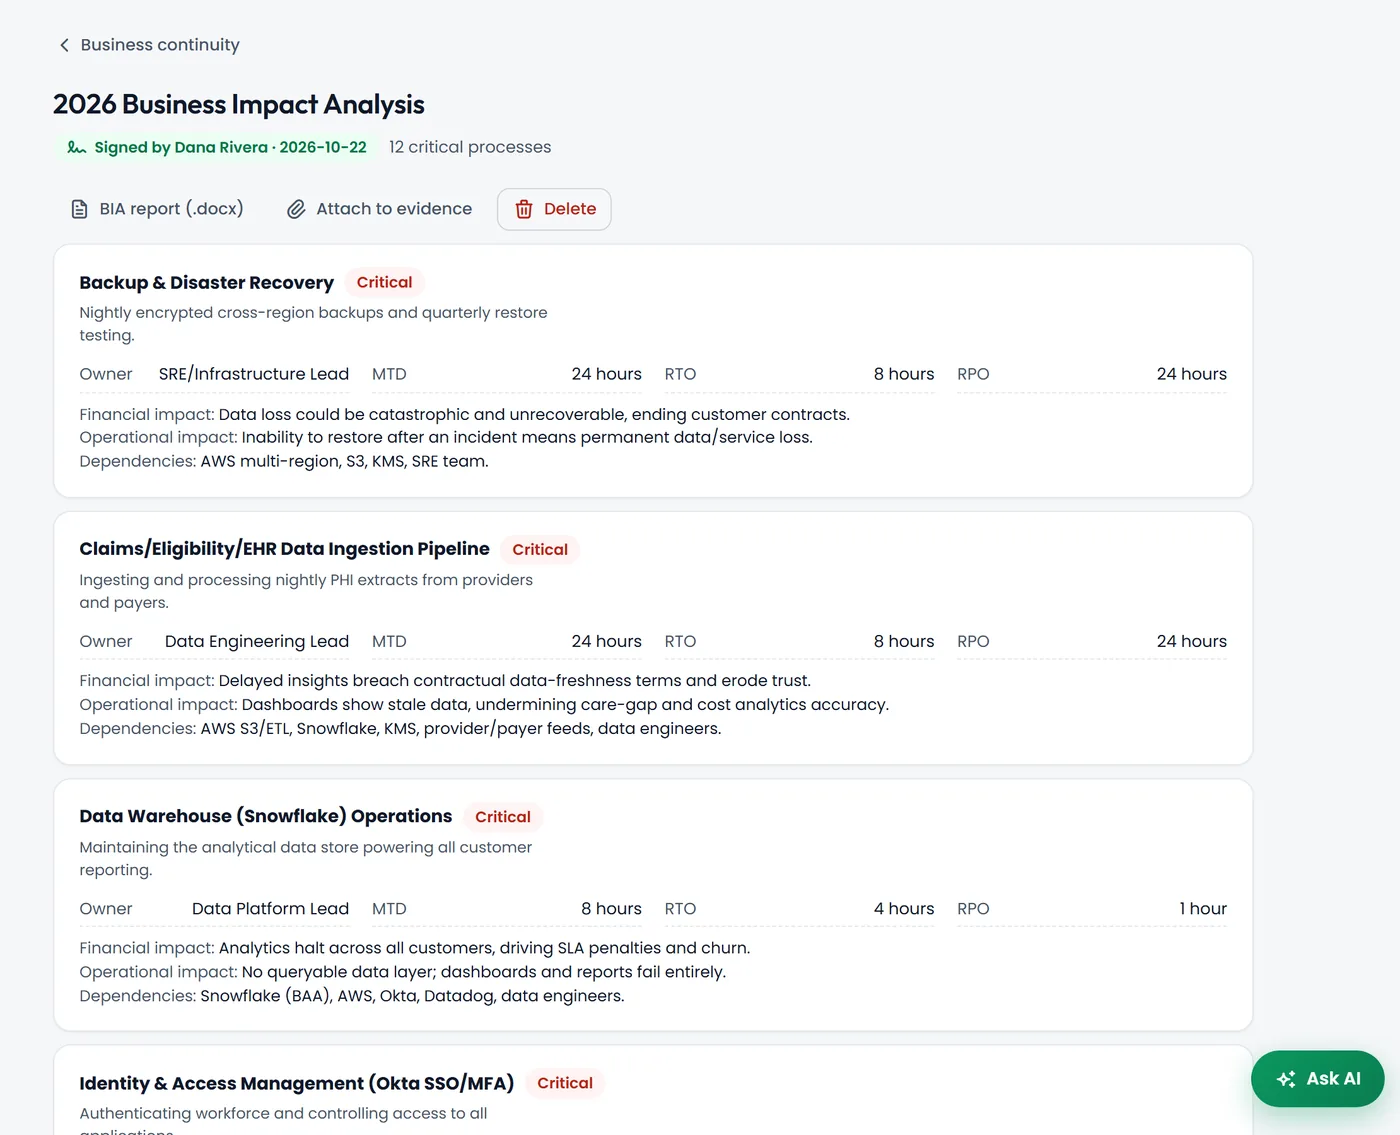
Business impact analysis with recovery targets and an AI-written continuity plan

Governance › Business continuity · AI-assisted

A continuity plan you can stand behind.

A Business Impact Analysis with AI-suggested critical processes and recovery targets, then a full continuity and disaster recovery plan built on it.
  • Recovery time and recovery point targets per process
  • AI-written BCP and DR plan grounded in your BIA
  • Signed and ready for the auditor
app.soc2audit.ai
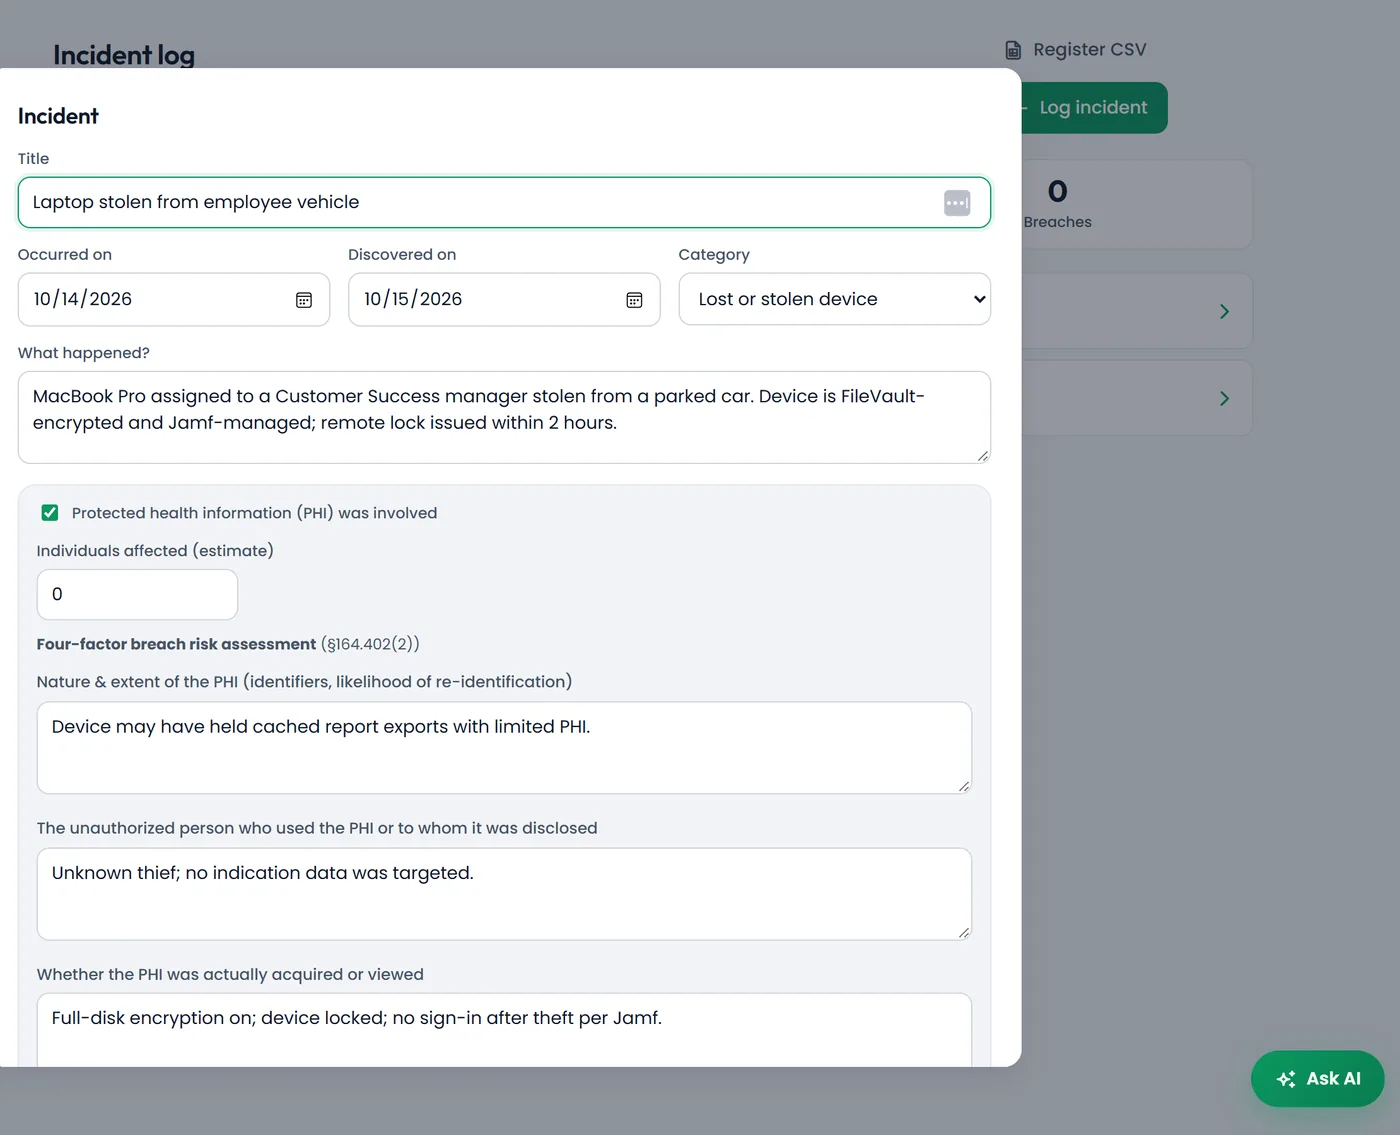
Incident log with a HIPAA four-factor breach risk assessment

Governance › Incident log

Document every incident the way regulators expect.

Log security incidents with the HIPAA four-factor breach risk assessment and notification tracking built in.
  • Four-factor breach assessment on every incident
  • Tracks notices to individuals, HHS and media
  • A complete incident history for your auditor
app.soc2audit.ai
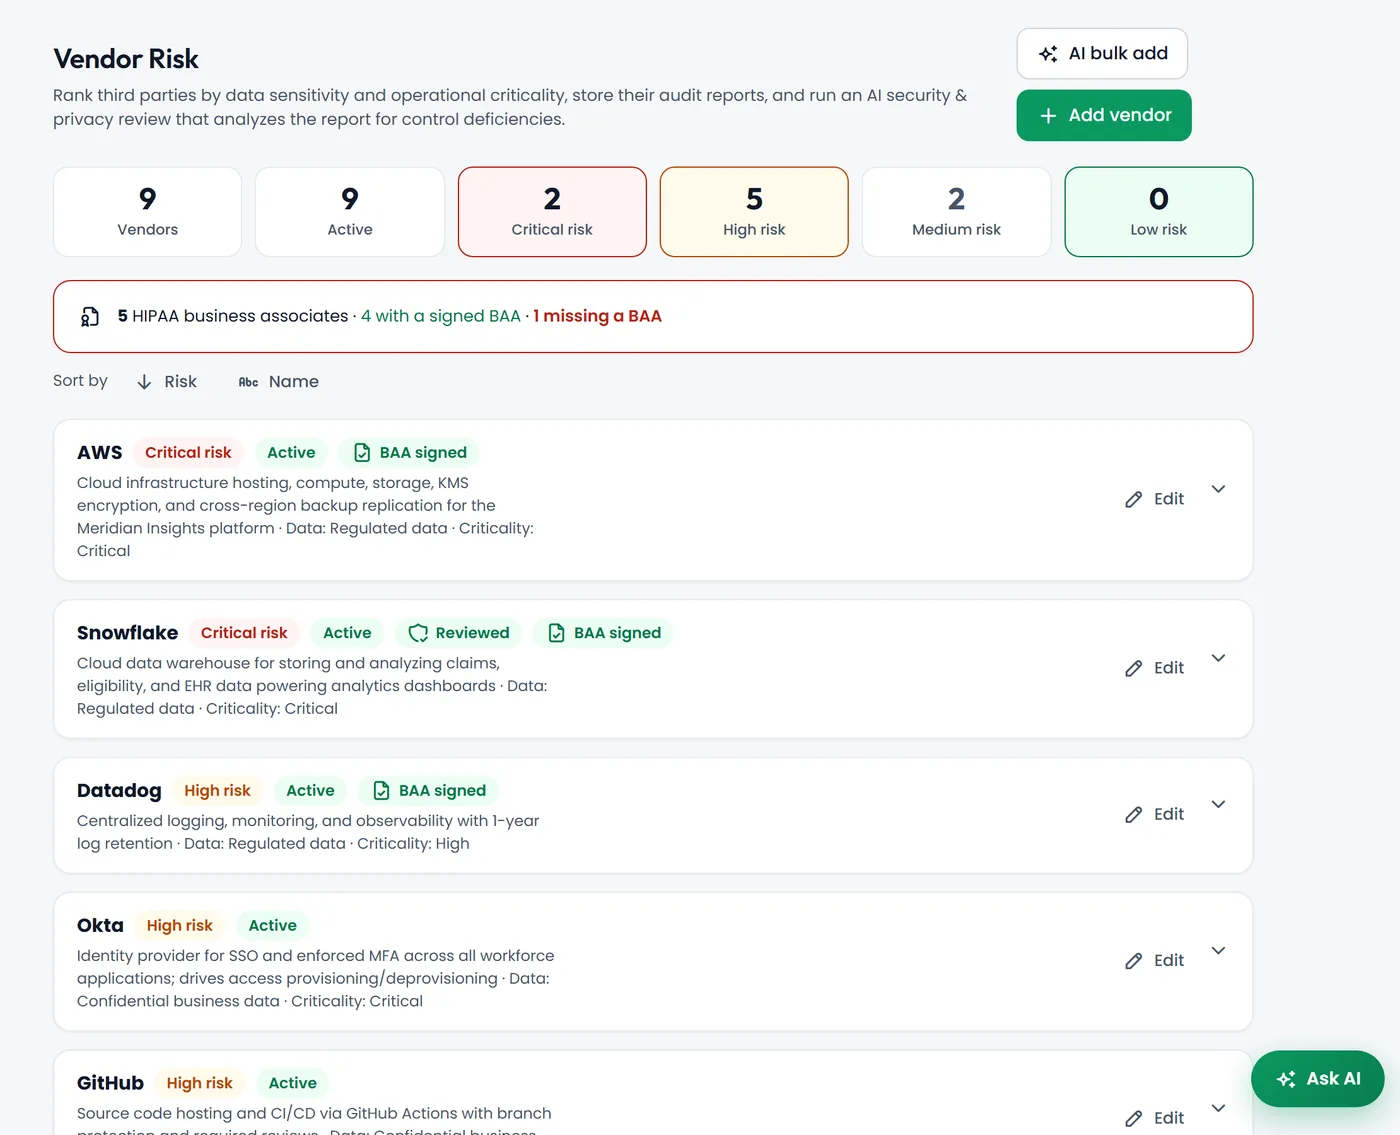
Vendor risk register with risk tiers, BAA tracking and an AI security review

Governance › Vendor Risk · AI-assisted

Know which vendors put you at risk.

Rank vendors by the data they hold and how critical they are. Track BAAs, store their audit reports and get an AI security review.
  • Risk tier from data sensitivity and business criticality
  • HIPAA BAA tracking with gap alerts
  • AI review of a vendor's SOC 2 report
app.soc2audit.ai
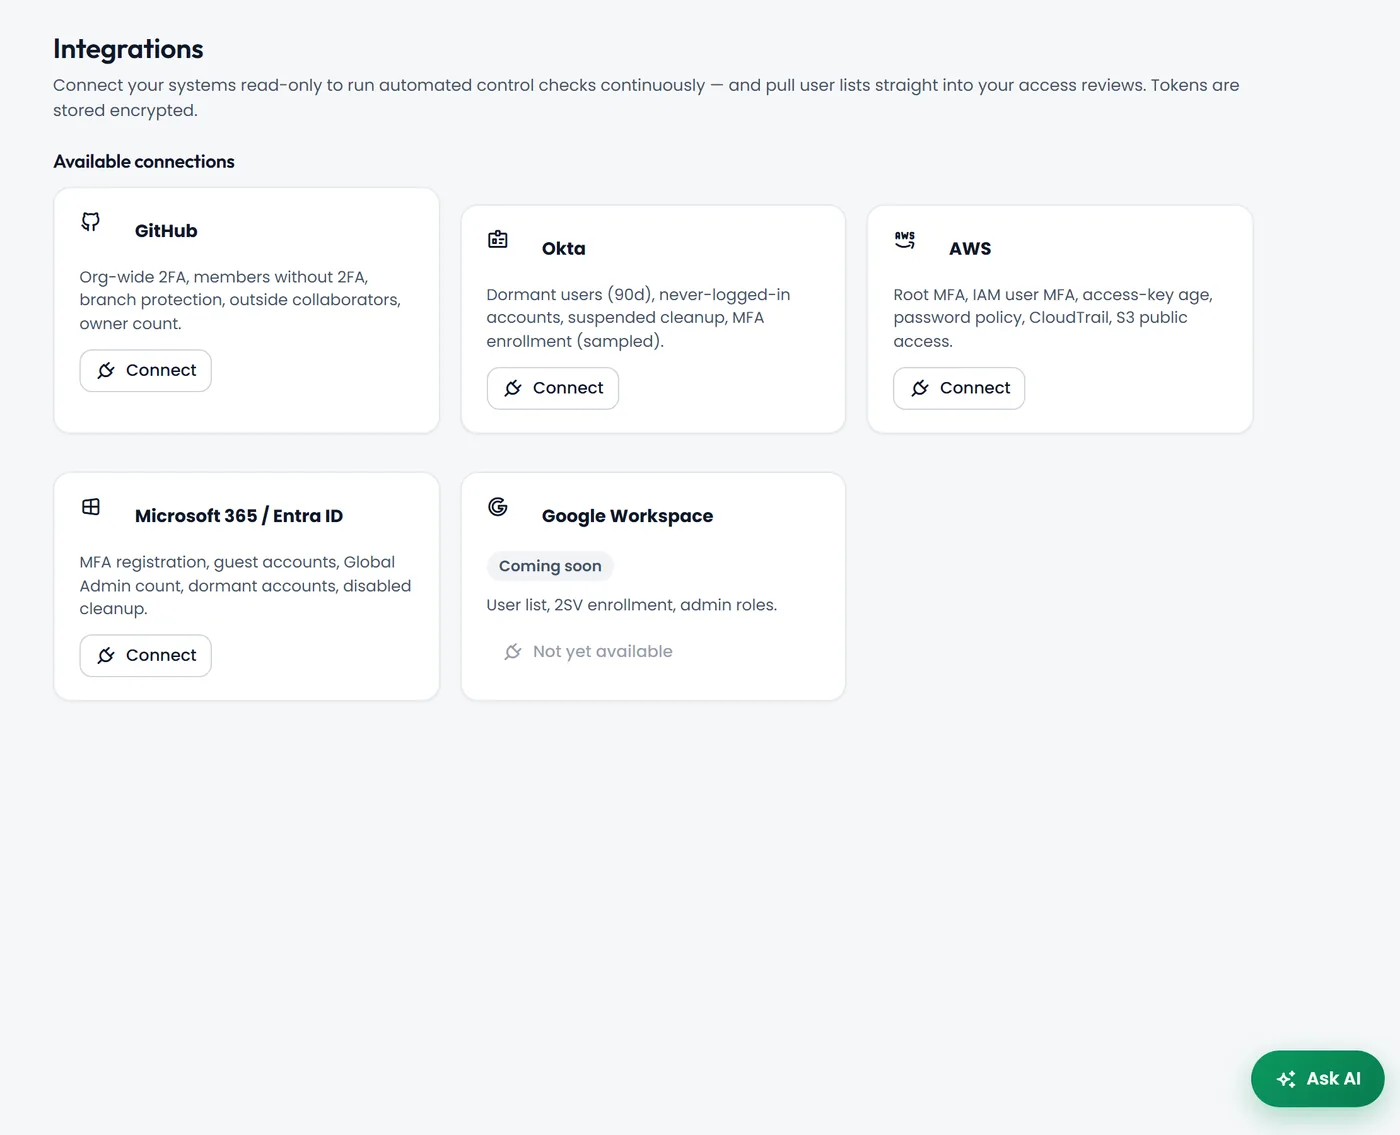
Integrations page with read-only AWS, Okta, GitHub and Microsoft 365 connections

Governance › Integrations

Evidence that collects itself.

Read-only connections to AWS, Okta, GitHub and Microsoft 365 run checks and fill matching evidence requests.
  • Checks for MFA, access keys, logging, branch protection and more
  • Evidence refreshes on every sync
  • Pulls user lists for access reviews
app.soc2audit.ai
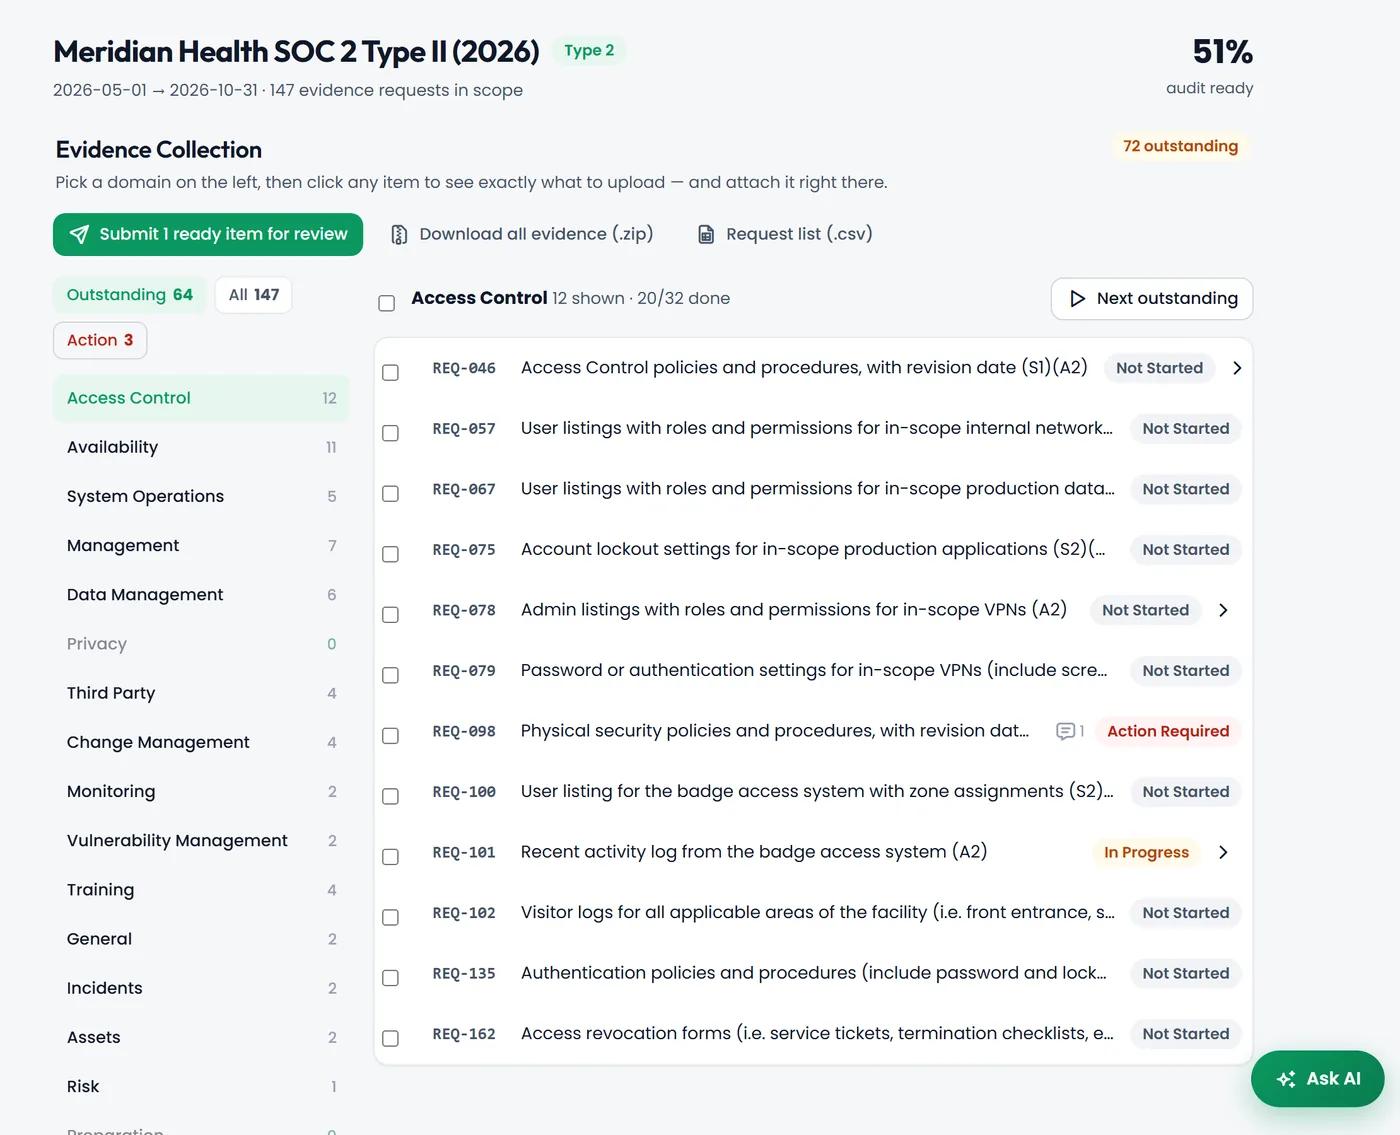
SOC 2 evidence request list organized by domain with owners and status

Audit › Evidence · AI-assisted

The whole audit request list, organized.

Every evidence request for a SOC 2 Type I or Type II, with guidance on what to upload, owners and status.
  • Organized by domain, with bulk actions
  • AI drafts the System Description, usually weeks of writing
  • Download everything as one archive
app.soc2audit.ai
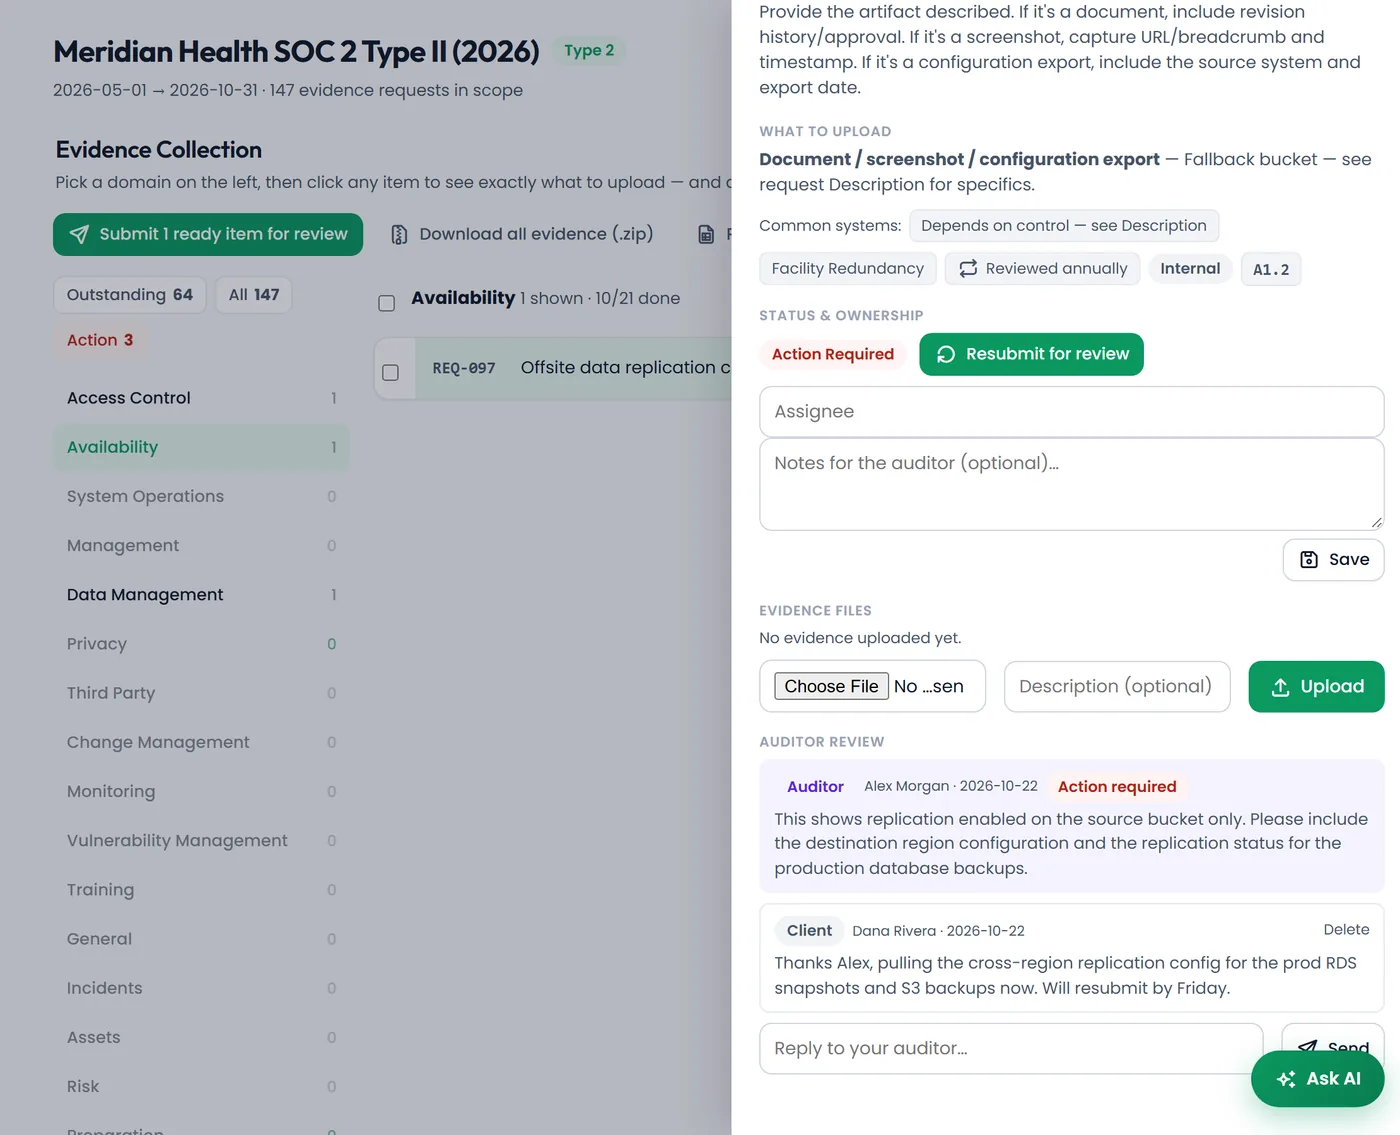
Auditor note and customer reply on an evidence request

Audit › Review thread

No more email back and forth.

When the auditor needs something changed, the note and your reply live on the evidence item itself.
  • Auditor feedback right where the evidence is
  • Items sent back are flagged until resolved
  • A full record of the conversation
app.soc2audit.ai
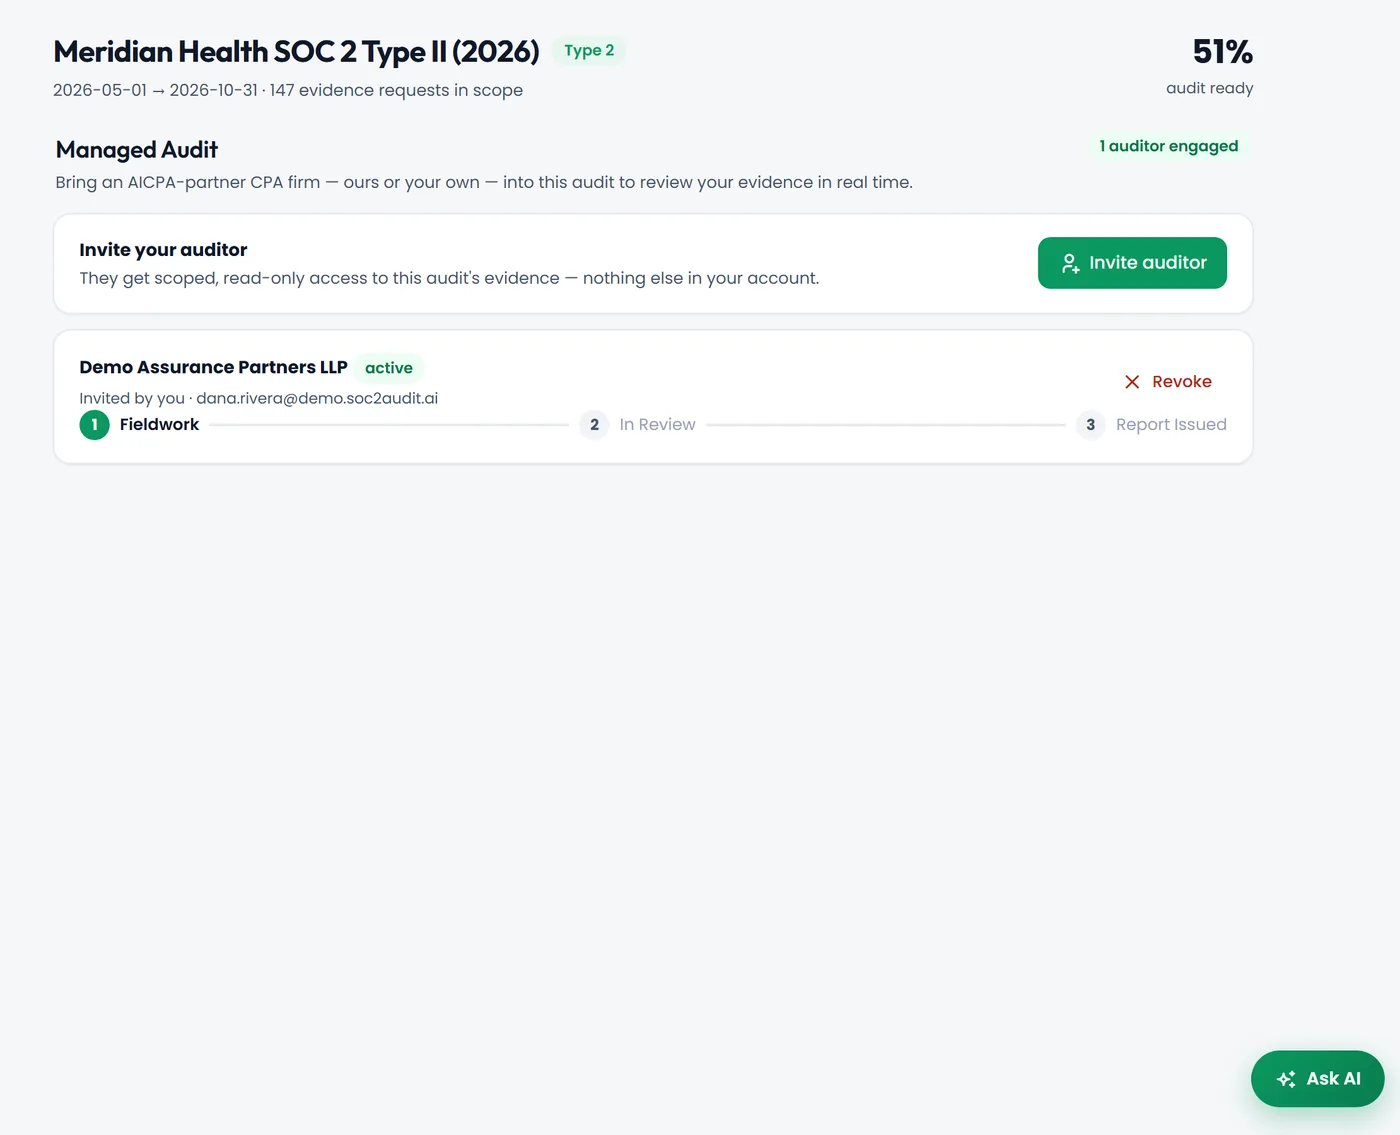
Managed audit tab tracking the CPA firm engagement stage

Audit › Managed audit

Bring your auditor into the platform.

Work with an AICPA-licensed CPA firm from our network, or your own. They get access to that audit only.
  • Invite a firm in one step
  • Track the audit from fieldwork to report issued
  • The final report is delivered in the platform
app.soc2audit.ai
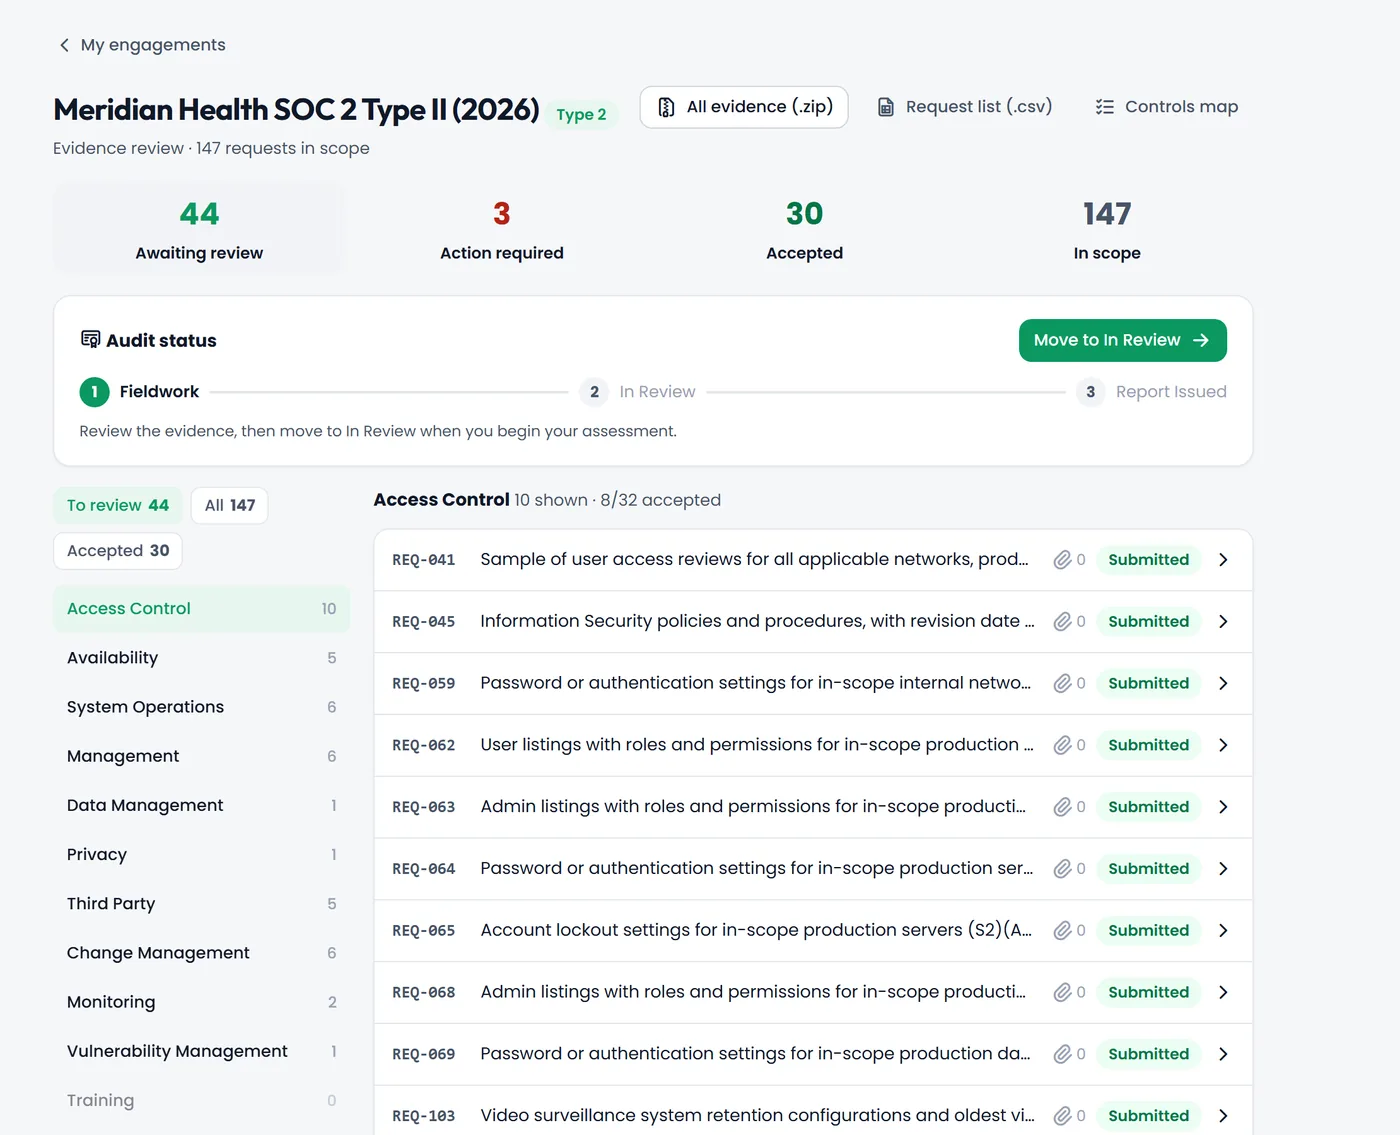
Auditor view of the evidence request list

Audit › Auditor's view

Your auditor works where your evidence lives.

The audit firm reviews the same request list, accepts evidence or sends it back, and asks for samples.
  • Accept or request changes on each item
  • Type II sample requests
  • Fewer fieldwork hours, a faster report
app.soc2audit.ai
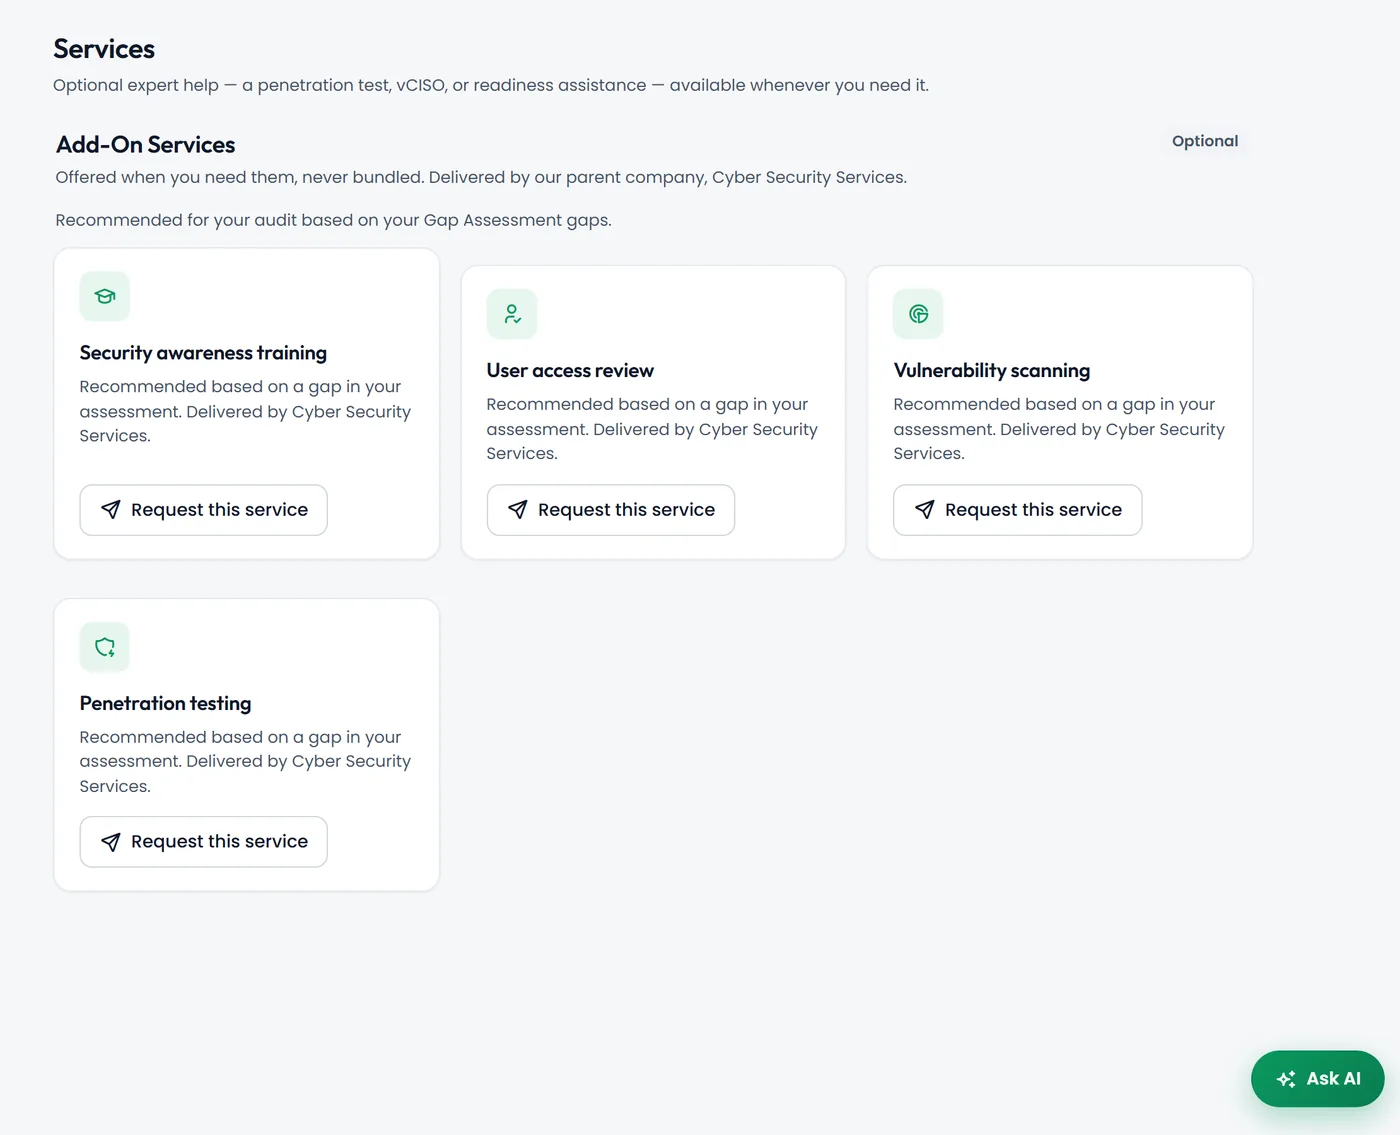
Optional security services offered from inside the platform

Audit › Services

Expert help when you need it.

Penetration testing, vulnerability management, vCISO and more from Cybersecurity Services, suggested when a gap calls for one.
  • Offered in context, never required
  • Request with one click
  • Delivered by the team behind the platform
app.soc2audit.ai
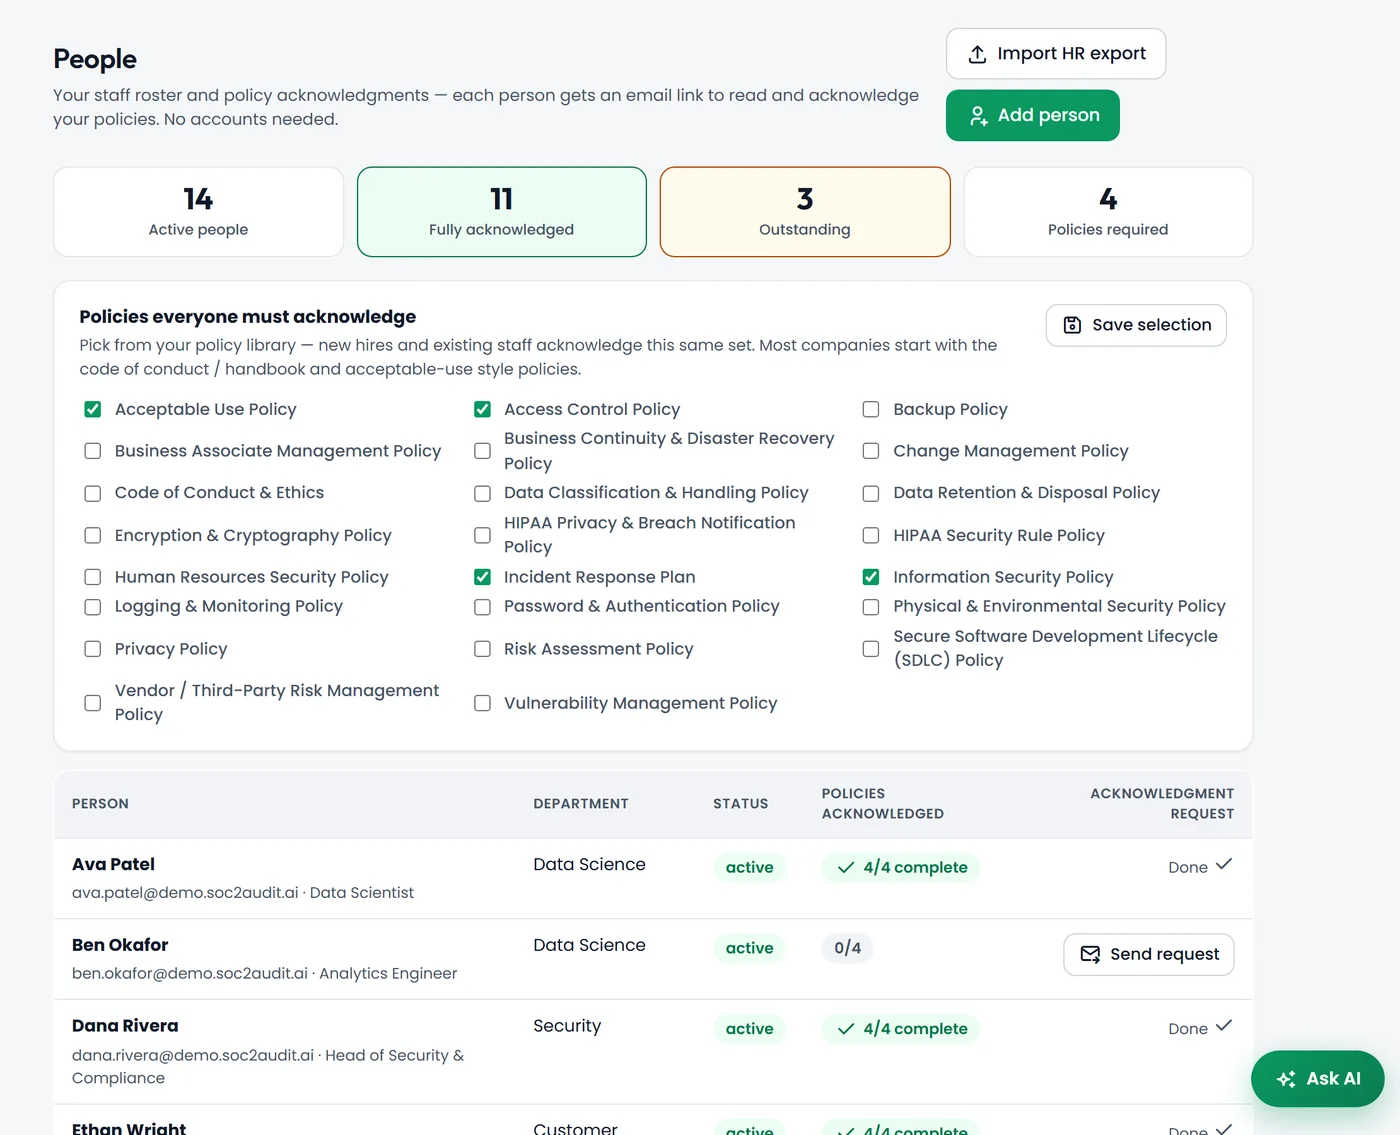
People page tracking staff policy acknowledgments

Company › People · AI-assisted

Policy acknowledgment without the chasing.

Staff acknowledge the policies you choose through a personal link. No account needed.
  • See who is done and who is outstanding
  • Import staff from an HR export with AI
  • Acknowledgment register as PDF or Excel for the auditor
app.soc2audit.ai
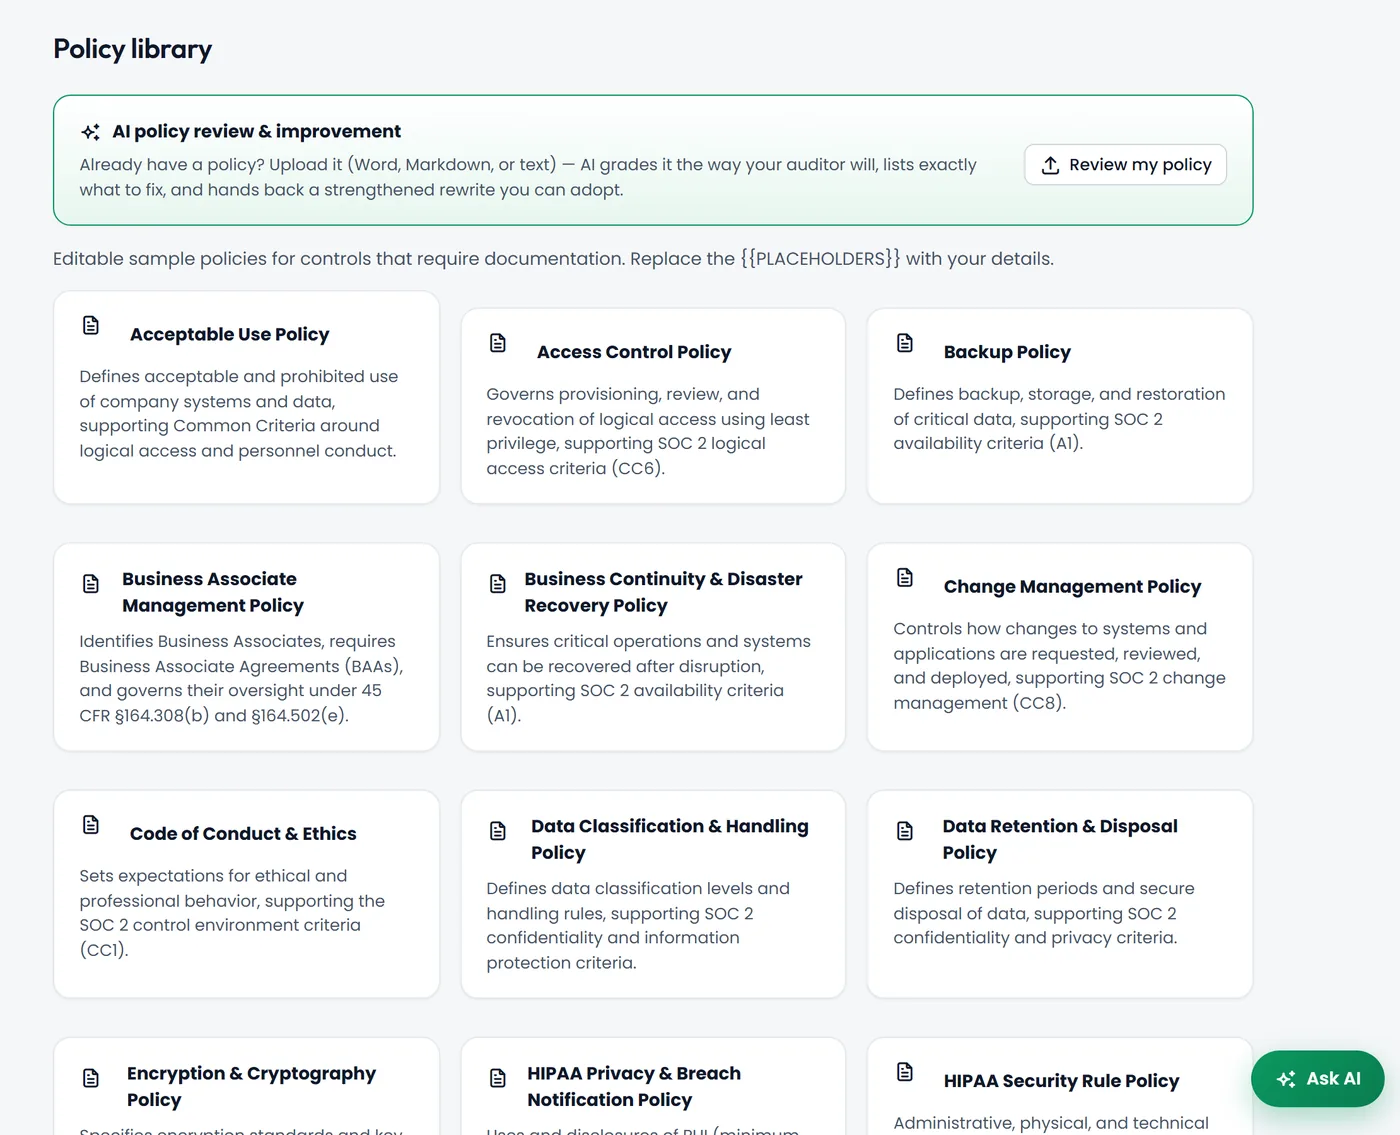
Policy library with SOC 2 and HIPAA policy templates

Company › Policy library · AI-assisted

Every policy, in one place.

Policy templates covering SOC 2 and HIPAA, alongside the policies AI wrote for you. Already have a policy? AI reviews it the way your auditor would.

  • AI policy review: what to fix, plus a strengthened rewrite to adopt
  • Download in Word to edit and adopt
  • Linked to the controls they satisfy

Real screens from a demo company, Meridian Health, a fictional health-tech SaaS near the end of a SOC 2 Type II observation period. Click a screen to enlarge it.

AI-Guided Gap Assessment

Know exactly where you stand before you spend a dollar on remediation.

AI-guided SOC 2 gap assessment with gaps ranked by severity

What the AI does

What you get

AI-Guided Remediation

Fix the gaps with an AI that tells you exactly what to do.

What The Ai Does

What you get

Audit Firms Partner

Need a pen test or a vCISO? Add them when you're ready, not before.

Some SOC 2 programs benefit from services that the platform can’t deliver on its own: a manual penetration test, ongoing vulnerability management, or a fractional CISO to review your program. Our parent company, Cybersecurity Services, LLC, offers these as optional add-ons through a separate engagement.

The AI copilot flags when a service might strengthen your program, but the decision is always yours. We do not force-bundle, and you can bring your own vendor if you prefer.

Optional security services offered from inside the platform

Services

What it includes

Penetration Testing

Manual web application, network, and cloud pen testing by OSCP-certified engineers. Produces an auditor-accepted report.
Vulnerability Management
Continuous vulnerability scanning, prioritized remediation guidance, and monthly reporting.
Virtual CISO (vCISO)
Fractional executive security leadership: policy review, board reporting, incident response planning, and vendor risk oversight.
SOC 2 Readiness Consulting
Optional hands-on help for teams who want a human expert alongside the AI copilot. Priced by scope.
AI-Guided Evidence Collection

Every piece of evidence, mapped to every control, with the AI telling you exactly what to upload.

SOC 2 evidence request list organized by domain with owners and status

What the AI does

What you get

AICPA Partner

An AICPA-licensed CPA firm runs your audit. You watch it happen in real time.

How it works

What you get

Faq

Frequently Asked Question

Who runs the audit?
An AICPA-licensed CPA firm from our pre-vetted partner network. soc2audit.ai prepares your evidence and controls; the CPA firm performs the audit and issues the attestation. That separation of duties is required: no software platform can attest under AICPA rules.
Vanta and Drata are systems of record: you get a dashboard and are expected to know what to do. soc2audit.ai is a guided journey: an AI copilot walks you through each phase, from gap assessment through audit sign-off. And we include an audit partner engagement in the workflow, not as a separate scramble at the end.
No. Penetration testing, vulnerability management, and virtual CISO services are offered by our parent company, Cyber Security Services, as optional add-ons. They surface in the platform when relevant to your control set, but they are never required and never bundled into the base subscription.
It depends on where you’re starting. Companies with mature security programs can complete the preparation phase in a few weeks. Companies starting from zero typically take 2–3 months to close gaps and gather evidence. The AI copilot gives you a personalized timeline after your gap assessment.
Yes. If you already have an AICPA-licensed CPA firm you want to work with, they can be onboarded to the platform as an audit partner. Most firms are happy to work inside a structured evidence platform, because it reduces their fieldwork hours.
SOC 2 Type I and Type II are our focus. Controls are also mapped to ISO 27001, HIPAA, and CJIS, included in the base subscription, so your work carries over.
Yes. Our SOC 2 Type II report is available once a year, under NDA on request.