
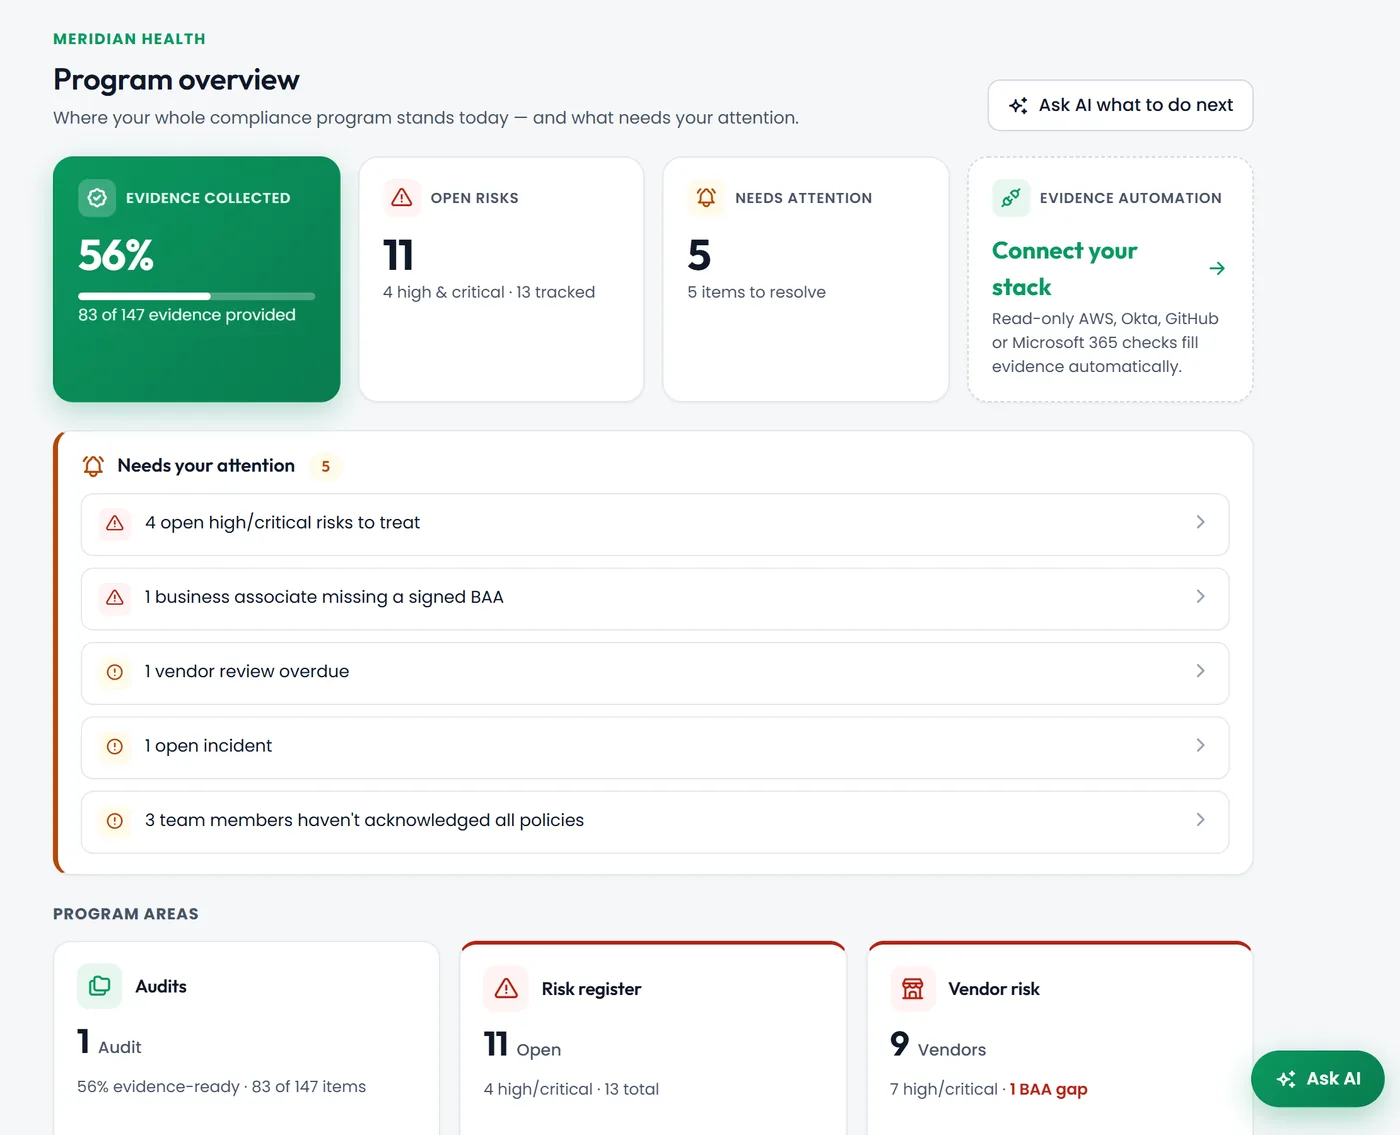
Overview
Evidence progress, open risks and everything that needs attention, pulled together from every part of the program.
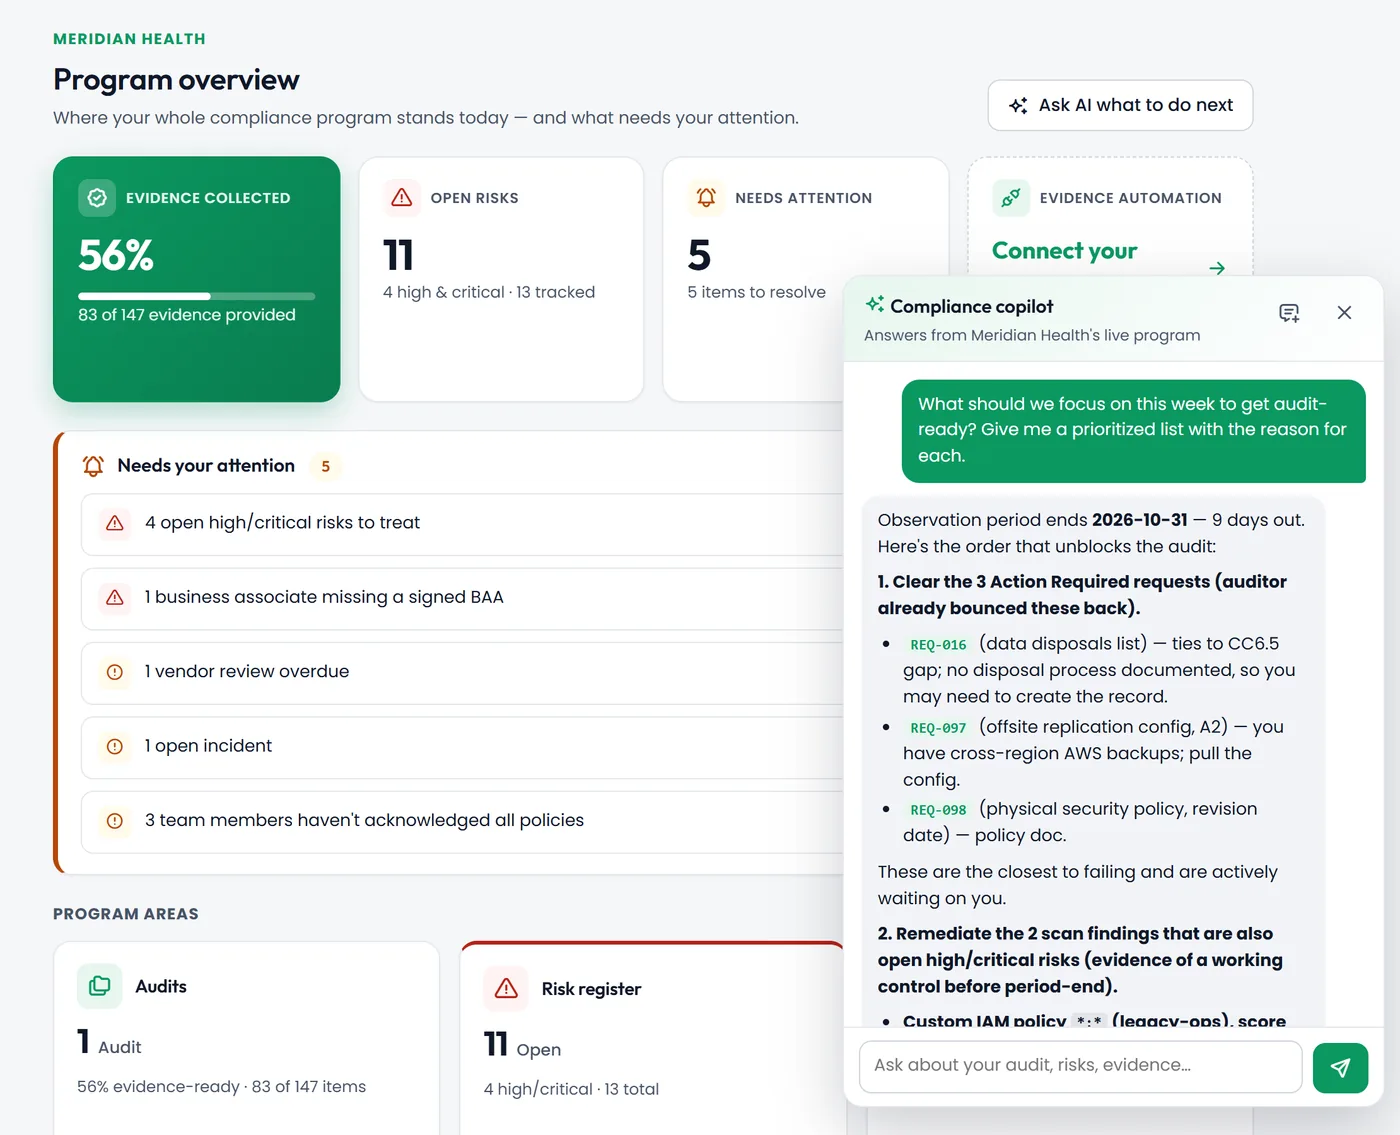
Overview › Ask AI · AI-assisted
The compliance copilot answers from your live data: what is blocking the audit, what your auditor sent back, which risks matter most. It is on every page.
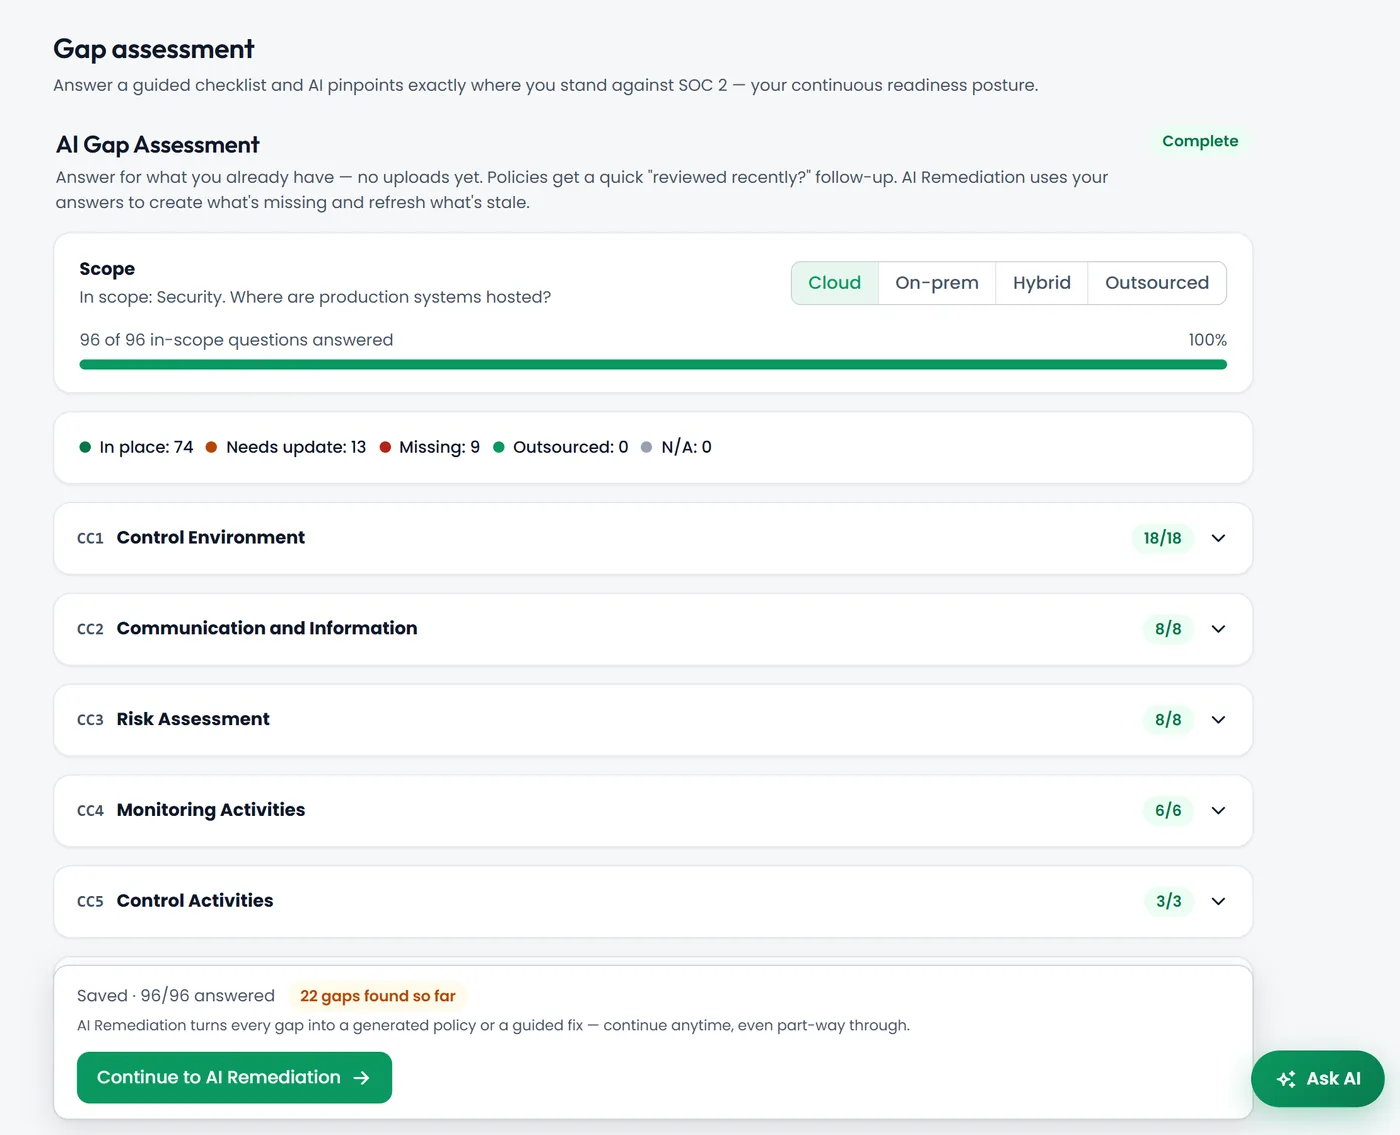
Readiness › Gap assessment · AI-assisted
About 100 plain-English questions mapped to the AICPA Trust Services Criteria. AI drafts answers from your company profile.
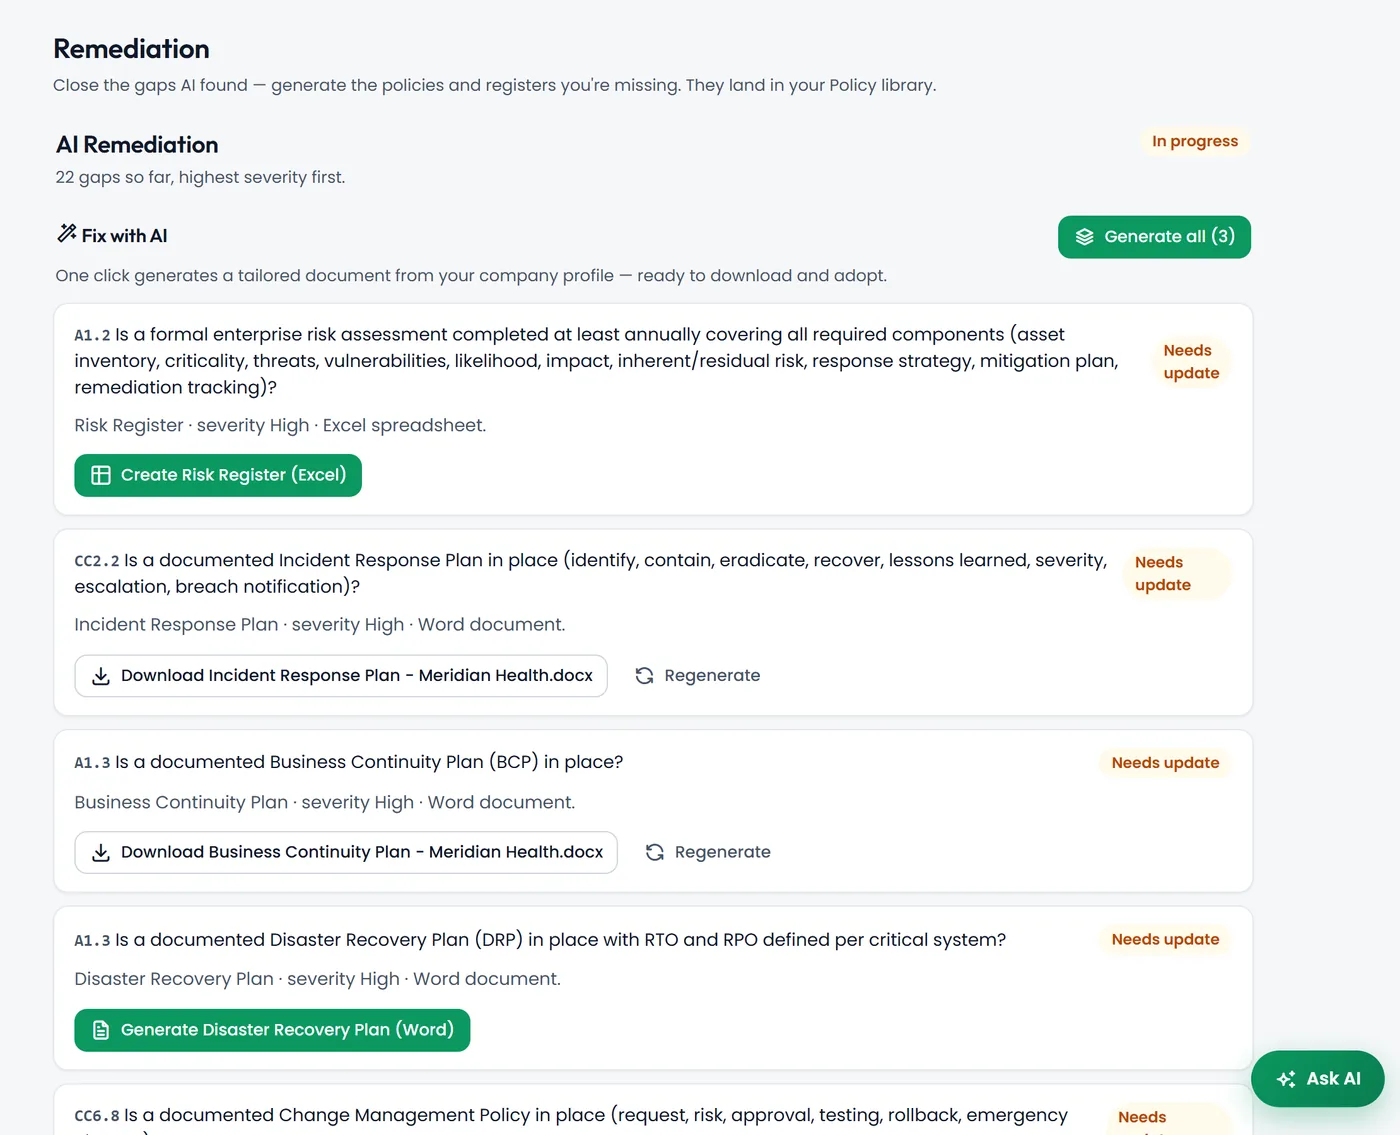
Readiness › Remediation · AI-assisted
Turn each gap into a policy, plan or register written for your company and your stack, not a generic template.
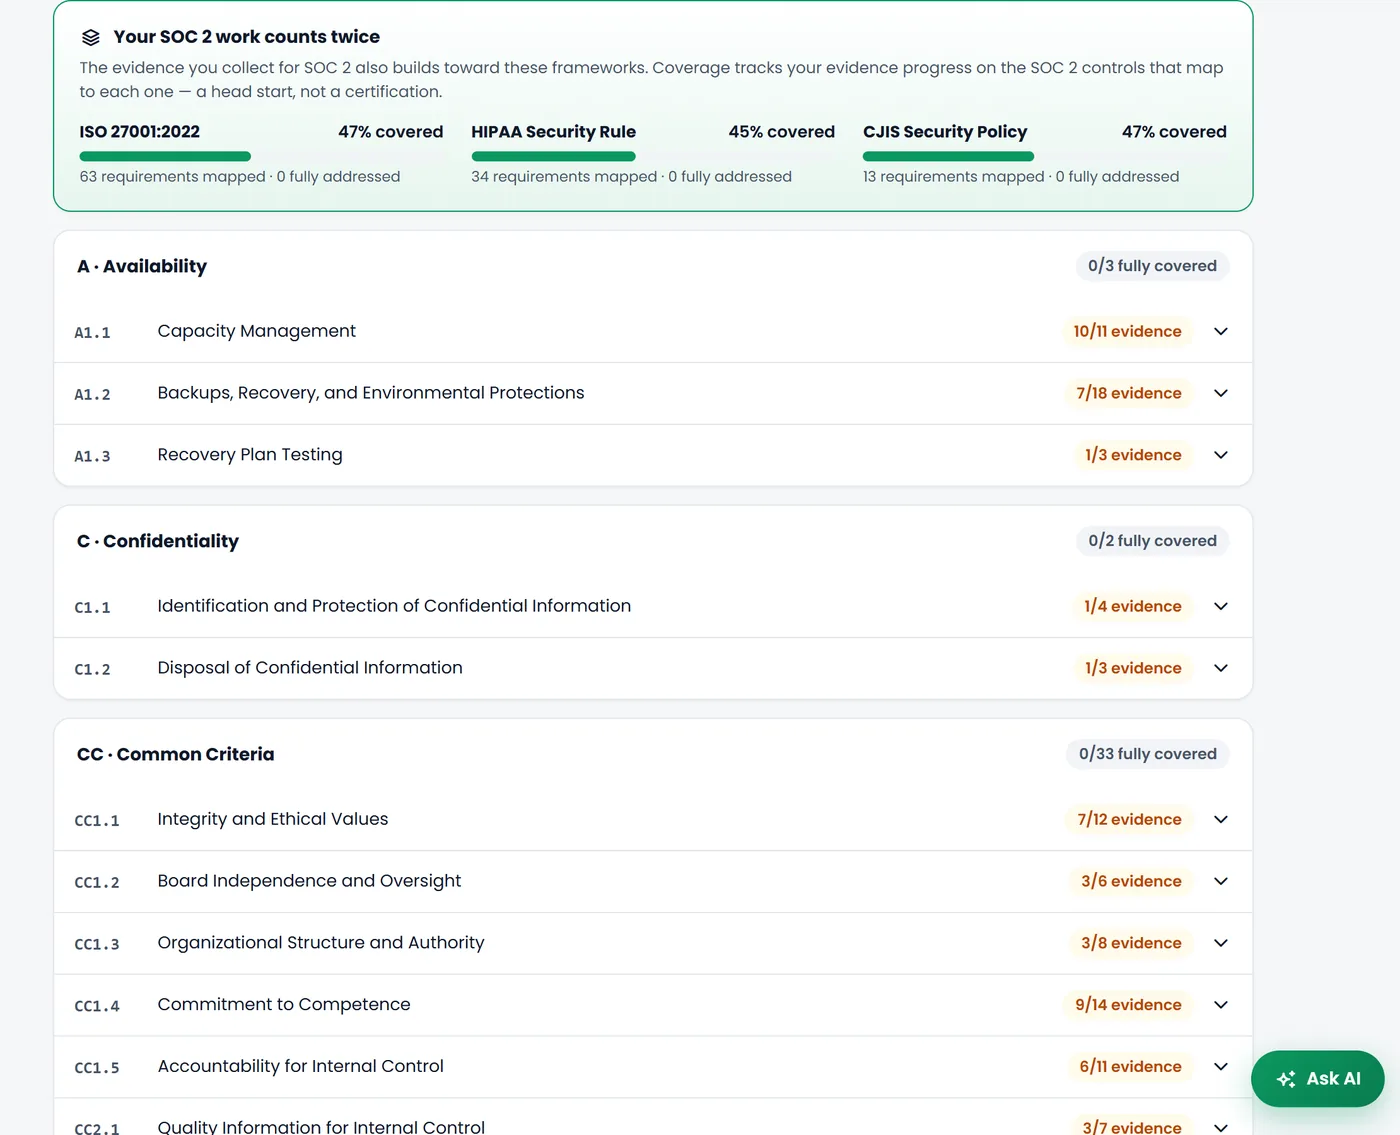
Readiness › Controls map
Every in-scope criterion with its evidence and policies, plus live coverage toward other frameworks from the same work.
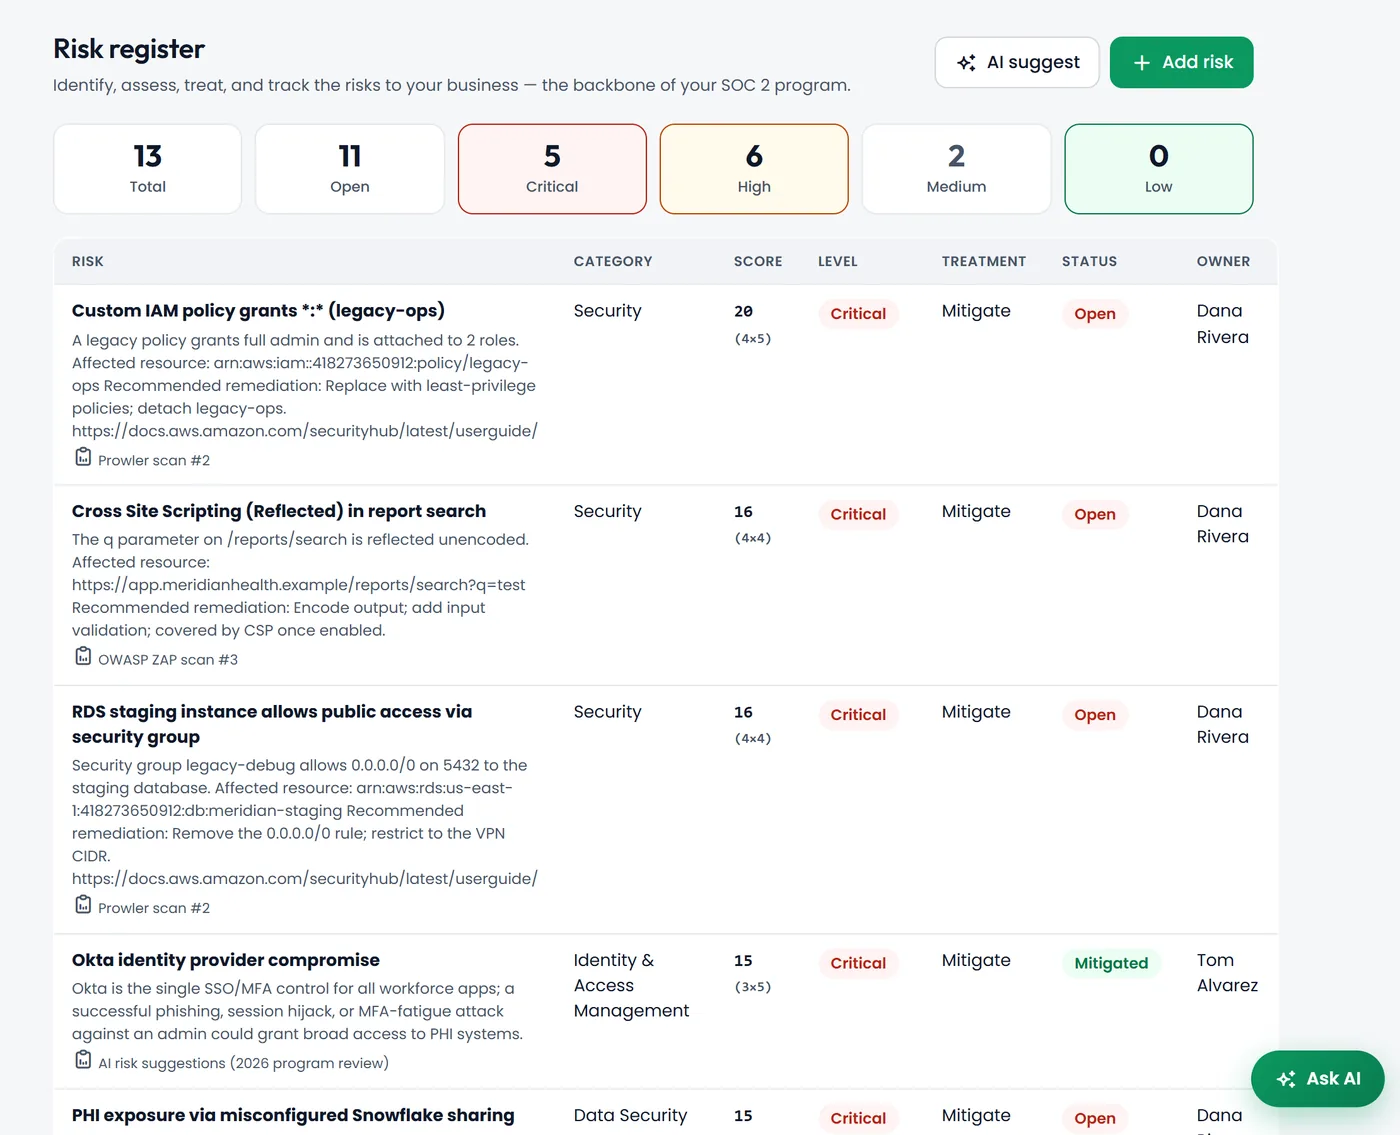
Governance › Risk register · AI-assisted
Score, treat and track every risk. AI suggests risks specific to your business, and scan findings feed straight in.
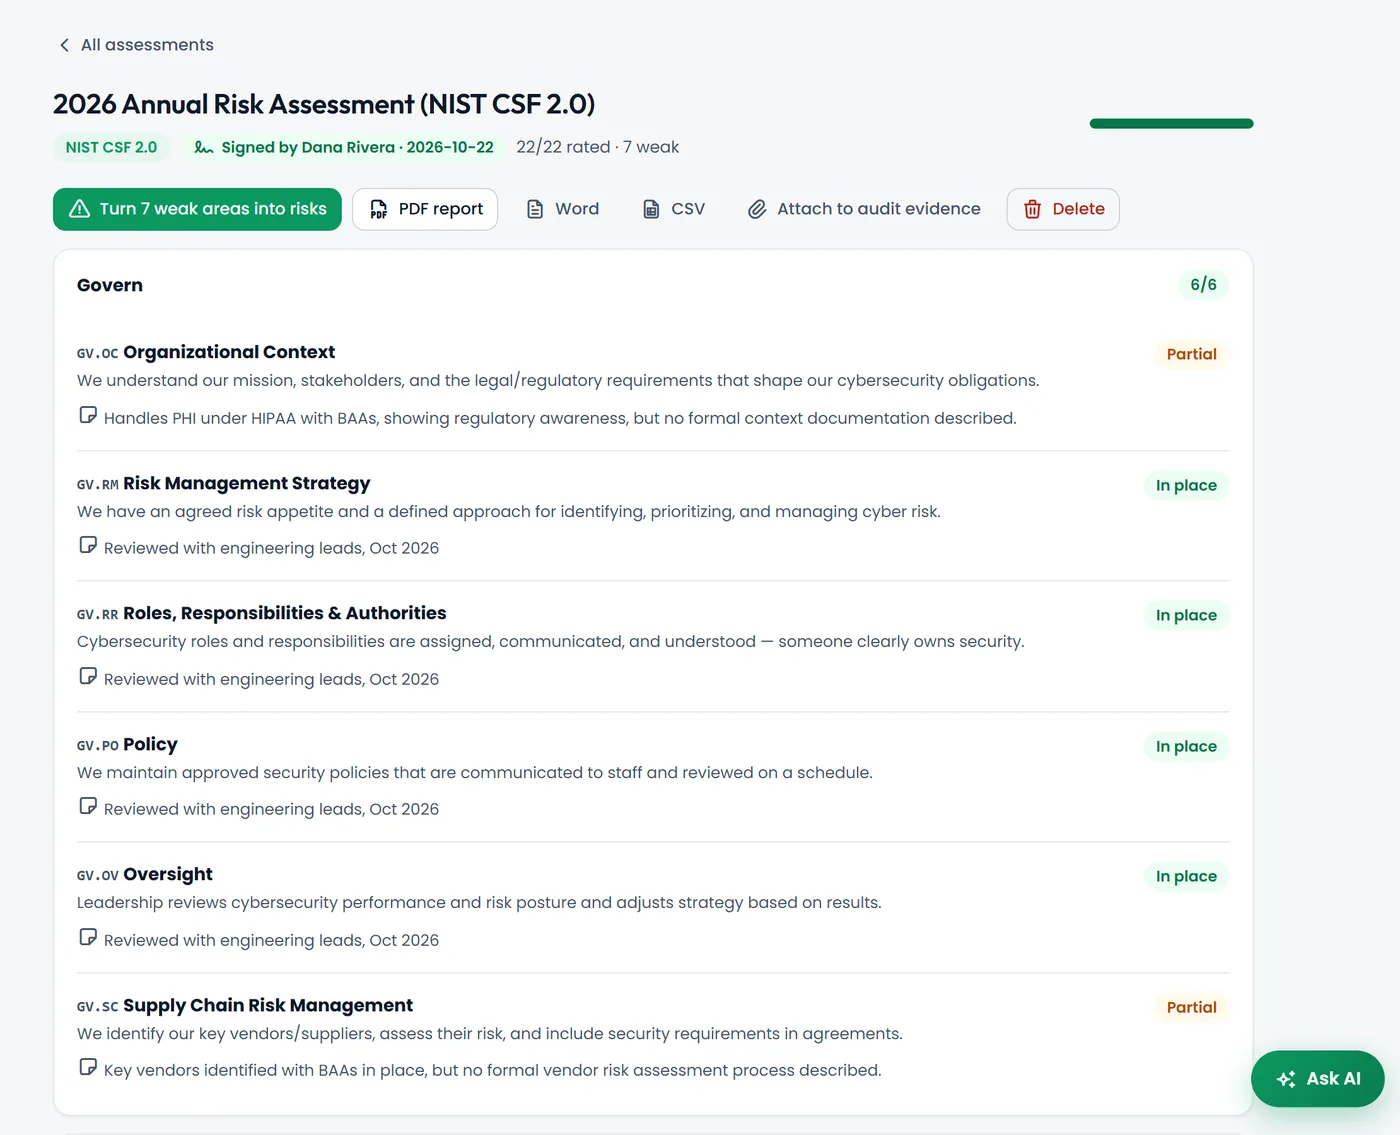
Governance › Risk assessments · AI-assisted
Assess against NIST CSF 2.0, CIS Controls v8.1 or the CJIS Security Policy. AI drafts the ratings and turns weak areas into risks.
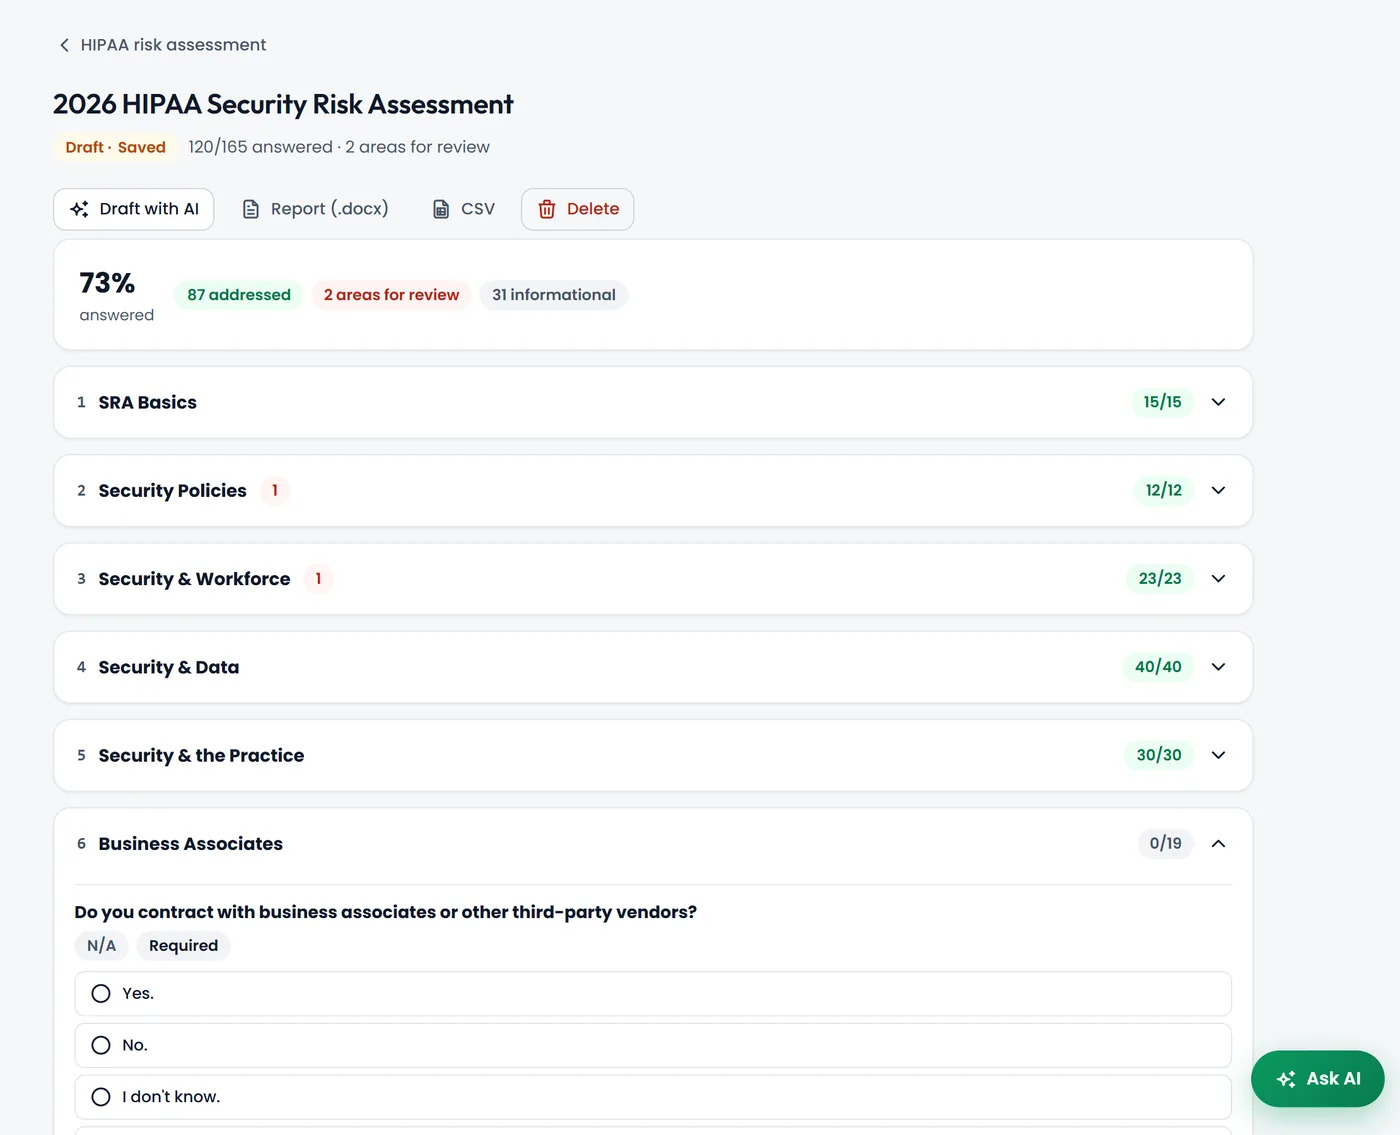
Governance › HIPAA risk assessment · AI-assisted
Built on the ONC/HHS SRA Tool method: seven sections and 165 questions mapped to the HIPAA Security Rule. AI drafts answers and shows its reasoning.
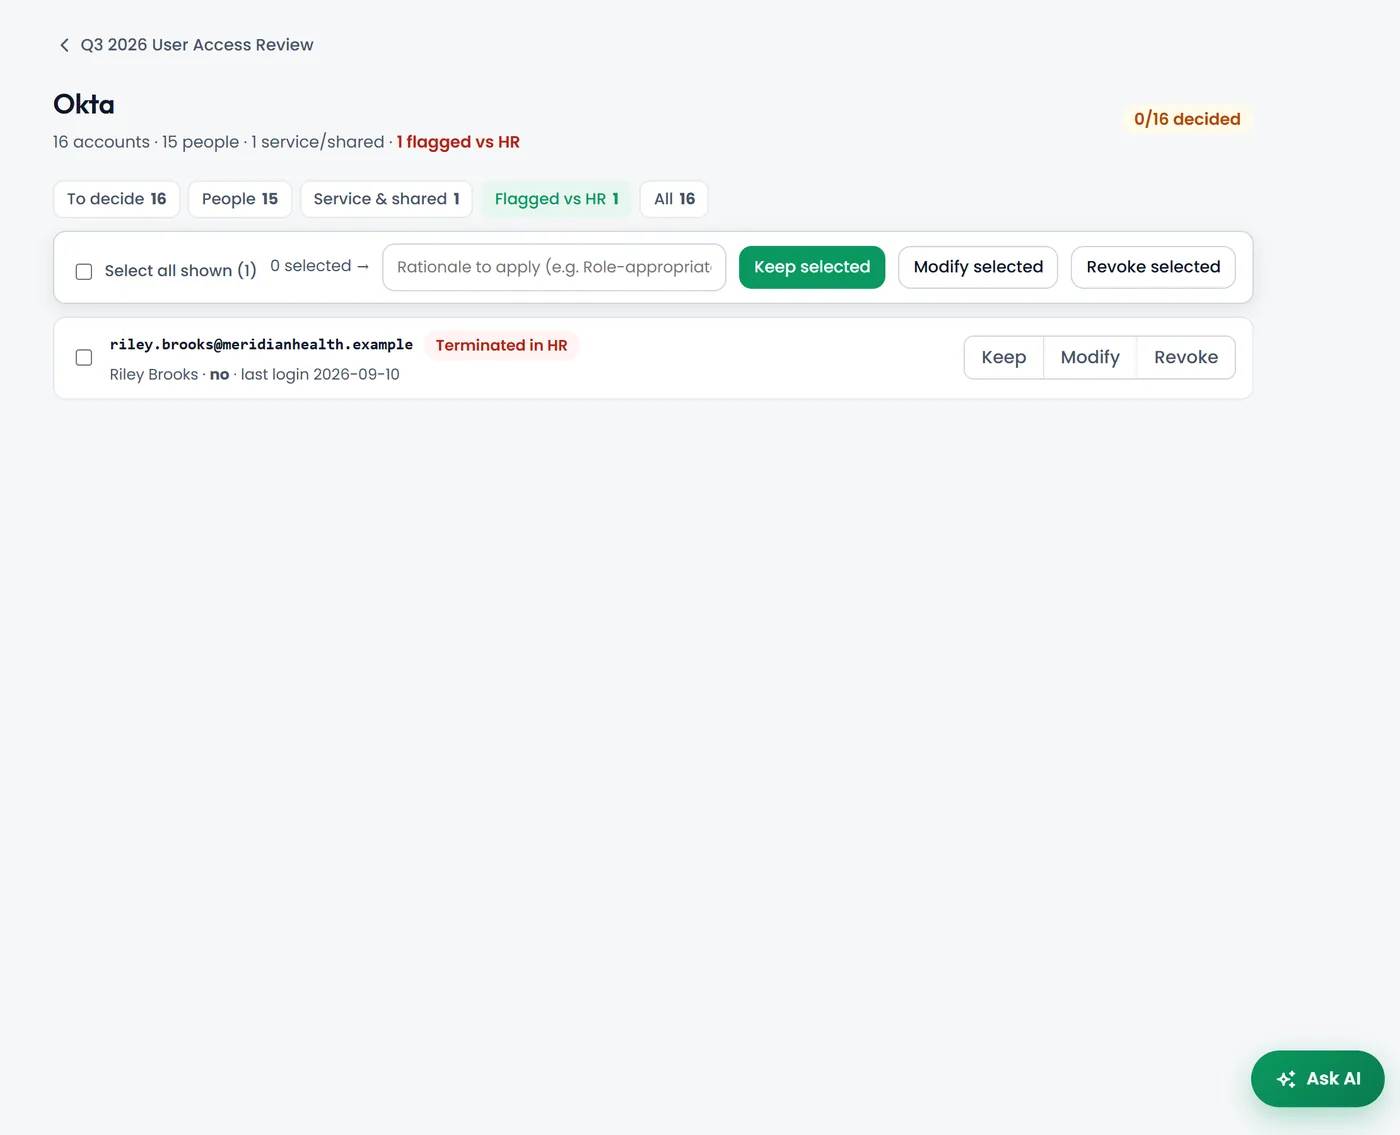
Governance › User access review
Compare your HR roster with each system's user list. Former employees and unknown accounts are flagged for you.
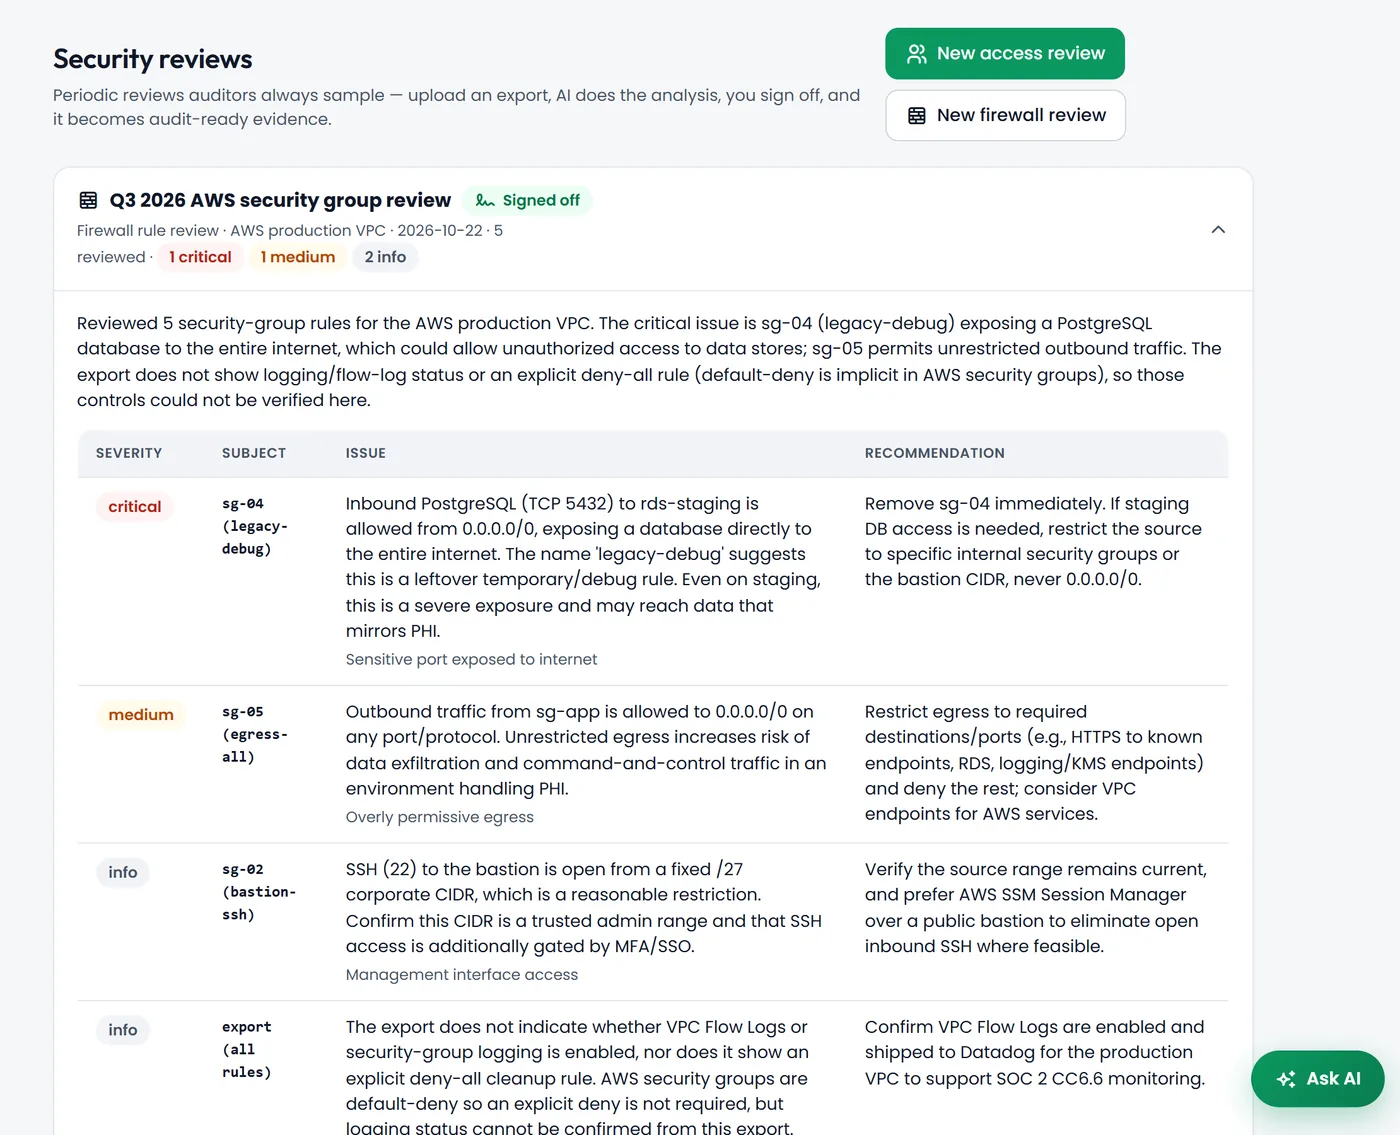
Governance › Security reviews · AI-assisted
Upload a firewall export and AI finds the risky rules. Sign it off and it becomes audit evidence.
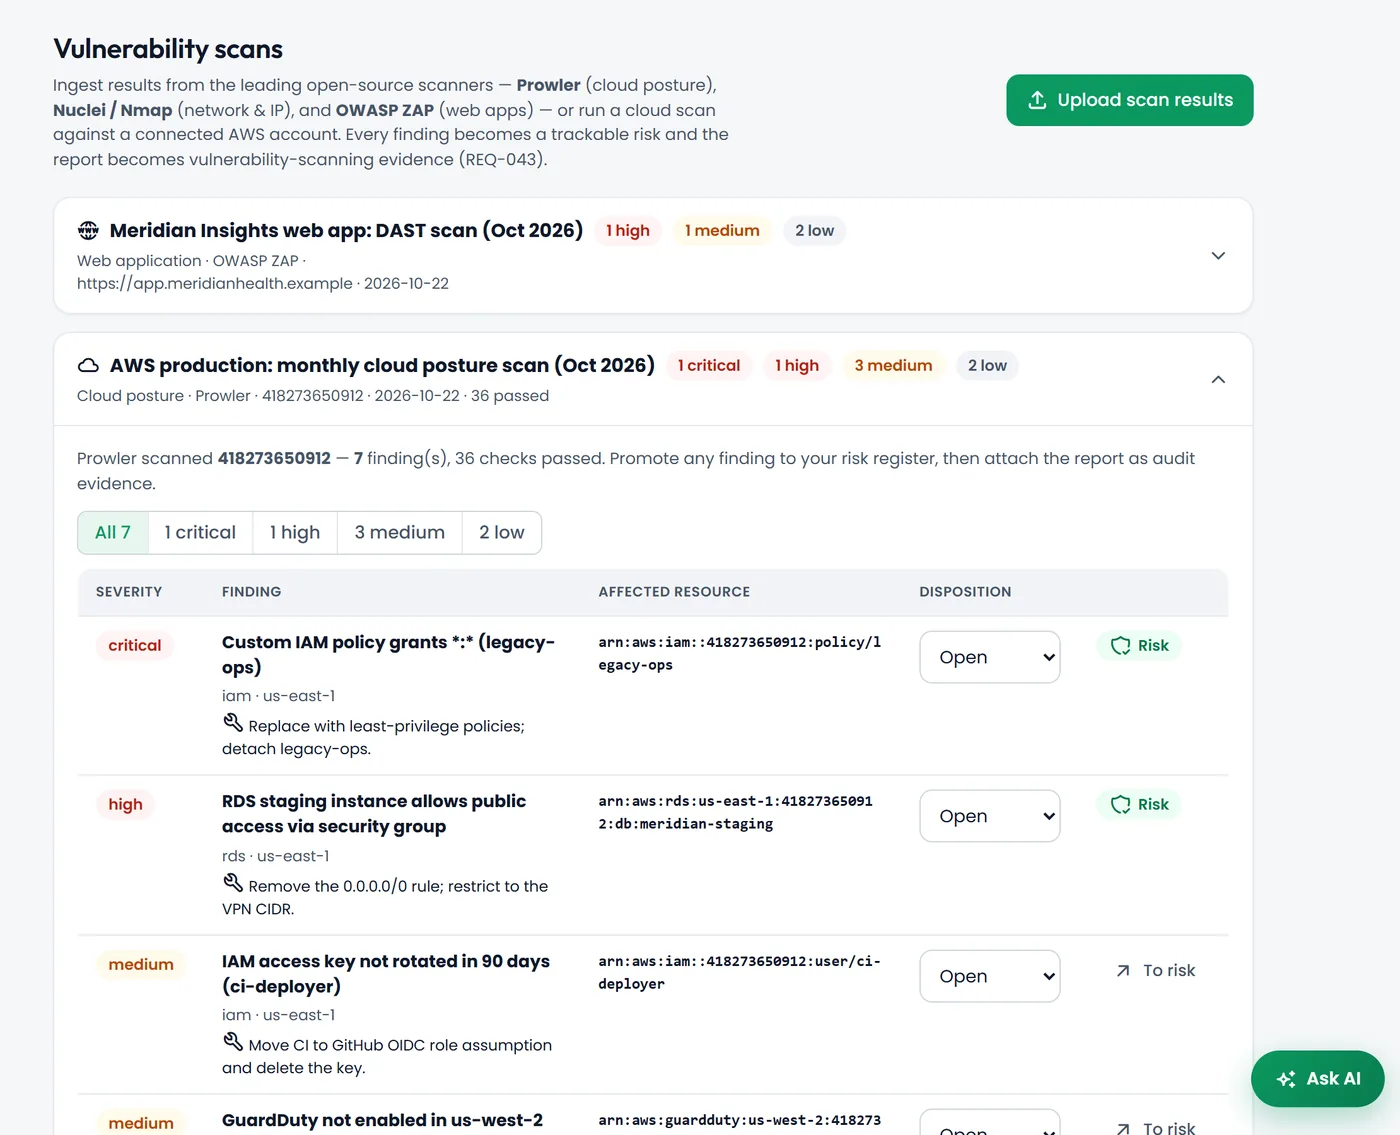
Governance › Vulnerability scans
Import results from Prowler, Nuclei or OWASP ZAP. Promote findings to the risk register and attach the report to your audit.
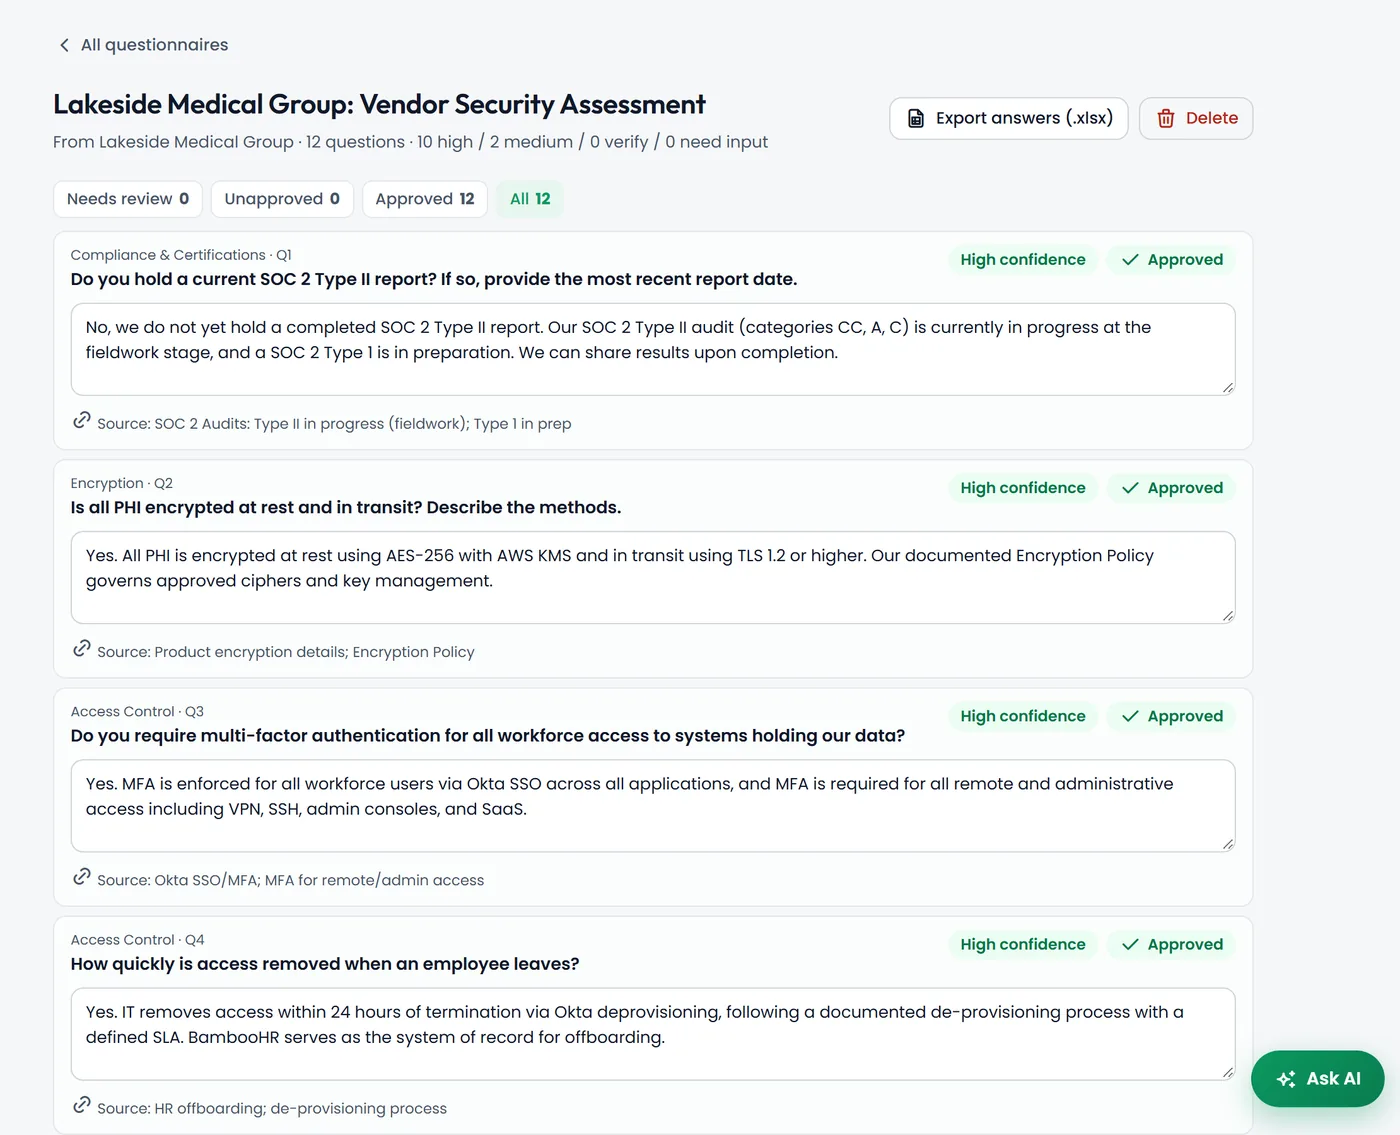
Governance › Questionnaires · AI-assisted
Paste or upload a questionnaire. AI answers it from your own program, with a confidence level on every answer.
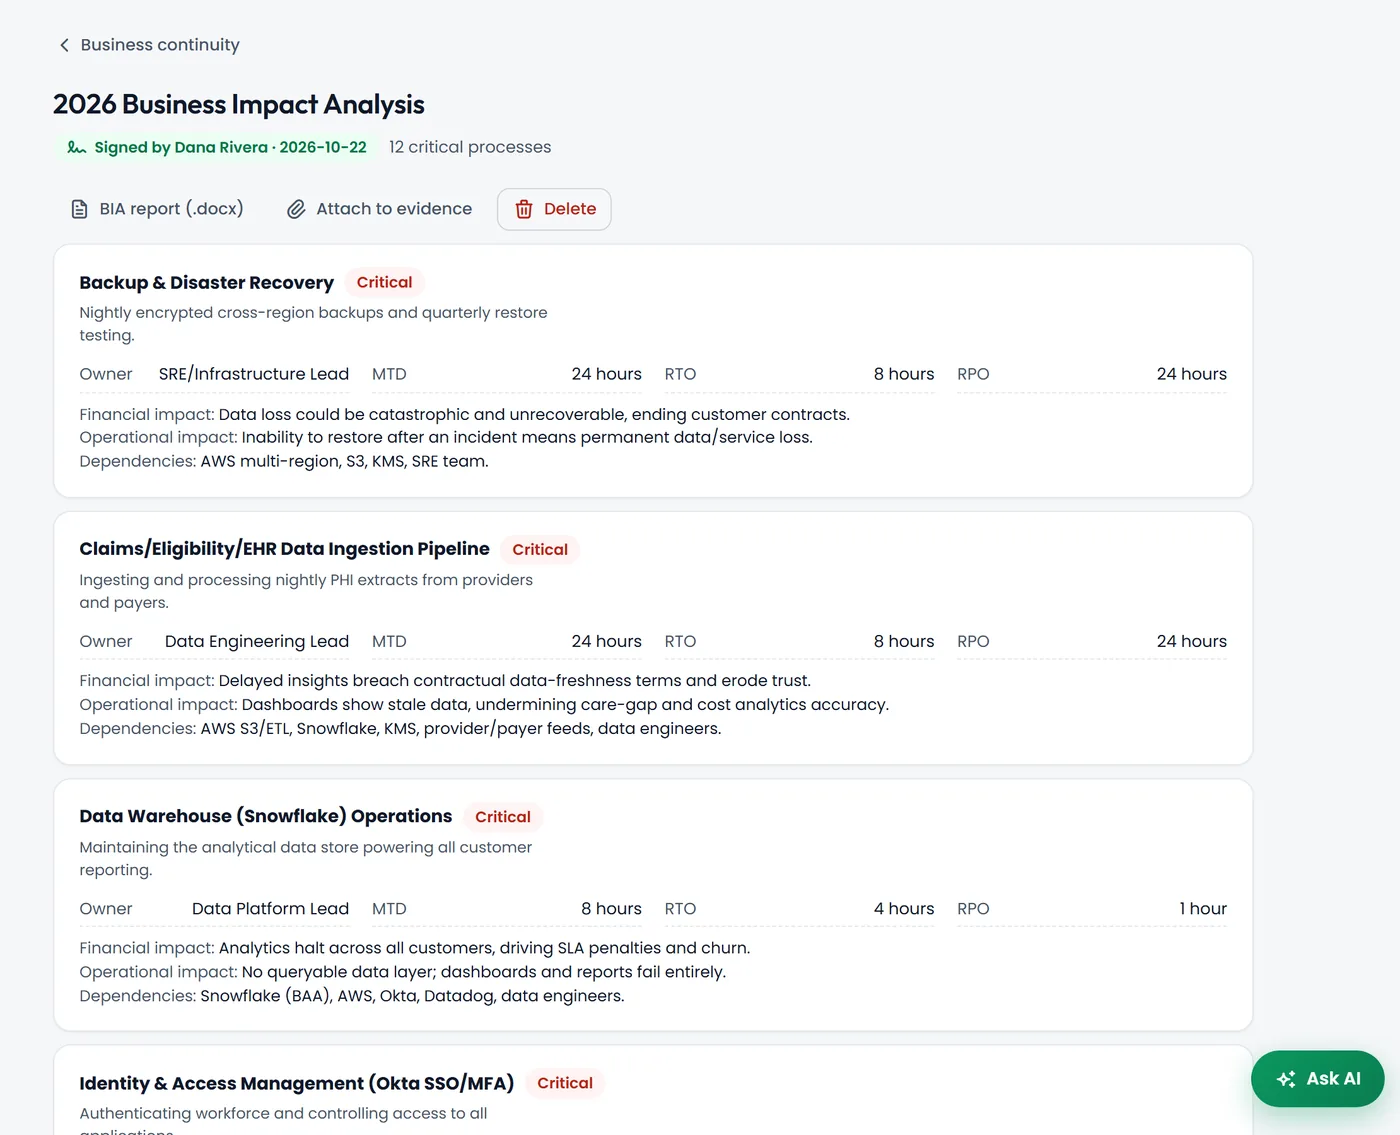
Governance › Business continuity · AI-assisted
A Business Impact Analysis with AI-suggested critical processes and recovery targets, then a full continuity and disaster recovery plan built on it.
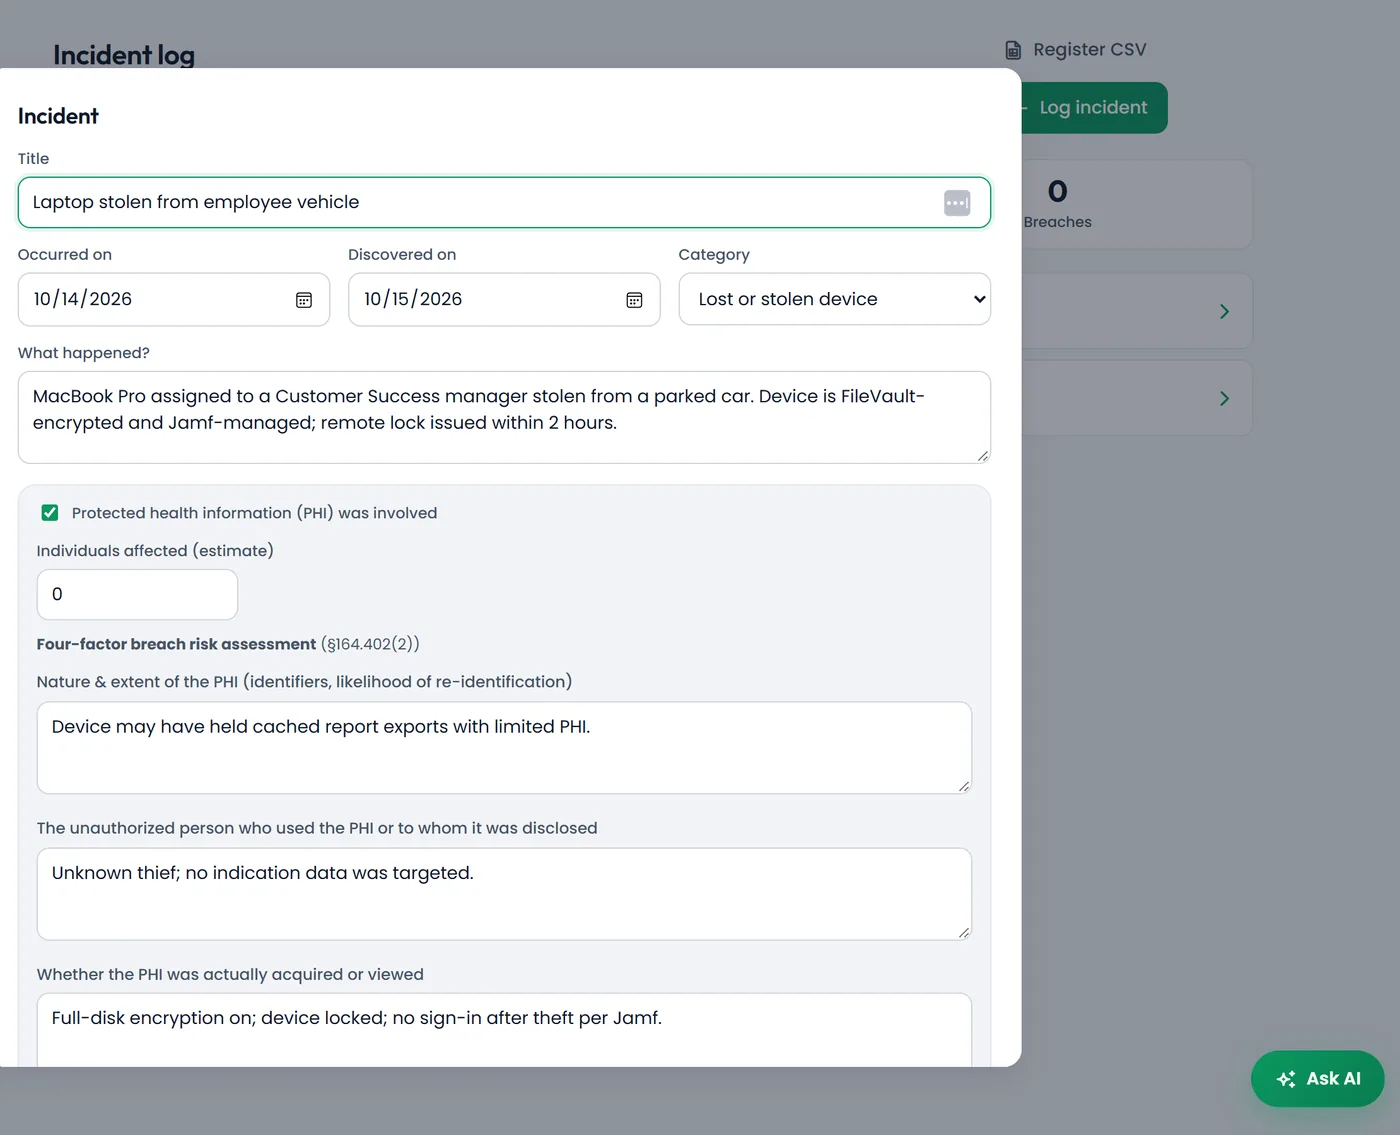
Governance › Incident log
Log security incidents with the HIPAA four-factor breach risk assessment and notification tracking built in.
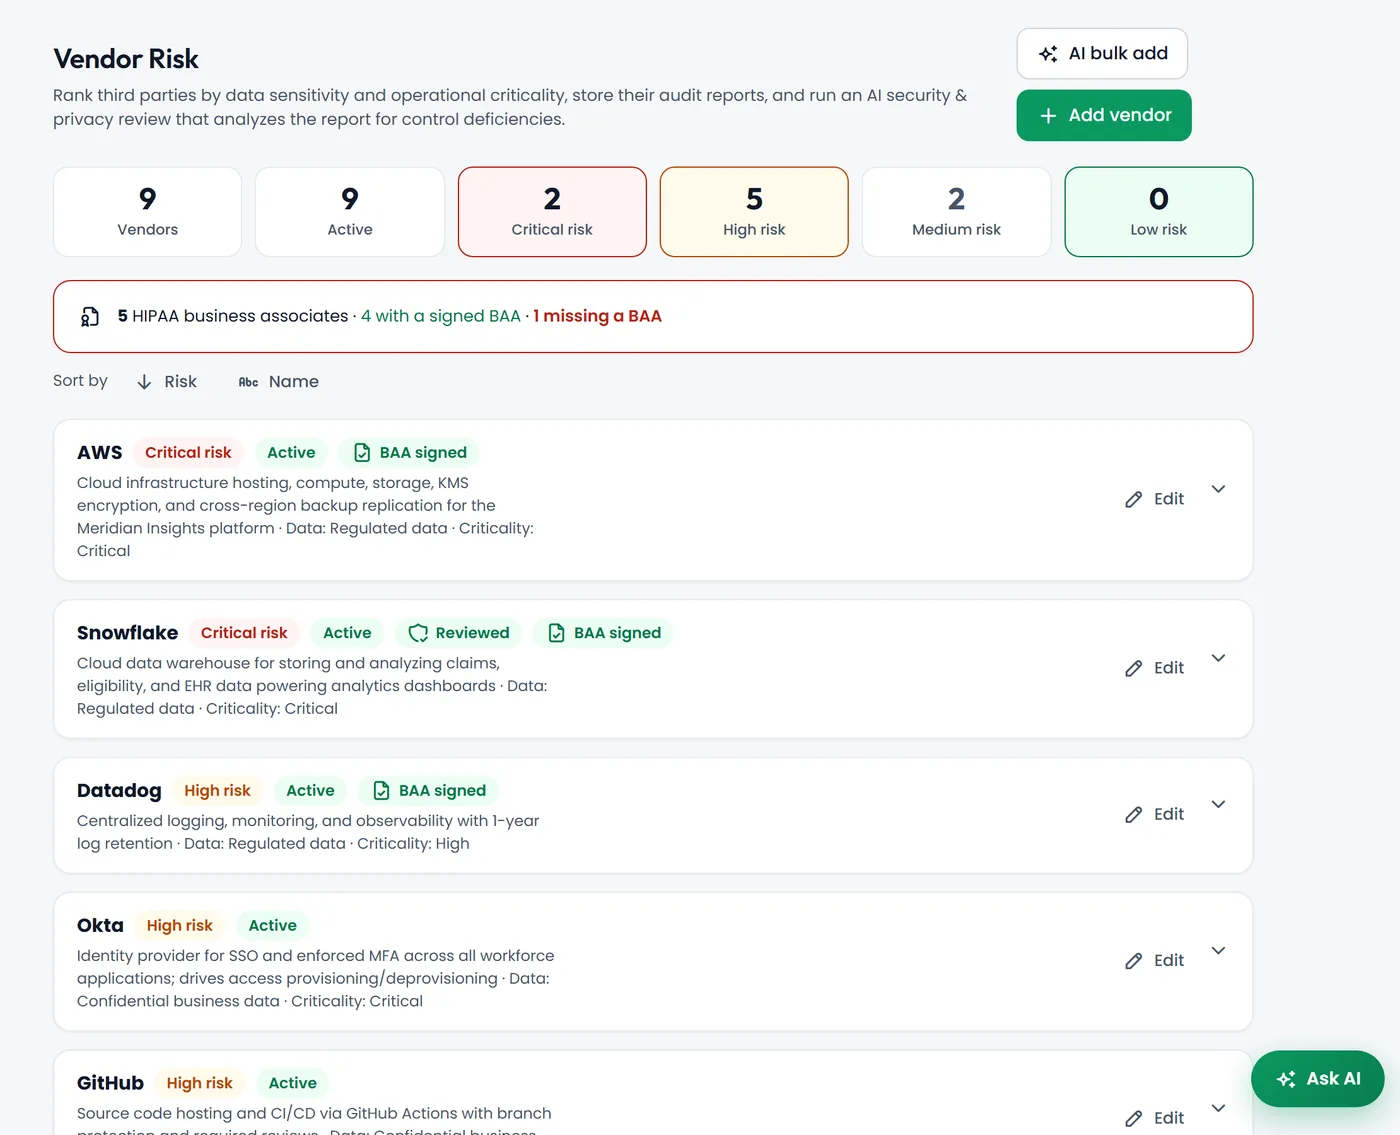
Governance › Vendor Risk · AI-assisted
Rank vendors by the data they hold and how critical they are. Track BAAs, store their audit reports and get an AI security review.
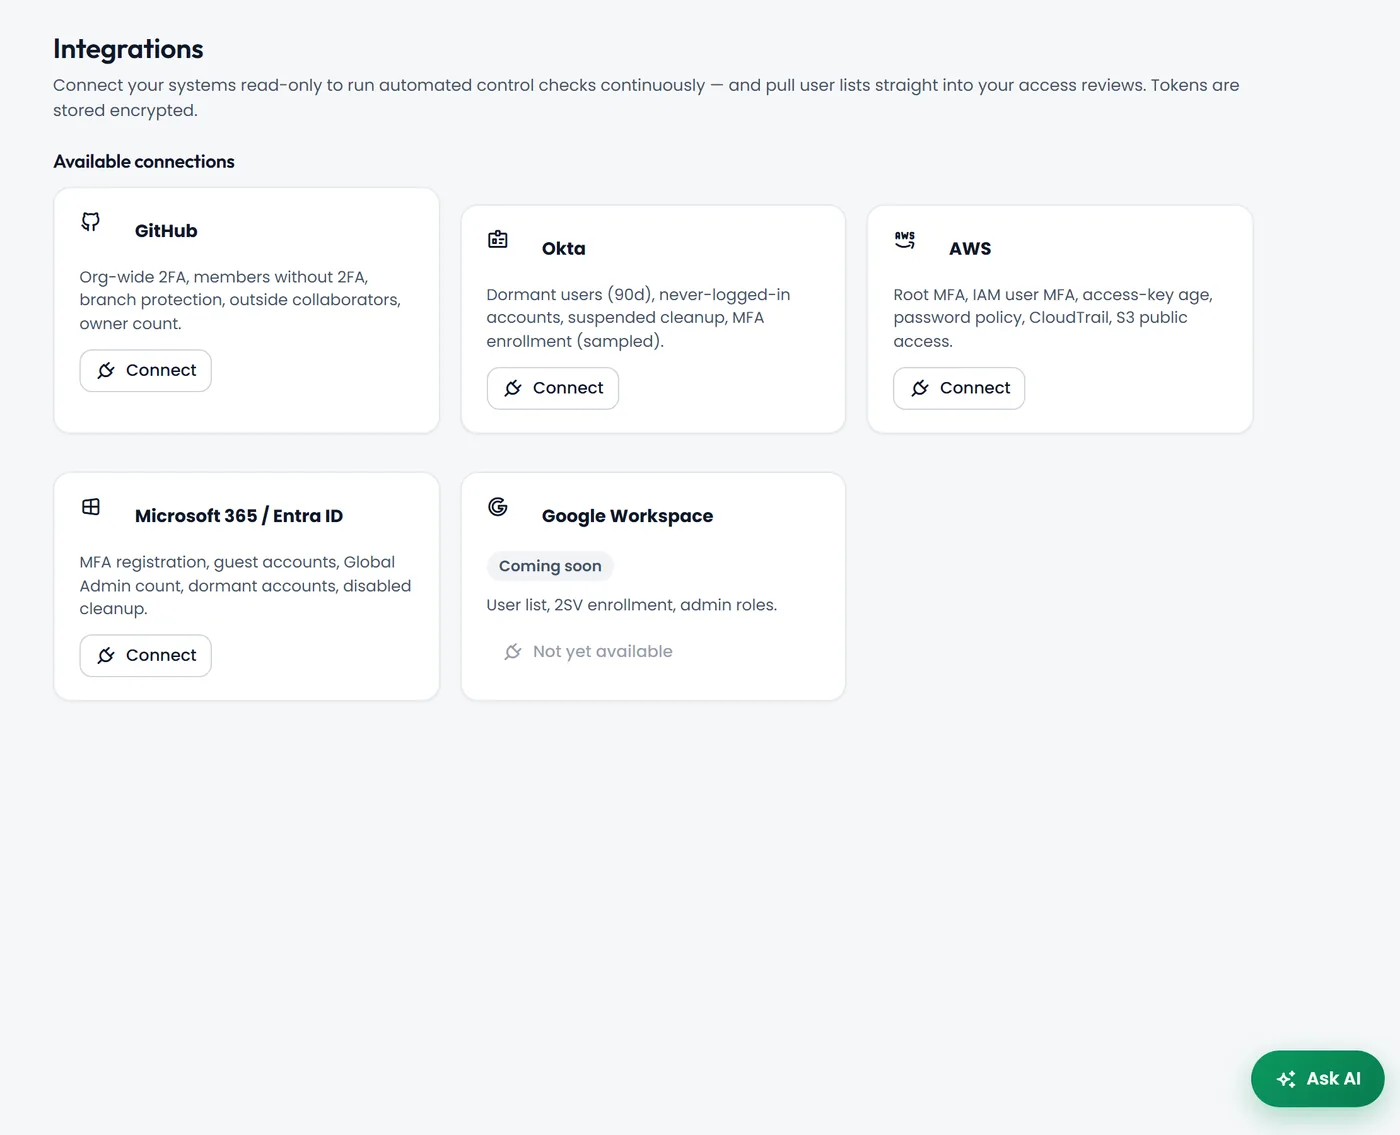
Governance › Integrations
Read-only connections to AWS, Okta, GitHub and Microsoft 365 run checks and fill matching evidence requests.
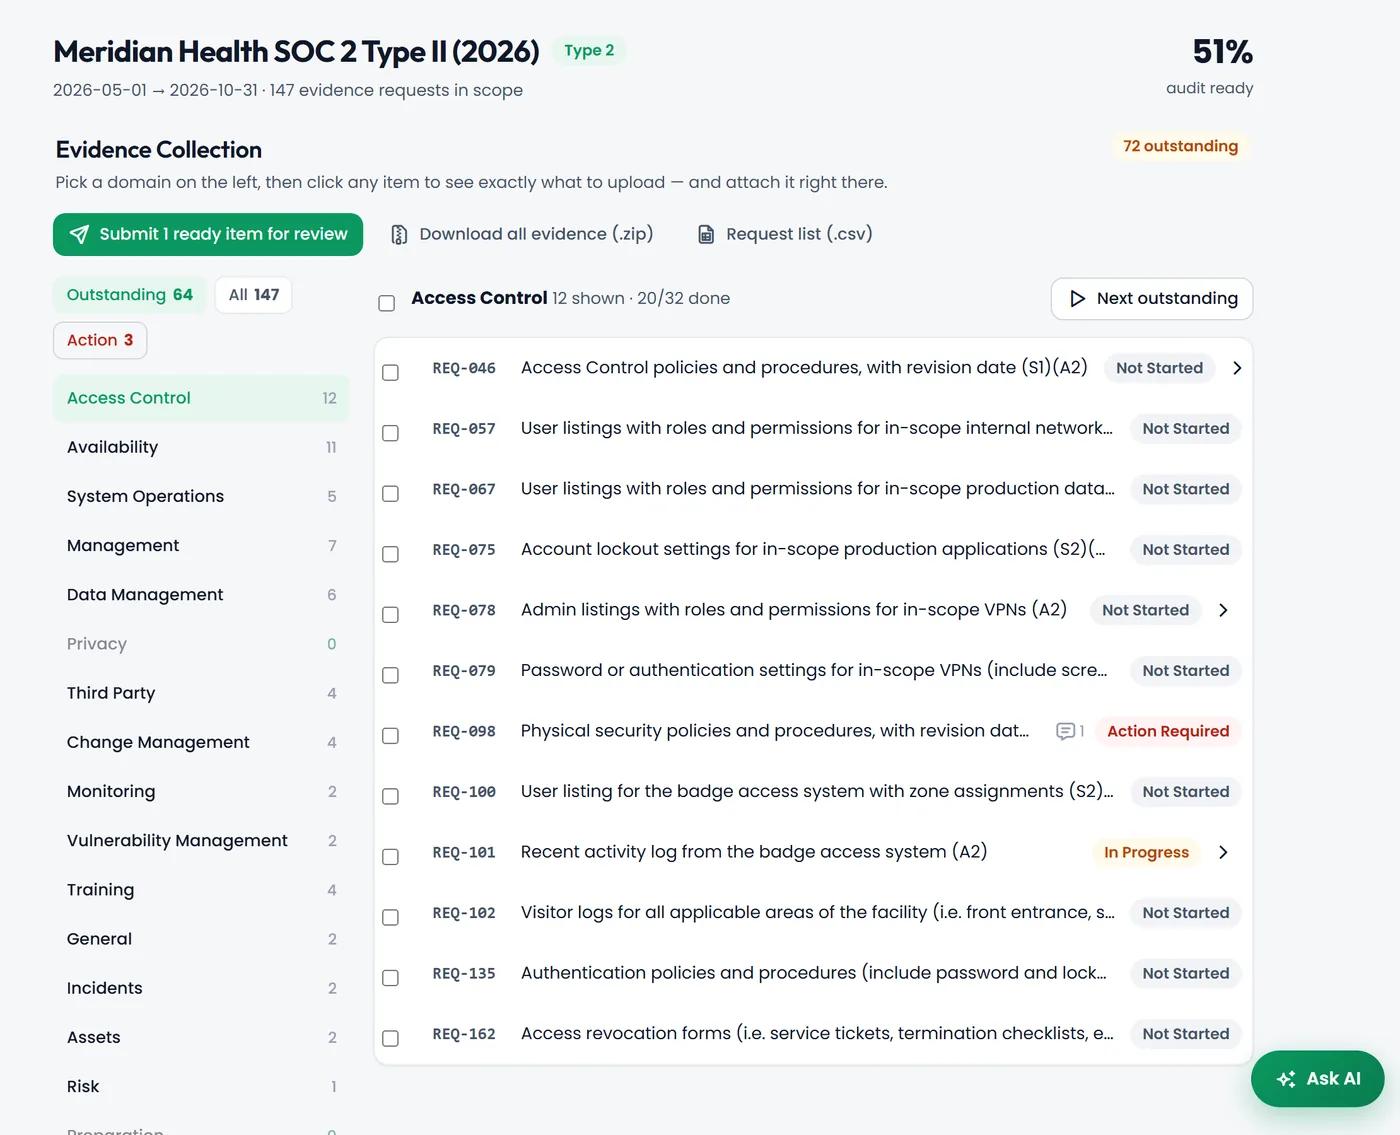
Audit › Evidence · AI-assisted
Every evidence request for a SOC 2 Type I or Type II, with guidance on what to upload, owners and status.
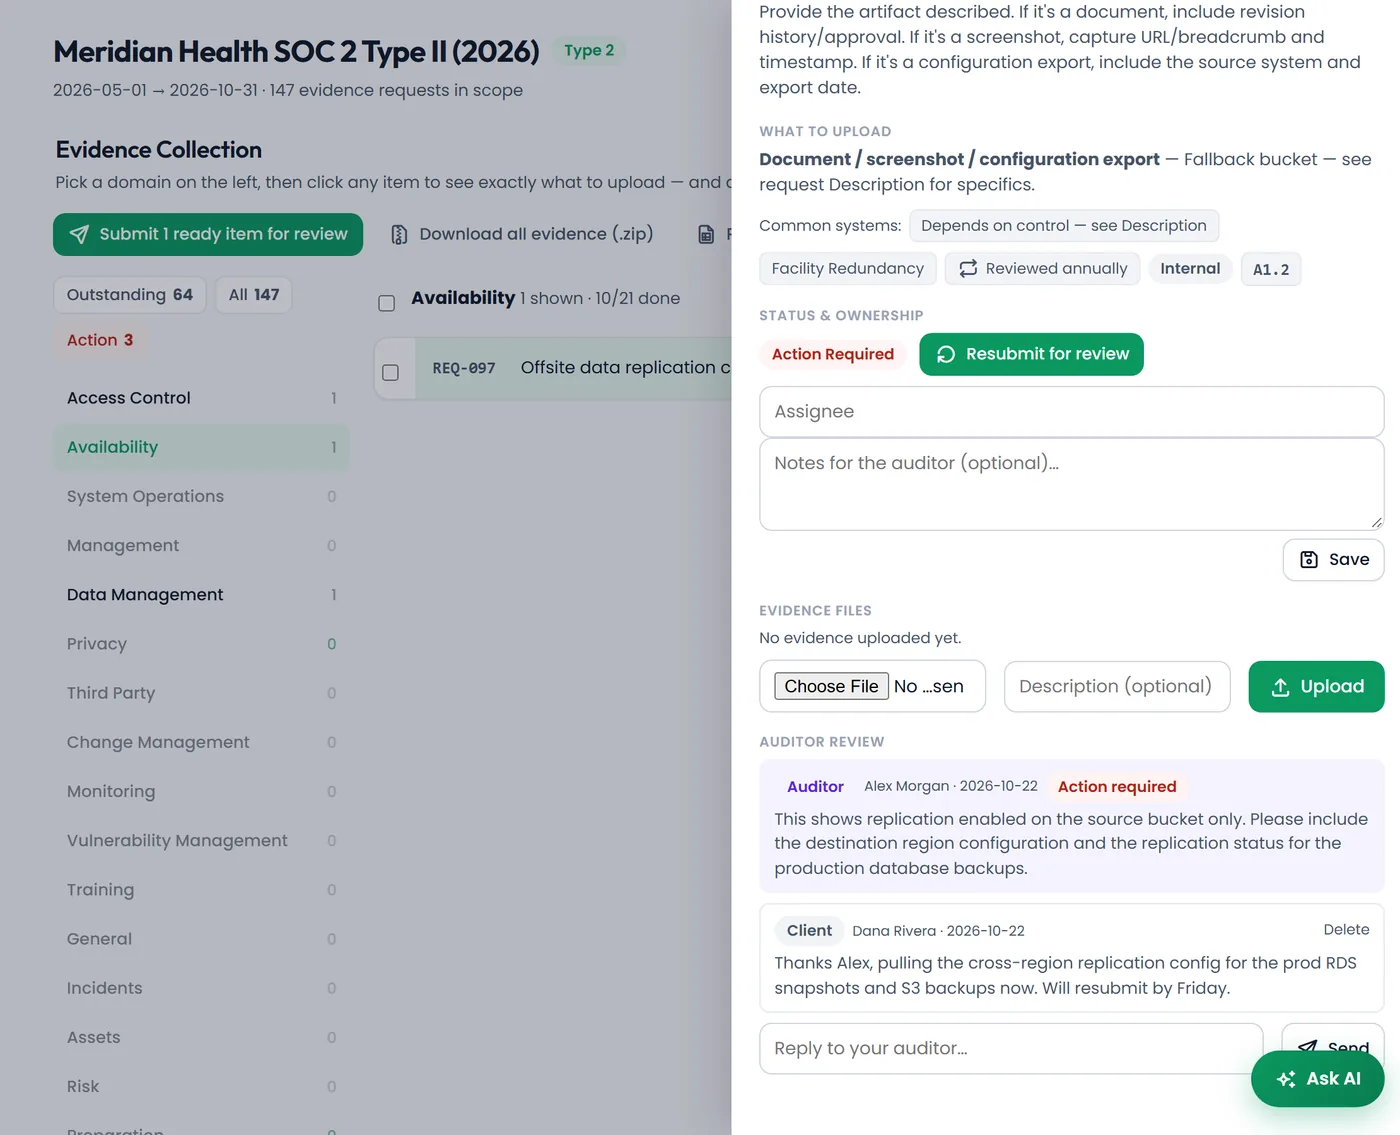
Audit › Review thread
When the auditor needs something changed, the note and your reply live on the evidence item itself.
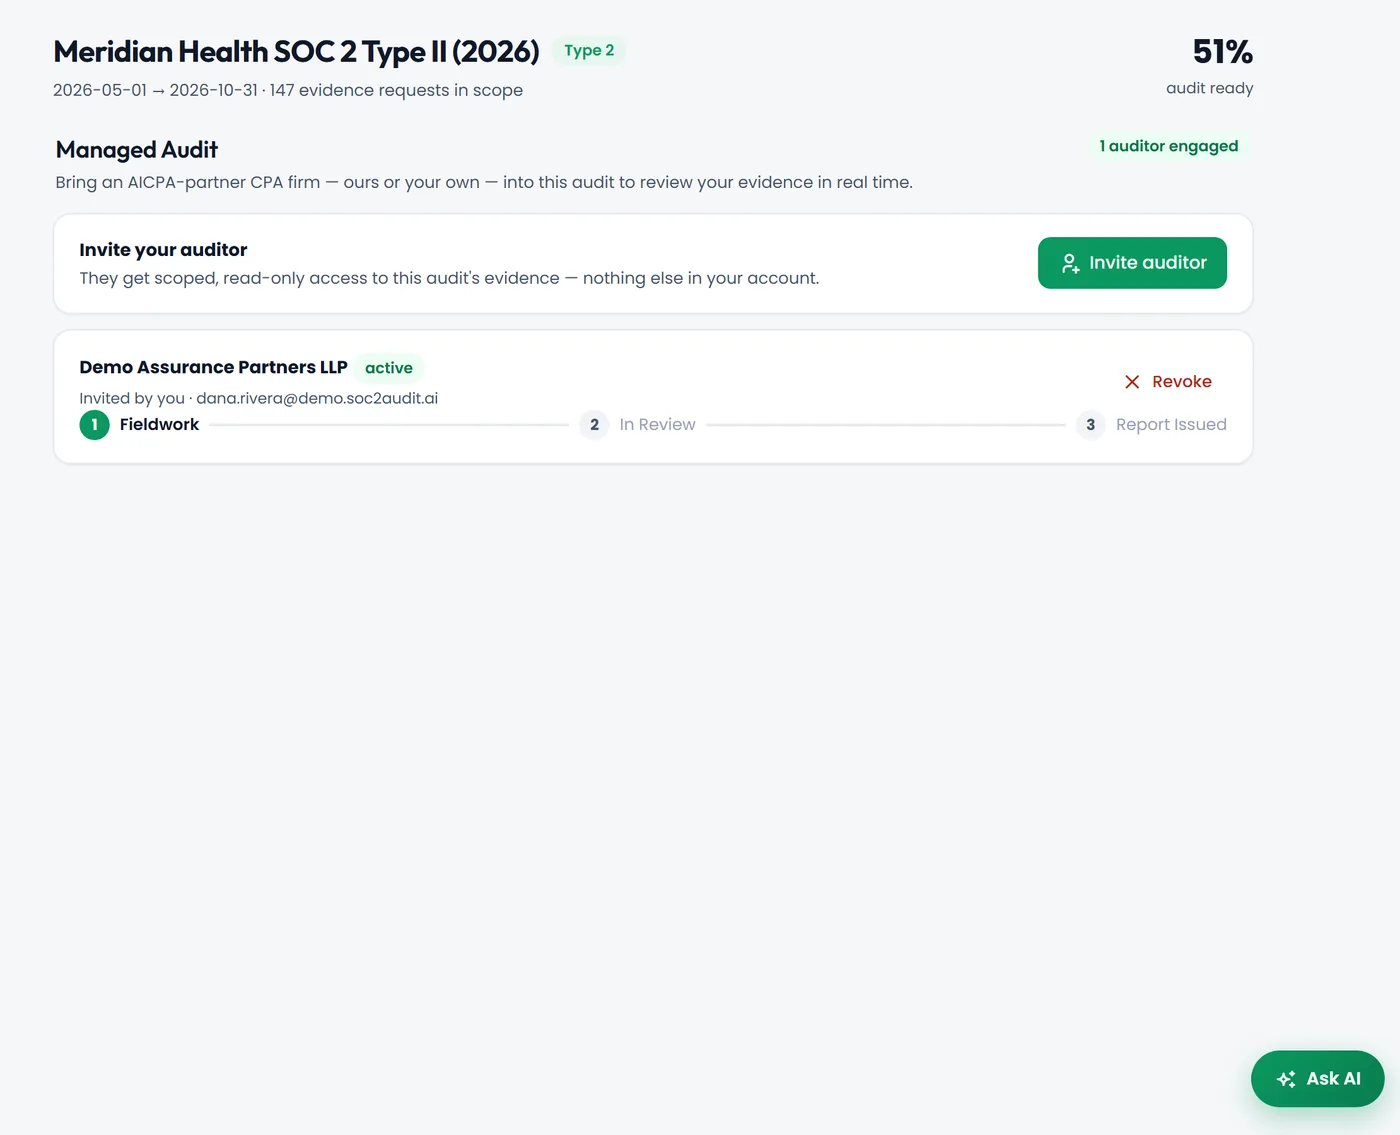
Audit › Managed audit
Work with an AICPA-licensed CPA firm from our network, or your own. They get access to that audit only.
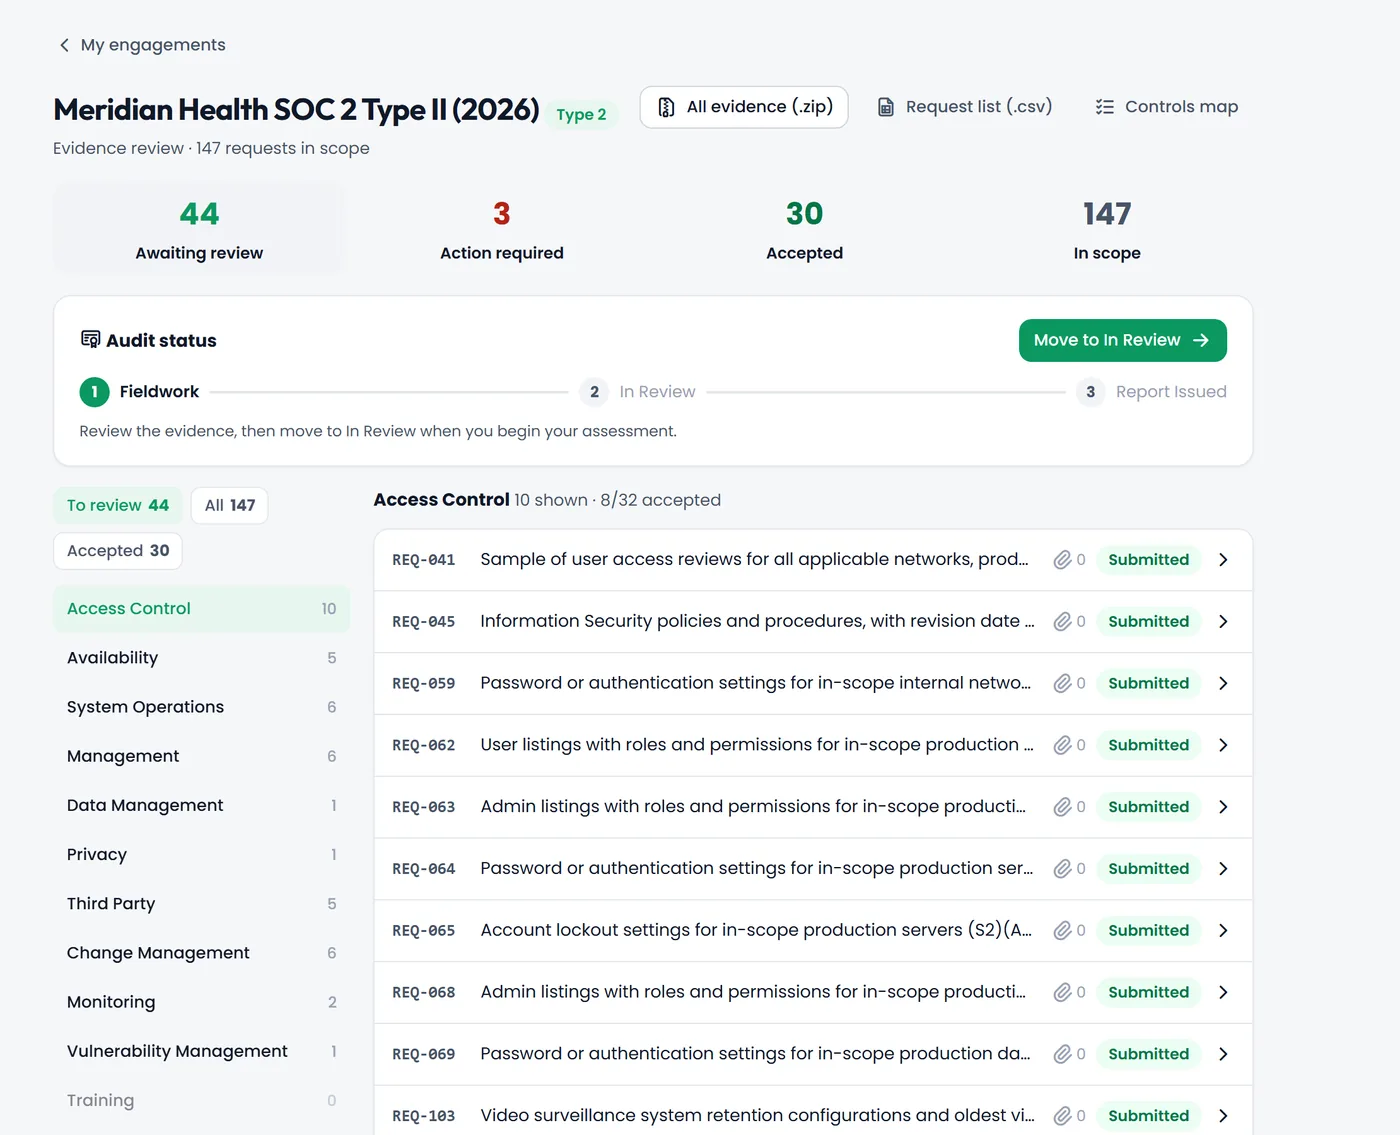
Audit › Auditor's view
The audit firm reviews the same request list, accepts evidence or sends it back, and asks for samples.
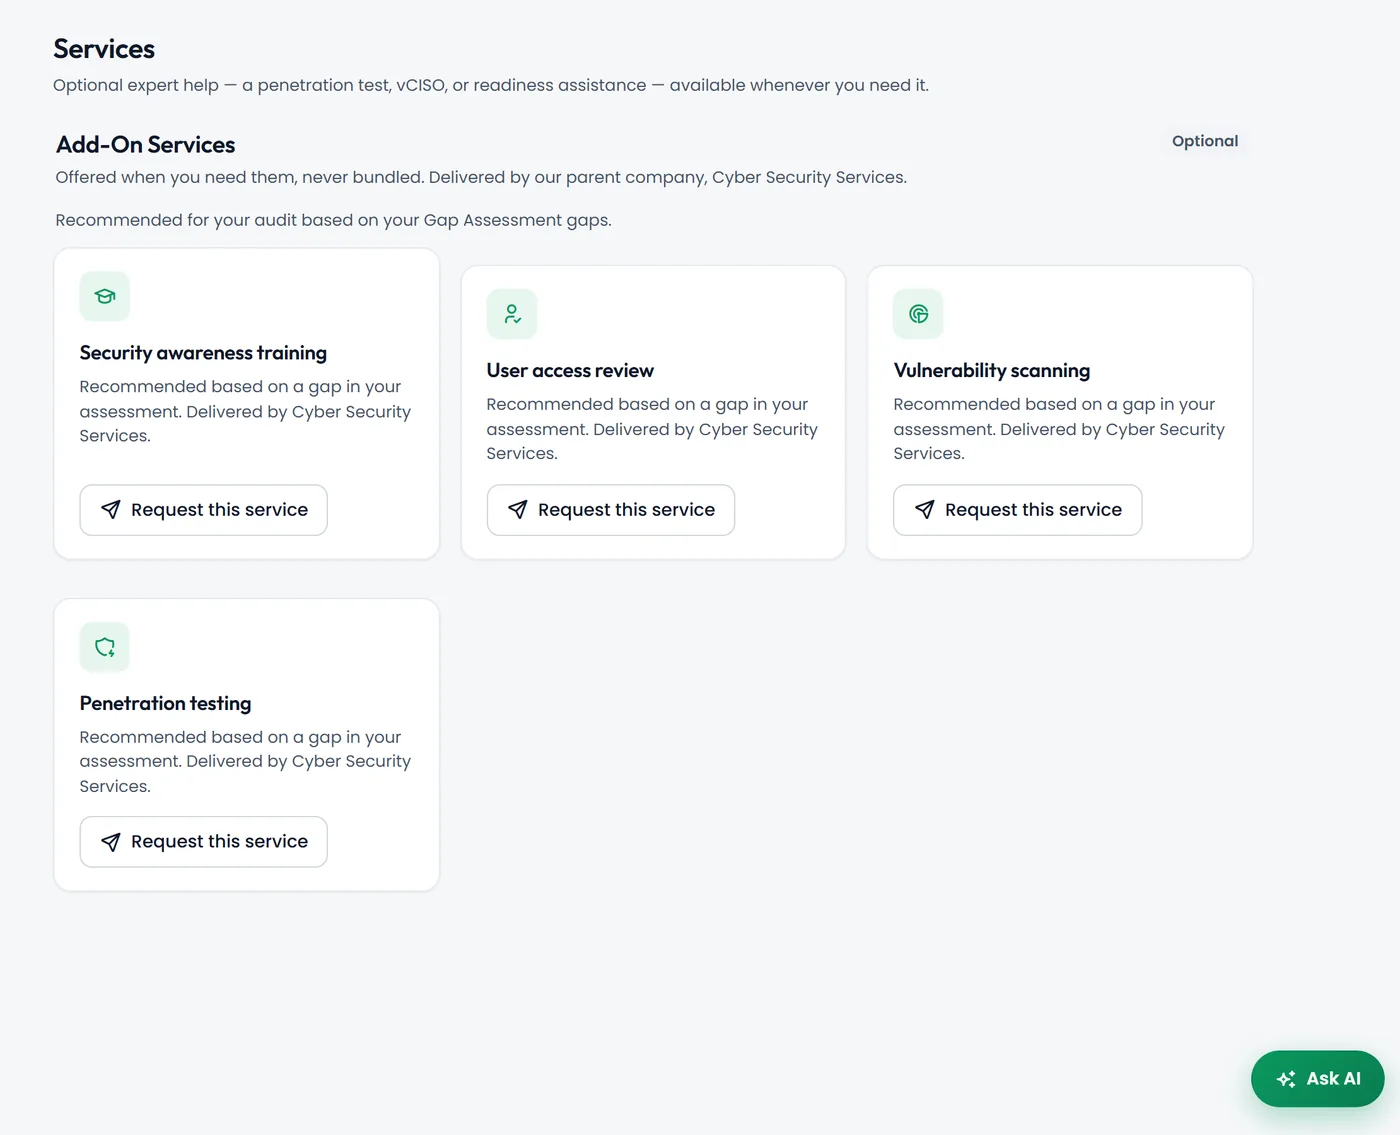
Audit › Services
Penetration testing, vulnerability management, vCISO and more from Cybersecurity Services, suggested when a gap calls for one.
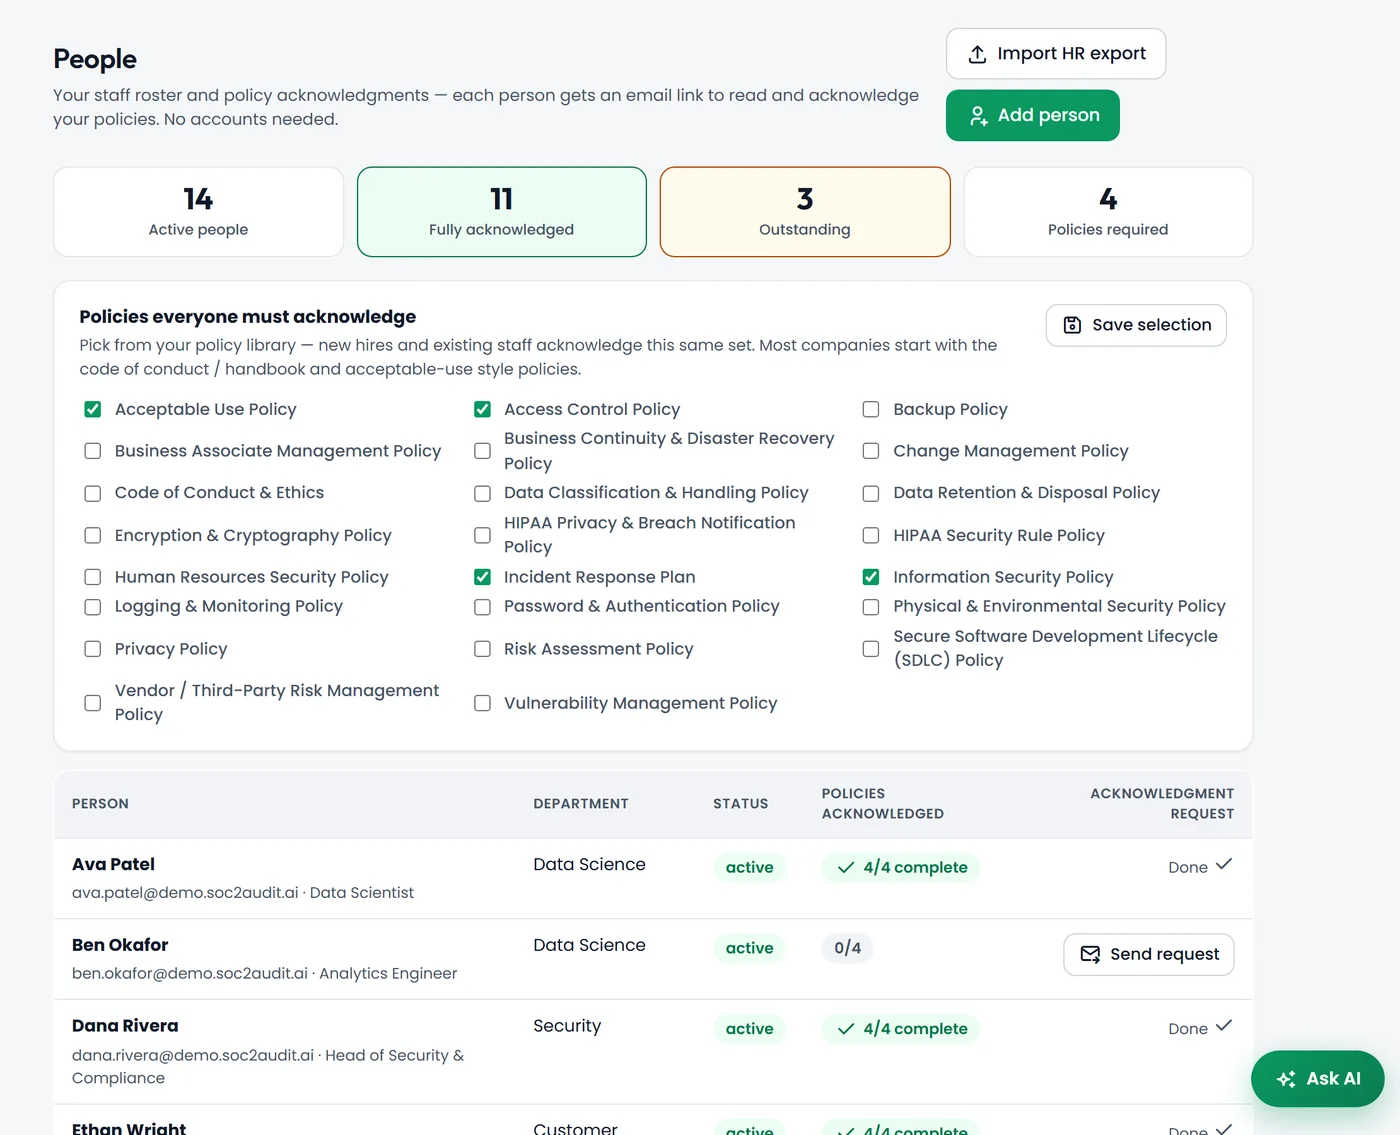
Company › People · AI-assisted
Staff acknowledge the policies you choose through a personal link. No account needed.
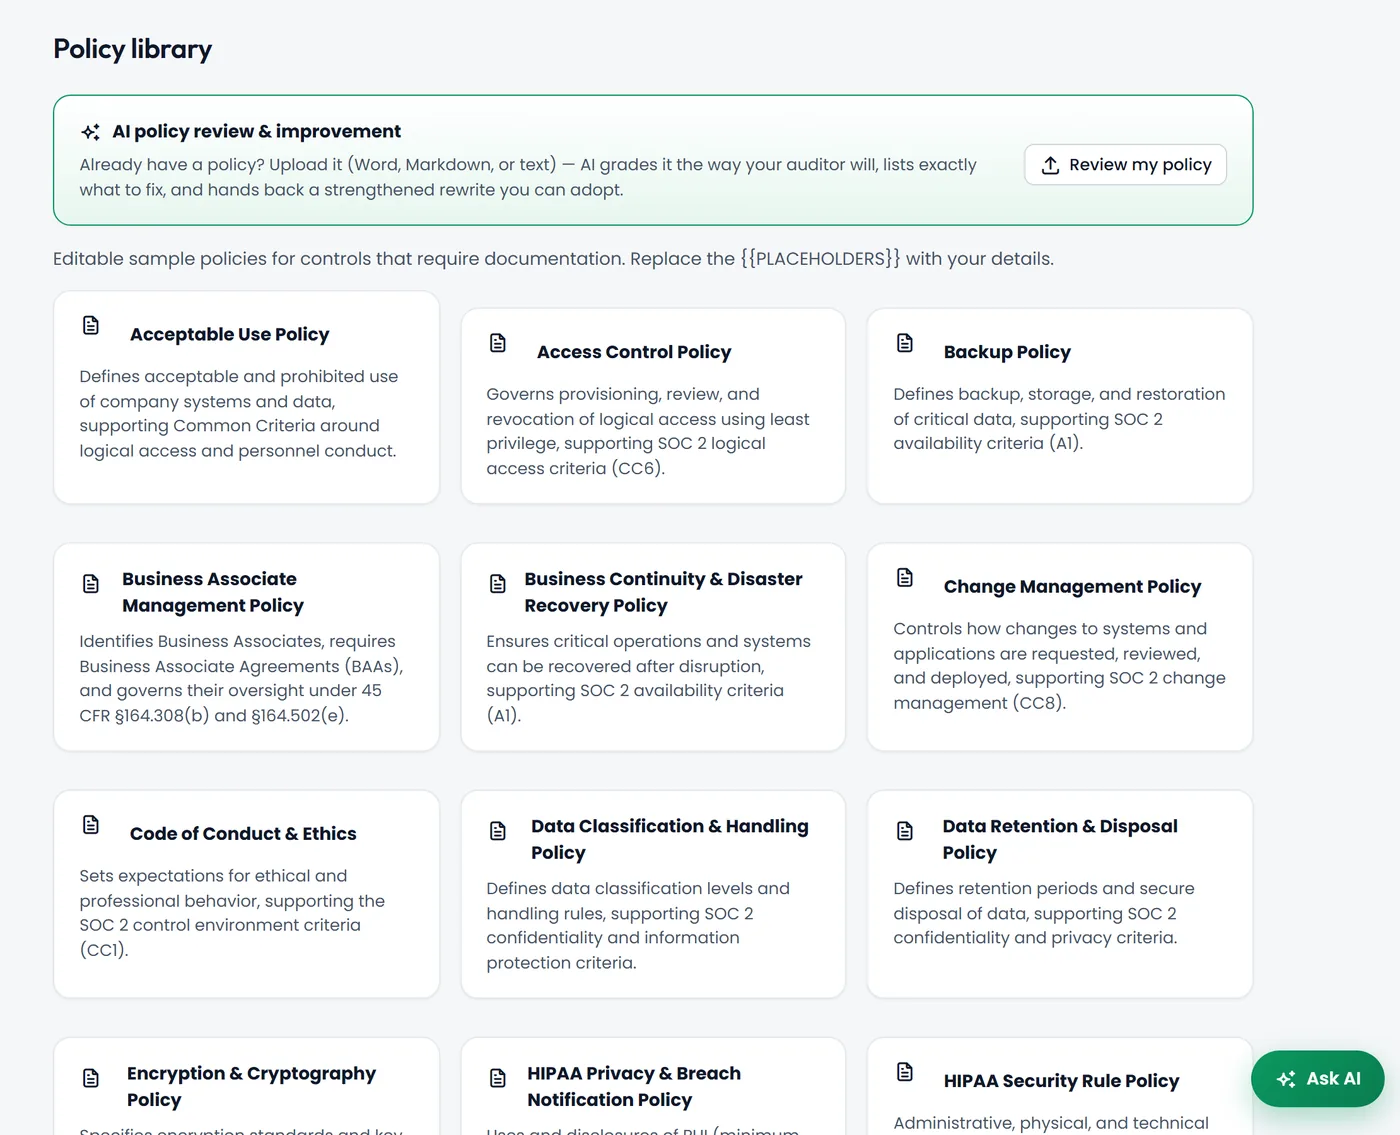
Company › Policy library · AI-assisted
Policy templates covering SOC 2 and HIPAA, alongside the policies AI wrote for you. Already have a policy? AI reviews it the way your auditor would.
Real screens from a demo company, Meridian Health, a fictional health-tech SaaS near the end of a SOC 2 Type II observation period. Click a screen to enlarge it.